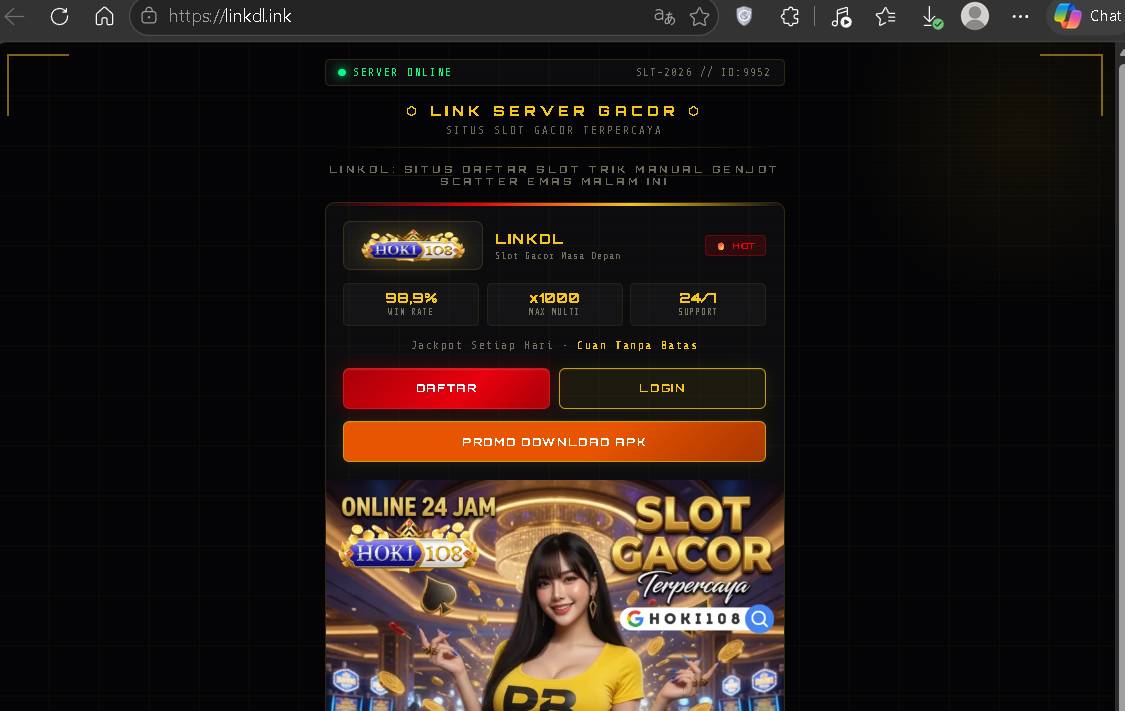
Linkdl.ink Review: Debunking the “Scatter Emas” Trick & APK Security Analysis
Landing on linkdl.ink displays an aggressive promotional banner featuring the headline: “LINKDL: SITUS DAFTAR SLOT TRIK MANUAL GENJOT SCATTER EMAS MALAM INI” beneath the Hoki108 brand banner. Accompanied by promises of an impossible “98,9% Win Rate” and “x1000 Max Multi,” the page presents itself as a specialized portal offering manual tricks to trigger slot jackpots.
In reality, linkdl.ink is an evasion gateway (link alternatif) designed to serve two primary purposes: harvesting payment deposits and distributing unverified Android APK packages outside official app stores. This technical safety review exposes the mechanics behind the “manual scatter” deception, the architecture of the portal, and the digital defense steps needed if your device has made contact with this domain.
Technical Identity & Network Profile: Linkdl.ink
| Forensic Metric | Technical Observation |
| Domain Identifier | linkdl.ink |
| Primary Network Association | Hoki108 / Server Gacor (GHOKI108 Q) |
| Hardcoded Backend Tag | SERVER ONLINE SLT-2026 // ID:9952 |
| Primary Conversion Objective | Direct APK Installation (PROMO DOWNLOAD APK) & Registration |
| Target Audience | Indonesian mobile users (QRIS, Dana, Local Banking) |
| Advertised Hook | “Trik Manual Genjot Scatter Emas” & 98.9% Win Rate |
| Risk Level | Critical — High-Risk Evasion Node & Malicious Sideloading Vector |
Suspicious Link or Courier SMS?
Verify URLs, APKs, or parcel alerts against our threat database before clicking.
The “Manual Scatter” Myth: Deconstructing the Linkdl.ink Deception
What distinguishes linkdl.ink from other syndicate mirrors is its explicit use of the “Trik Manual Genjot Scatter Emas” psychological hook.
How the Myth Works:
- The Claim: The site implies that players can manually time spins or use specific betting patterns to “force” the game’s algorithm into triggering high-paying “golden scatter” rounds.
- The Reality: Authentic slot mechanics run strictly on certified Pseudo-Random Number Generators (PRNG) hosted on protected game provider servers (such as Pragmatic Play or PG Soft). No manual timing, betting cadence, or client-side clicks can influence server-side PRNG outcomes.
- The Exploitation: By convincing users that winning is a matter of “skill” or “secret manual timing,” players blame themselves when they lose money rather than recognizing that the platform runs unregulated, house-rigged mathematics.
Key Security Threats on Linkdl.ink
1. Direct Delivery of Unverified Binaries (“Link Download”)
The domain naming convention itself—linkdl (short for Link Download)—reveals the syndicate’s primary intention: pushing visitors toward the “PROMO DOWNLOAD APK” button.
Downloading and installing third-party Android packages from an unverified .ink domain carries critical risks:
- Accessibility Privilege Abuse: Rogue casino APKs frequently request Accessibility Services, allowing background scripts to read text on the screen, monitor banking apps, and auto-grant application permissions.
- SMS Interception: Malicious binaries can capture incoming 2FA codes and One-Time Passwords (OTPs) sent via SMS, enabling unauthorized account takeovers on mobile banking and digital wallets (Dana, OVO, GoPay).
- Trojan Payloads: The downloaded file can act as a lightweight dropper that quietly fetches secondary surveillance tools onto the target device.
📧 Need Legal Assistance?
Contact the author for legal consultations, case evaluations, and professional inquiries.
In the upper status bar, linkdl.ink displays:
SERVER ONLINE | SLT-2026 // ID:9952This is not a real-time server diagnostic. It is a static template artifact identical to markers found across other syndicate landing pages. When telecommunications firewalls (such as Indonesia’s Trust Positif) block one domain, the operators deploy a new, inexpensive domain using the exact same front-end template to keep the traffic pipeline open.
3. Financial Extraction & Account Locks
Like its sister nodes, linkdl.ink operates with zero regulatory licensing (no PAGCOR, Curacao, or MGA oversight). If you deposit funds via bank transfer or QRIS:
- Small initial cashouts might be processed to fabricate trust.
- Substantial winning balances are frozen under arbitrary pretexts, such as “unmet turnover requirements” or “account verification delays”.
- There is no consumer protection board or ombudsman to petition for lost funds.
Visualizing the Linkdl.ink User Journey
Emergency Action Checklist: If You Interacted with Linkdl.ink
If you visited the site, entered details, or initiated a download, take these steps immediately:
- Step 1: Neutralize the Downloaded BinaryIf you downloaded the
.apkfile, do not tap it. Open your device file manager, navigate toDownloads, and permanently delete the file. If already installed, immediately toggle Airplane Mode, reboot into Safe Mode, revoke Accessibility/Admin permissions, and uninstall the app. - Step 2: Disconnect and ScanRun a full system scan using verified security software (Bitdefender Mobile Security or Malwarebytes) to detect hidden persistence scripts.
- Step 3: Secure Critical AccountsUsing a clean secondary device, change passwords on your banking apps, Google account, and mobile wallets. Migrate from SMS-based 2FA to software authenticators like Google Authenticator or Aegis.
- Step 4: Report to Anti-Scam RegistriesFile records with fraud prevention portals such as Indonesia’s IASC (OJK) via
iasc.ojk.go.idand Aduan Konten viaaduankonten.idto accelerate domain blacklisting and assist in freezing destination accounts.
Frequently Asked Questions (FAQ)
1. Is linkdl.ink scam?
Yes, linkdl.ink exhibits the operational hallmarks of an online gambling scam gateway. It lures users with fabricated promises of “manual scatter tricks” and guaranteed 98.9% win rates to extract deposits via QRIS and local bank transfers. The platform provides zero regulatory recourse when deposits or winnings are frozen.
2. Is linkdl.ink legit?
No, linkdl.ink is not a legitimate gaming platform. It lacks corporate registration, holds no valid gambling licenses (such as PAGCOR or Curacao), and functions purely as an unverified clone mirror for the Hoki108 gambling network.
3. What does “linkdl” mean in the domain linkdl.ink?
The “linkdl” prefix stands for Link Download, highlighting that the site’s primary delivery model is tricking mobile visitors into sideloading unsigned .apk software directly onto their phones rather than using a verified web browser or an audited app store.
4. Can the “Trik Manual Genjot Scatter” on linkdl.ink actually help you win?
No. Slot games run on cryptographic Random Number Generators that cannot be manipulated by manual tap sequences, betting tricks, or timing patterns. The “Trik Manual” slogan is a psychological marketing scheme designed to make losses feel like user error rather than mathematical certainty.
Installing the APK file exposes your phone to banking Trojans, credential theft, and SMS sniffers programmed to steal 2FA verification codes, compromising your banking apps and digital wallets.
Every safe click counts. If this post helped, a coffee gesture fuels more scam‑busting investigations.

Final Verdict
Safety Rating: CRITICAL RISK — AVOID
linkdl.ink is an evasion gateway operating on a disposable domain to distribute unverified Android software and channel users into an unregulated gambling network. Interacting with the site poses acute risks to device security and financial accounts. Never register, never transfer money, and never install application files from this portal.
Related Forensic Teardown
How Domain Churn Scams Keep Illegal Betting Rings Alive →Help Us Spread Awareness
Please share this article to spread awareness. Follow us on social media for more scam alerts.