Rajakuz.lol Investigation: Gacor180 Mirror Architecture, TLD Hopping & Security Analysis
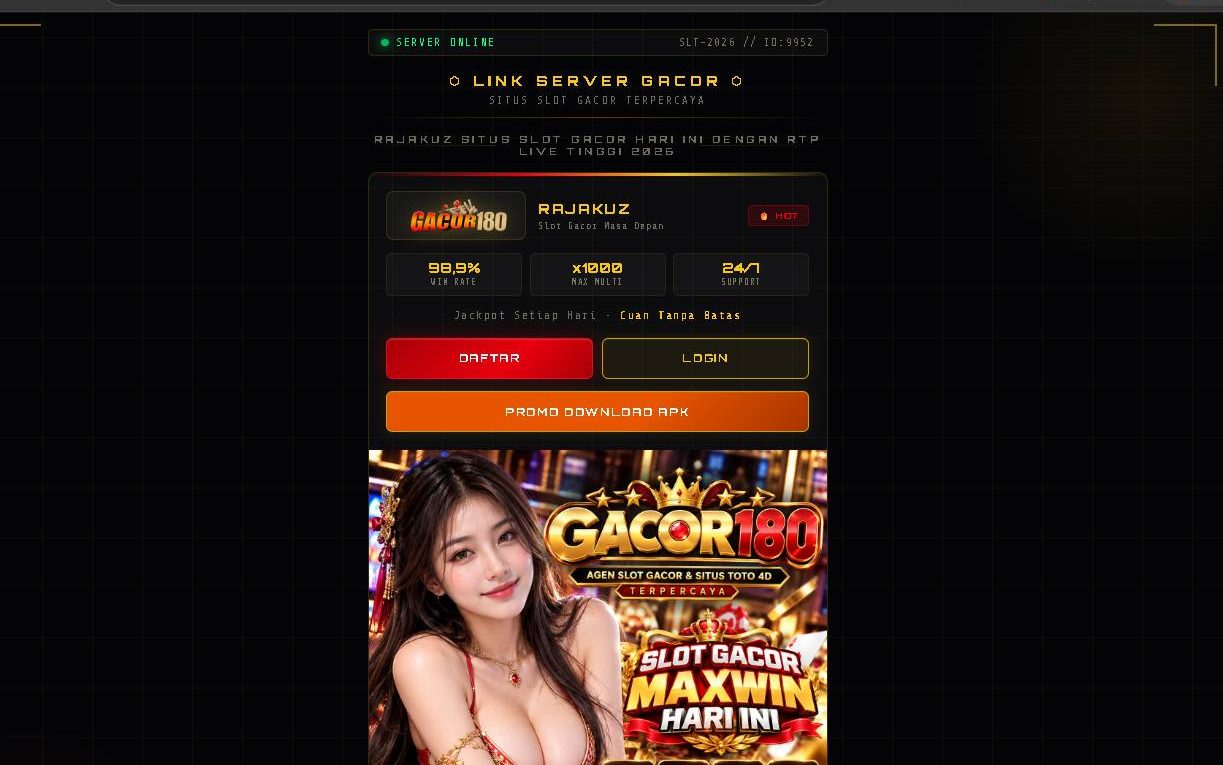
A new gateway in the Indonesian online gambling (judi online) ecosystem has surfaced under the domain rajakuz.lol. Featuring high-impact promotional banners declaring “RAJAKUZ SITUS SLOT GACOR HARI INI DENGAN RTP LIVE TINGGI 2026” and co-branded with Gacor180 (“AGEN SLOT GACOR & SITUS TOTO 4D TERPERCAYA”), the platform presents itself as a premier gaming portal.
Beneath claims of a “98.9% Win Rate” and “x1000 Max Multi,” this site is not an independent operator. It represents an infrastructure evolution by an established syndication network moving to generic top-level domains (gTLDs) to circumvent regional ISP filtering. This technical breakdown analyzes the backend mechanics of rajakuz.lol, the risks of its direct APK download prompts, and actionable steps to take if you have interacted with it.
Technical Profile: Rajakuz.lol
| Parameter | Observed Specification |
| Domain Asset | rajakuz.lol |
| Network Infrastructure | SERVER ONLINE SLT-2026 // ID:9952 |
| Associated Umbrella Brands | Gacor180 / Rajakuz |
| Monetization Engine | Unregulated Slot / Toto 4D Casino Mirror |
| Local Payment Methods Bait | Indonesian E-Wallets (QRIS, Dana, OVO, GoPay) & Local Bank Transfers |
| Primary Risk Vectors | Sideloaded APK Malware, Credential Harvesting, Financial Lockout |
| Overall Assessment | Critical Risk / High-Evasion Mirror Gateway |
Suspicious Link or Courier SMS?
Verify URLs, APKs, or parcel alerts against our threat database before clicking.
The TLD Shift: Why Operators Moved to .lol
Earlier waves of this automated mirror syndicate relied heavily on extensions like .fit and .ink. As national regulatory agencies—specifically Indonesia’s Ministry of Communication and Digital Affairs (Komdigi / formerly Kominfo)—accelerated DNS-level blacklisting via the Trust Positif database, operators adapted their domain generation strategies.
The adoption of rajakuz.lol demonstrates this shift:
- Circumventing Algorithmic Firewall Rules: Many automated web filters flag newly registered
.inkand.topdomains due to high historic abuse rates. Switching to.lolbypasses simple heuristic firewalls. - Burner Economics: Novel gTLDs frequently offer low initial registration pricing, allowing syndicates to deploy dozen-site batches that route traffic to the same central database until flagged.
- Keyword-Injected SEO Splogs: Malicious actors inject
.lolbacklinks into compromised WordPress themes and open directories to capture search volume from unvetted organic queries.
📧 Need Legal Assistance?
Contact the author for legal consultations, case evaluations, and professional inquiries.
Key Red Flags Identified on Rajakuz.lol
1. Hardcoded Cloned Infrastructure (ID:9952)
Inspecting the top header of rajakuz.lol reveals the status indicator:
SERVER ONLINE | SLT-2026 // ID:9952This is not a dynamic server check. It is a static, hardcoded HTML badge that matches the source layout found on other syndication nodes. The identical code base, paired with the same button sequence (Daftar, Login, PROMO DOWNLOAD APK), confirms the site is an automated front-end shell designed to channel registrations directly into a central offshore database.
2. The Live RTP Manipulation Strategy
Rajakuz.lol markets itself around “RTP Live Tinggi 2026” alongside an advertised 98.9% Win Rate.
Legitimate, regulated slot software uses cryptographic Random Number Generators (RNG) with fixed Return to Player rates certified by independent testing labs (such as eCOGRA, iTech Labs, or BMM Testlabs) at 92%–96%.
Promoting a permanent 98.9% payout rate is a mathematical impossibility for any functional casino. In mirror networks, “Live RTP” metrics are arbitrarily tuned by the operator to simulate “hot” periods, encouraging players to deposit during perceived winning streaks.
3. The PROMO DOWNLOAD APK Threat Vector
The landing page places heavy visual emphasis on a “PROMO DOWNLOAD APK” button. Sideloading untrusted application packages directly from a browser bypasses Android’s built-in Google Play Protect screening, exposing devices to significant vulnerabilities:
- Accessibility Service Hijacking: Malicious APKs request accessibility permissions under the guise of “game acceleration” or “lag-free play.” Once granted, the application can observe screen taps and input fields.
- SMS & 2FA Interception: Malware targets incoming SMS streams to harvest One-Time Passwords (OTPs) generated during mobile banking, Dana, or GoPay transactions.
- Persistent Background Daemons: Rogue APKs maintain hidden services that persist even when the browser or application window is closed.
Every safe click counts. If this post helped, a coffee gesture fuels more scam‑busting investigations.

The Rajakuz.lol User Journey & Conversion Trap
- Step 1 (Inbound Routing): Users reach the domain through parasite SEO redirects, spam comments, or cloaked search results.
- Step 2 (The Behavioral Hook): The interface pushes low barrier-to-entry terms (promising fast multipliers and round-the-clock service).
- Step 3 (Extraction & Lockout): Once a deposit is confirmed via QRIS or virtual account, withdrawal requests face obstacles: mandatory turnover escalations, sudden “system maintenance” errors, or total account termination without recourse.
Technical Incident Response (If You Interacted with Rajakuz.lol)
If you accessed the site, submitted credentials, or downloaded files, follow these containment steps:
Immediate Device Decontamination
- Switch on Airplane Mode: Disconnect Wi-Fi and mobile data immediately to prevent an active sideloaded APK from exfiltrating data to external command-and-control (C2) servers.
- Reboot into Safe Mode: On Android, hold the power button, then tap and hold Power Off until the Reboot to Safe Mode prompt appears. This prevents third-party apps from running on startup.
- Revoke Privileged Access:
- Go to
Settings$\rightarrow$Security$\rightarrow$Device Admin Apps. Revoke permissions for any unfamiliar services. - Go to
Settings$\rightarrow$Accessibility. Ensure no unverified gaming services have screen-reading permissions enabled.
- Go to
- Uninstall the File: Delete the APK from
Settings$\rightarrow$Apps, and delete the source installer from yourDownloadsdirectory. - Run Endpoint Scans: Reboot normally and perform a deep scan using an established mobile security tool (Bitdefender, Sophos, or Malwarebytes).
Credential & Banking Containment
- Reset Reused Passwords: If the password entered on the
Daftarform matches any email, banking, or e-commerce accounts, update those credentials immediately from a separate, clean device. - Migrate from SMS OTPs: Transition critical accounts from SMS-based verification to app-based authenticators (such as Aegis or Google Authenticator) to protect against SMS-intercepting malware.
- Report Unrecognized Charges: If money was transferred via bank transfer or QRIS, immediately contact your payment institution’s fraud unit. Reference an unauthorized transaction to an illicit gateway and request an immediate recipient block and case reference number.
Frequently Asked Questions
Is Rajakuz.lol scam?
Yes, Rajakuz.lol displays the defining characteristics of an unlicensed gambling clone trap. It operates without regulatory transparency, uses fabricated win-rate figures to drive deposits, and distributes untrusted APK files that present severe risks to mobile devices and financial accounts.
Is Rajakuz.lol legit?
No, Rajakuz.lol is not a legitimate gaming platform. It lacks accreditation from established gambling commissions (such as PAGCOR, Curacao eGaming, or MGA), conceals corporate ownership, and functions strictly as a temporary evasion mirror for the unregulated Gacor180 network.
Why does Rajakuz.lol feature the Gacor180 brand?
The domain acts as an alternative entrance (link alternatif) for the Gacor180 network. When primary domains are blocked by Indonesian ISP filters, syndicates deploy domains like Rajakuz.lol to capture incoming traffic and channel users into their backend payment systems.
Can you safely install the Rajakuz.lol APK?
No. Installing .apk packages from unverified third-party websites bypasses mobile security sandboxes. Sideloaded casino files frequently conceal banking Trojans, background keyloggers, or SMS-sniffing tools designed to capture banking credentials and OTP codes.
Final Safety Assessment
Status: CRITICAL RISK — AVOID
Rajakuz.lol is a high-evasion mirror portal designed to route traffic into an unregulated online gambling backend while exposing mobile users to unverified APK payloads. Do not register, do not submit personal contact details, and do not execute deposits through this gateway.
Related Forensic Teardown
How Domain Churn Scams Keep Illegal Betting Rings Alive →Help Us Spread Awareness
Please share this article to spread awareness. Follow us on social media for more scam alerts.