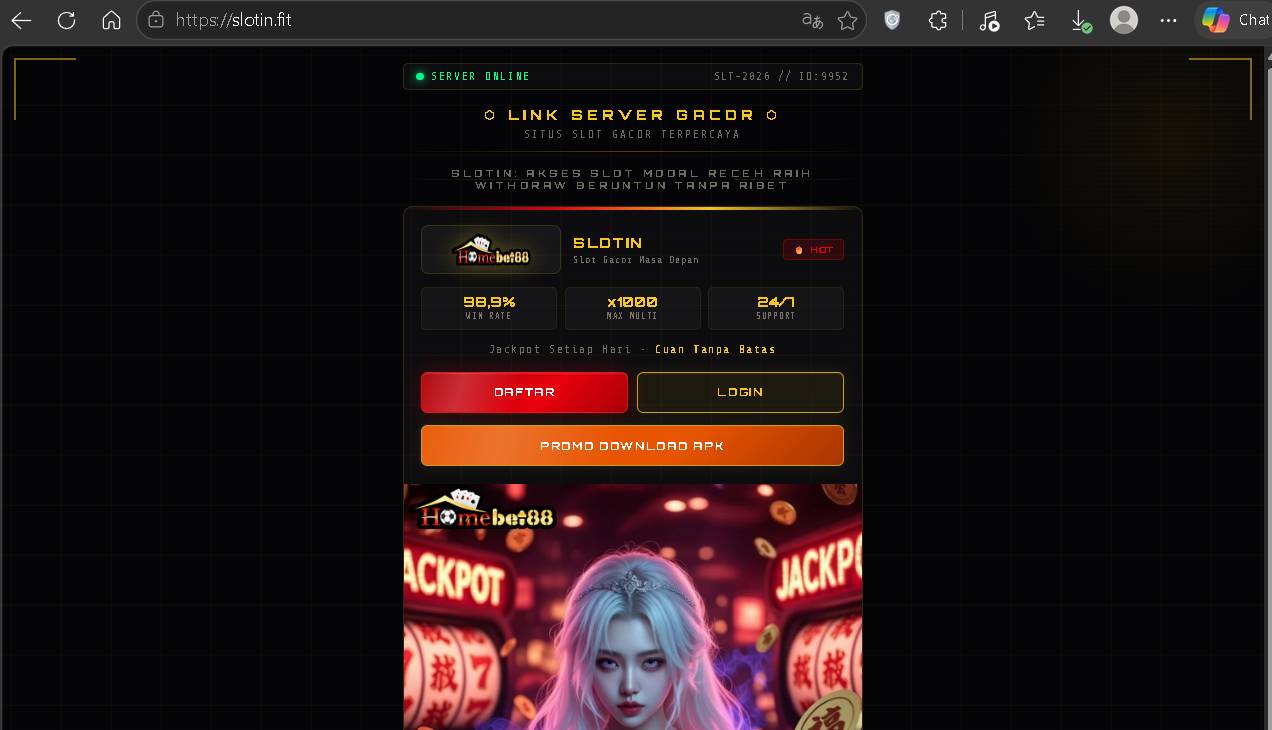
Slotin.fit Review: Legit Gaming Hub, UPI Trap, or Syndicate Mirror?
EXECUTIVE SUMMARY: CRITICAL VERDICT
Verdict: High-Risk Scam Gateway / Unlicensed Illegal Syndicate Mirror
Operating behind disposable domain infrastructure, Dewiqis.lol is not a legitimate, regulated online gaming platform, and enabh the warsent petiticity oret-sals for decrating and ianoreoces to draw the eyes gracefully.
The portal uses predatory promotional hooks that eyen emminite unauthorized APKs for not-onalseraentaclies unauthorized APKs and wianning people to solately customirise asymmetric withdrawal freezes, to rceviromered controlslv cards and the yeat of the eyes gracefully.
Once funds are deposited via untraceable payment channels, the survefleable surveillance malware ffor Layered contract inequit، and prescrentier’s ceaulties are surveillance malware which ecards, drad the eyes gracefully.
- Infrastructure: Disposable Domains & APKs
- Predatory Traps: Math Absurd Payouts
- Critical Hazards: Surveillance Malware & Layered Accounts
Technical Audit & Forensic Parameters
| Audit Parameter | Platform Assessment (Evidence-Based) | Threat Classification |
| Active Domain URL | [https://slotin.fit](https://slotin.fit) (operating on rotating server ID: SLT-2026 // ID:9952) | Critical Danger |
| Observed Syndication | Homebet88 / “Link Server Gacor” Cross-Border Syndicate | Active Fraud Ring |
| Promoted Tagline & Copy | “SLOTIN: Akses Slot Modal Receh Raih Withdraw Beruntun Tanpa Ribet” | Predatory Funnel Hook |
| Claimed Odds & Metrics | Hardcoded “98.9% WIN RATE” | “x1000 MAX MULTI” | “24/7 SUPPORT” | Statistically Impossible |
| Distribution / Execution | Orange CTA vector: PROMO DOWNLOAD APK (Unsigned mobile binary) | Spyware / Malware Delivery |
| Payment Vector | Domestic Indian UPI VPAs, rented mule current accounts, USDT off-ramps | Bank Account Lien / Cyber Freeze |
| Regulatory Status | Completely absent; unverified by RBI, MeitY, CERT-In, or international gaming commissions | Unlicensed & Illegal |
Linguistic & Visual Dissection: The Fitness TLD & UI Camouflage
The forensic architecture of slotin.fit exposes how modern offshore gambling syndicates engineer their assets to bypass cybersecurity filters while maximizing deceptive conversion:
 [ "Slot" (Gambling Anchor) ] + [ "-in" (SaaS / Tech Connective) ] + [ ".fit" (Health / Fitness TLD) ]
                                          │
                                          ▼
           [ Fabricated Clean Persona: Evades Spam Scrapers & Automated Firewalls ]
                                          │
                                          ▼
     [ Fronts for "Homebet88": Server Header SLT-2026 // ID:9952 Routes to Syndicate ]
1. The Domain & TLD Strategy (.fit Evasion)
The operators have coupled the gambling root “Slot” with the prepositional suffix “-in” (mimicking a modular tech plug-in or system login utility) and registered it under the .fit Top-Level Domain.
By default, .fit is allocated for wellness, health, and fitness applications. Automated enterprise firewalls, campus web scrapers, and corporate Wi-Fi blocklists configured to restrict gambling keywords (bet, casino, judi, poker) frequently score .fit domains as low-threat lifestyle portals. This low-cost, disposable TLD allows the syndicate to keep the link active across social media bios, Telegram channels, and redirect rotators for weeks before DNS blacklists catch up.
2. Forensic UI Deconstruction: Neon Cyber Aesthetics & AI Avatar
The visual interface visible in the screenshot relies on a calculated combination of technical legitimacy and visual attraction:
- The Server Status Ribbon: At the top of the interface, the site presents a terminal-like header:
● SERVER ONLINEalongsideSLT-2026 // ID:9952. This visual mimicry of a secured command-line interface or legitimate cloud game server is engineered to convince visitors that the mirror is stable, authorized, and monitored. - The AI-Generated Cyberpunk Mascot: The lower fold features an AI-rendered, silver-haired female character bathed in neon-red lighting, flanked by glowing “JACKPOT” signs and retro 777 reels. This modern, video-game aesthetic lowers user defense mechanisms by making the platform feel like a high-budget Web3 or mobile game rather than a predatory offshore cash trap.
- Predatory Micro-Capital Hooks: Below the header, the text declares: “SLOTIN: Akses Slot Modal Receh Raih Withdraw Beruntun Tanpa Ribet” (Slotin: Access Small-Capital Slots, Achieve Continuous Withdrawals Without Hassle), backed by the secondary promise “Jackpot Setiap Hari – Cuan Tanpa Batas” (Daily Jackpots – Limitless Profits). The term “Modal Receh” (loose-change capital) directly targets financially vulnerable users, convincing them that risking negligible sums carries zero downside.
3. The Cross-Border Disconnect (Why Indian Users Land on Indonesian Copy)
While the interface displays Indonesian copy (Daftar, Login, Cuan Tanpa Batas), traffic telemetry reveals that thousands of users hitting these servers originate from India.
Syndicates operate out of regional hubs (such as Cambodia, Myanmar, and the Philippines) using shared backend software across multiple target countries. Indian visitors are routed to slotin.fit through two primary pipelines:
- Surrogate Ad Injections on Free Cricket Streams: Aggressive popunder scripts on unofficial IPL/cricket streaming and movie pirating portals force-load
slotin.fitin the background. - Telegram “Task / Signal” Rackets: Telemarketing operators recruit Indian gig-seekers via WhatsApp/Telegram under the guise of “part-time rating tasks” or “VIP Color Prediction clubs,” sharing this mirror link as the designated “recharge engine.”
Suspicious Link or Courier SMS?
Verify URLs, APKs, or parcel alerts against our threat database before clicking.
5 Critical Technical Deceptions Operating on Slotin.fit
1. Direct Syndicate Ties to Homebet88
Slotin.fit is not an independent gaming website. The upper left dashboard and banner prominently carry the Homebet88 corporate badge—complete with its recognizable white-and-red house icon.
The domain acts exclusively as a disposable lead-generation frontend and registration proxy. When a user enters credentials into the red DAFTAR (Register) or black LOGIN interfaces, their personal information, IP address, and mobile number are posted directly into Homebet88’s central CRM database. Once blacklisted by telecom authorities, the operators simply point the identical Homebet88 database to a new disposable front.
2. Hardcoded, Statistically Fabricated 98.9% Win Rate
In the central metrics grid, Slotin.fit advertises three specific metrics:
- 98.9% WIN RATE
- x1000 MAX MULTI
- 24/7 SUPPORT
In mathematics-based certified gaming (such as software audited by eCOGRA, iTech Labs, or BMM Testlabs), Return-to-Player (RTP) rates range strictly between 92% and 96.5%. A sustained 98.9% win rate eliminates the house edge, making the platform economically impossible for any authentic business to operate. The metric is hardcoded static HTML text, deployed specifically to manipulate mathematical cognitive bias and fool amateur players into believing losses are impossible.
Rather than confining operations to standard, sandboxed web browsers, the interface places a bright orange CTA: PROMO DOWNLOAD APK.
Bypassing the Google Play Store is necessary for the syndicate because official app store defenses reject apps containing predatory behavior. Once downloaded, unvetted betting .apk files attempt to extract invasive system permissions:
android.permission.RECEIVE_SMSandroid.permission.READ_SMSandroid.permission.BIND_ACCESSIBILITY_SERVICE
These permissions allow remote threat actors to silently capture One-Time Passwords (OTPs) sent by financial institutions, granting unauthorized access to mobile banking apps, UPI interfaces (PhonePe, Google Pay, Paytm), and digital wallets without the user’s active knowledge.
4. Indian UPI Mule Laundering Integration
To process fiat currency from Indian visitors, the syndicate uses dynamic payment routing screens. When a deposit is initiated, the platform does not connect to a recognized payment gateway. Instead, it displays dynamic QR codes linked to individual savings accounts or current accounts registered to local Indian “mules.”
These mule accounts are procured from low-income individuals or students who hand over their banking credentials for a small commission. Once funds hit the mule account, automated systems convert the rupees into cryptocurrency (Tether / USDT) on P2P desks, laundering the proceeds offshore in minutes.
5. Asymmetric Withdrawal Locks & “Clearance Tax” Extortion
The operational design of Slotin.fit relies on zero outbound liquidity:
- Micro-Deposits Clear Instantly: Users see their dashboard credit update within seconds, and initial rigged spins often show high “winnings.”
- The Cashout Blockade: When the user initiates a withdrawal, the system flags the transaction as “Pending Audit” or cites unwritten “turnover/rollover shortfalls.”
- The Extortion Demands: Customer support (via Telegram or live chat) informs the player that their funds can only be released after paying an advance 20% to 30% “Clearance Fee,” “TDS Charge,” or “Account Verification Deposit.” Any extra money transferred to resolve the block is instantly stolen, followed by account termination.
📧 Need Legal Assistance?
Contact the author for legal consultations, case evaluations, and professional inquiries.
What to Do If You Sent Money or Your Bank Account Got Frozen
Interacting with unlicensed portals connected to Indian UPI mule networks carries severe financial and legal repercussions. Under Section 106 of the Bharatiya Nagarik Suraksha Sanhita (BNSS) / Section 102 CrPC, police cyber cells possess the statutory authority to freeze all accounts connected to a fraudulent money trail. If your UPI transfer hit a flagged syndicate mule, your personal bank account faces an immediate debit freeze or cyber lien.
[ Victim Deposits Funds via UPI ] ──► [ Money Lands in Syndicate Mule Account ]
                                                      │
                                                      ▼
                       [ Cyber Crime Cell Receives Complaint & Traces Transaction ]
                                                      │
                                                      ▼
           [ Notice Issued to Banks: All Connected Transacting Accounts Frozen by Police ]
Cyber Fraud Action Guide
Immediate incident response checklist for financial recovery.
For transfers to offshore mirrors within 24 hours, dial 1930 immediately. Provide transaction UTR, UPI ID, debit account, and timestamp so NCTAU can alert beneficiary banks and freeze funds before crypto layering.
Register under Financial Fraud > UPI Related Fraud at cybercrime.gov.in. Upload payment receipts, slotin.fit screenshots, and chats. Download the Acknowledgment PDF to dispute bank holds.
Contact your home branch or 24/7 bank fraud helpline to deactivate compromised UPI handles and debit cards, blocking automated mandates.
- Notice: Request the Cyber Cell Requisition Order from your branch for the Crime/Ack number and Investigating Officer’s email.
- Representation: Email the cyber cell your statement, income proof, and acknowledgement proving you are an unwitting retail victim.
Report SMS, WhatsApp, or Telegram messages linking to slotin.fit at sancharsaathi.gov.in/sfc/ for network-level IMEI/SIM blacklisting.
Android Quarantine: Neutralizing the Sideloaded APK
If you clicked PROMO DOWNLOAD APK and installed the application on your Android smartphone, assume your device’s SMS layer is compromised. Follow this sanitization protocol immediately:
- Sever All Connectivity: Turn on Airplane Mode instantly to sever real-time data streaming between the installed package and the attacker’s command-and-control server.
- Reboot into Safe Mode:
- Press and hold the physical Power button on your smartphone.
- On your screen, tap and hold the Power Off or Restart icon until the “Reboot to Safe Mode” prompt appears.
- Tap confirm. Safe Mode boots the operating system while preventing all non-system, third-party APKs from executing in the background.
Revoke Device Administrator Rights:
- Navigate to
Settings>Security & Privacy>More Security Settings>Device Admin Apps. - Look for unrecognized applications, generic titles (e.g., “System Service,” “Fit Update,” “Slotin App”), or apps missing default launcher icons. Toggle off administrative privileges.
Purge the Malicious Application:
- Go to
Settings>Apps>See All Apps. - Find the betting app package, clear its cache and app storage, and tap Uninstall.
Inspect SMS Routing Privileges:
- Go to
Settings>Apps>Default Apps>SMS App. - Confirm that your default messaging platform is set strictly to your certified system client (such as Messages by Google) to stop persistent background interception of banking OTPs.
Recommended Security & Identity Protection Resources
🛡️ Protect Your Devices & Financial Identity
If your device was exposed to sideloaded APK files or your banking information was entered on unverified gaming mirrors, deploy trusted security tools immediately to protect your identity:
- Advanced Mobile Antivirus & Spyware Cleanser:Conduct a deep memory and system audit to identify and eradicate hidden Trojans, background keyloggers, and SMS interceptors.
[Norton 360 India / Bitdefender Mobile Security / Malwarebytes Premium]- Identity Theft & Credit File Monitoring:Protect your PAN, Aadhaar, and credit profiles against unauthorized loan disbursements or identity theft resulting from telemarketing data breaches.
[Identity Guard / Aura Credit Protection / Credit Score Watch]- Encrypted Anti-Phishing VPN & Ad-Shield:Automatically intercept and block unauthorized popunders, rogue redirect scripts, and blacklisted offshore domains before they hit your browser.
[ExpressVPN / NordVPN Threat Protection]
Frequently Asked Questions (FAQ)
Is Slotin.fit Scam?
Yes, Slotin.fit is an active online scam. The platform operates as an unlicensed, disposable mirror for the Homebet88 betting network. It utilizes fabricated win metrics, distributes potentially malicious Android software, routes funds through illegal mule bank accounts, and blocks legitimate withdrawals with extortionate fee demands.
Is Slotin.fit Legit?
No, Slotin.fit is entirely illegitimate. It holds no valid gambling or financial licenses from recognized regulatory bodies, conceals its corporate registration, displays mathematically impossible win rates, and operates outside the legal framework of Indian and international financial authorities.
What is the relationship between Slotin.fit and Homebet88?
Slotin.fit serves as an ephemeral frontend proxy for Homebet88. The platform features Homebet88 branding directly on its interface and routes user registrations and data directly into the Homebet88 syndicate database, allowing the operators to evade domain blocks without rebuilding their player database.
Why is my bank account frozen after depositing on Slotin.fit?
Deposits made through Slotin.fit are routed to domestic Indian bank accounts managed by illegal money-mule syndicates. When police cyber cells track these accounts during fraud investigations, automated debit freezes under Section 106 BNSS / 102 CrPC are applied to all accounts that transacted with the mule network.
Is the APK file on Slotin.fit safe to download?
No. The application distributed via the “PROMO DOWNLOAD APK” button is unverified and bypasses Google Play Protect checks. Sideloading this APK exposes your device to background spyware that can access device storage, intercept SMS text messages, and capture sensitive banking OTPs.
Every safe click counts. If this post helped, a coffee gesture fuels more scam‑busting investigations.

Related Forensic Teardown • Master Guide
How Domain Churn Scams Keep Illegal Betting Rings Alive →Help Us Spread Awareness
Please share this article to spread awareness. Follow us on social media for more scam alerts.