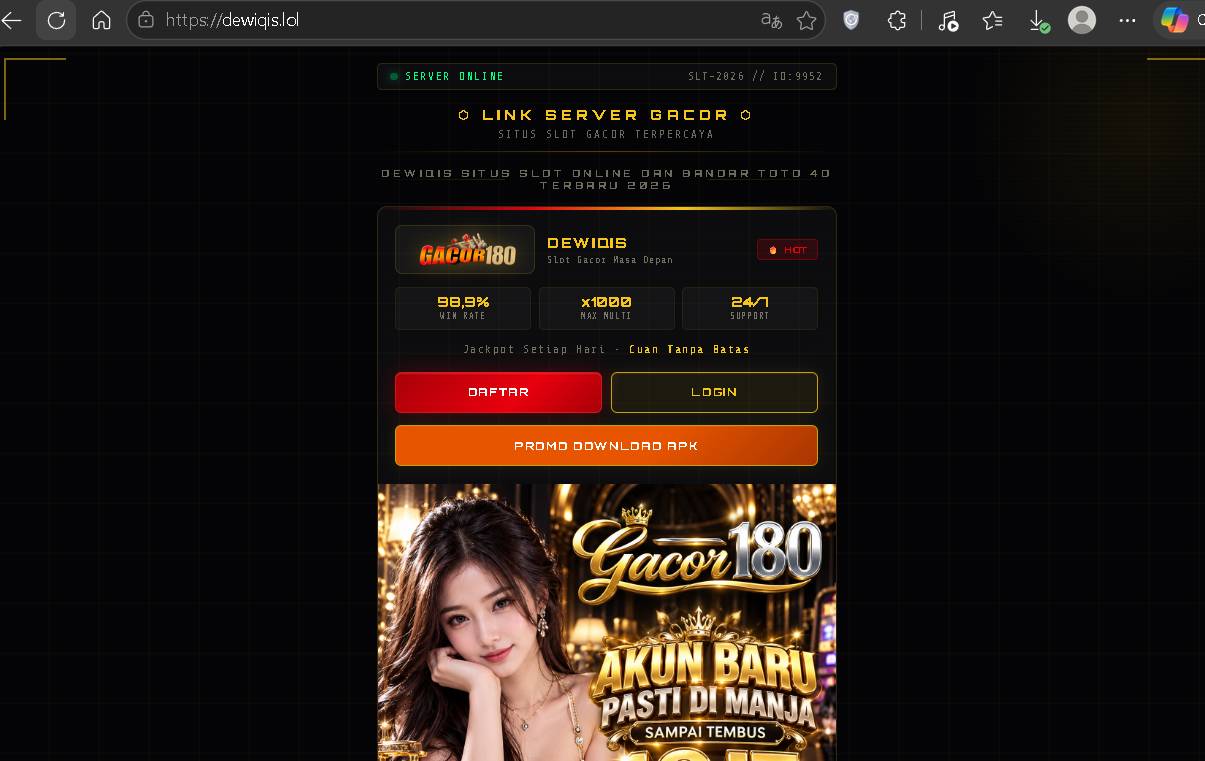
Dewiqis.lol Review: Legit Gaming Hub, UPI Trap, or Syndicate Mirror?
Executive Summary & Verdict Callout
Verdict: High-Risk Scam Gateway / Unlicensed Illegal Syndicate Mirror.
Operating behind disposable domain infrastructure, Dewiqis.lol is not a legitimate, regulated online gaming platform. Instead, it serves as an offshore, syndicated landing portal designed to funnel traffic into illegal betting platforms and unauthorized Android package kits (APKs).
The portal uses predatory promotional hooks—including mathematically absurd win rates, claims of guaranteed payouts, and unverified surrogate links—to lure retail users into high-risk deposit funnels. Once funds are deposited via untraceable payment channels or layered mule accounts, players are subjected to asymmetric withdrawal freezes, arbitrary clearance fee demands, and catastrophic device compromises via sideloaded surveillance malware.
Technical Audit & Forensic Parameters
| Forensic Parameter | Investigated Data / Observed Artifact |
|---|---|
| Active Domain URL | [https://dewiqis.lol](https://dewiqis.lol) |
| Observed Brand Identifiers | DEWIQIS / GACOR180 / SLT-2026 |
| Regional Language Taglines | “LINK SERVER GACOR – SITUS SLOT GACOR TERPERCAYA”, “DEWIQIS SITUS SLOT ONLINE DAN BANDAR TOTO 4D TERBARU 2026”, “Slot Gacor Masa Depan”, “Jackpot Setiap Hari – Cuan Tanpa Batas”, “AKUN BARU PASTI DIMANJA SAMPAI TEMBUS” |
| Fabricated Metrics & RTP | 98,9% WIN RATE |
| Telemetry / Tracking Header | SERVER ONLINE |
| Primary Interaction Buttons | DAFTAR (Register), LOGIN, and highlighted PROMO DOWNLOAD APK |
| Target Payment Vectors | P2P Mule Bank Accounts, Dynamic Layered UPI VPAs, Untraceable USDT/TRX Crypto Wallets |
| Distribution / Hijack Vector | Sideloaded third-party Android APKs, Telegram channel redirectors, surrogate pirated streaming ads |
| Licensing & Regulatory Status | Unlicensed & Unregulated; zero compliance under CERT-In, RBI payment aggregator directives, or global gaming regulators (MGA/UKGC). |
Suspicious Link or Courier SMS?
Verify URLs, APKs, or parcel alerts against our threat database before clicking.
Linguistic & Visual Dissection (Evidence-Based Forensic Analysis)
The Disposable TLD Strategy (dewiqis.lol)
The platform’s choice of the .lol top-level domain (TLD) is a textbook tactic in evasion-heavy cyber syndicates. Low-cost, non-standard TLDs like .lol, .top, and .vip are frequently churned in bulk. Operators purchase hundreds of cheap wildcard subdomains and algorithmic variations (such as dewiqis.lol, dewiqis.vip, etc.) to stay one step ahead of domain blacklists, corporate web firewalls, and telecom-level URL filtering enforced by internet service providers (ISPs). When law enforcement or automated crawlers flag and sinkhole one endpoint, traffic is instantly rerouted to another mirror domain with identical landing code.
       [Surrogate Ads / Social Media Bait]
                        │
                        ▼
[https://dewiqis.lol]
(Disposable .lol Gateway) │ │ [DAFTAR / Web Login] [PROMO DOWNLOAD APK] │ │ ▼ ▼ Mule Account UPI / Stealth Sideloaded APK P2P Deposit Churn (SMS/OTP Hijack & Spyware)
Deconstructing the UI Camouflage & Psychological Anchors
The landing page screenshot exposes several distinct visual markers engineered to bypass user skepticism:
- The “Gacor” Myth & High-RTP Manipulation: Prominently branding itself with the Indonesian slang term “Gacor” (indicating a slot machine that is “singing” or paying out constantly) and advertising an impossible “98,9% WIN RATE” along with a “x1000 MAX MULTI”, the interface targets the psychology of easy financial gain.
- The “Akun Baru Pasti Dimanja” Lure: The graphic banner prominently displays an attractive, glamorous female model accompanied by the headline “AKUN BARU PASTI DIMANJA SAMPAI TEMBUS” (promising that “new accounts are guaranteed to be spoiled until they hit the jackpot”). This classic honeypot visual lowers cognitive suspicion and encourages immediate deposits under the false belief that new player algorithms are intentionally rigged in their favor.
- Telemetry Camouflage (
SLT-2026 // ID:9952): Displaying a fake green indicator labeled"● SERVER ONLINE"along with arbitrary backend IDs creates a false impression of stability, technical legitimacy, and secure enterprise infrastructure.
📧 Need Legal Assistance?
Contact the author for legal consultations, case evaluations, and professional inquiries.
The Cross-Border Proxy Arbitrage
Although the interface text is composed entirely in Bahasa Indonesia (“Situs Slot Gacor Terpercaya”, “Bandar Toto 4D”), these exact platforms are aggressively weaponized in multi-jurisdiction arbitrage scams across South Asia, particularly India.
Syndicates syndicate identical source templates through pirated movie streaming sites, sports mirror broadcasts, and Telegram promo bot networks. When Indian users interact with these portals, the payment rails adapt dynamically on the backend to solicit domestic payments via UPI VPAs and QR codes tied to domestic mule accounts. The operational infrastructure remains offshore, exploiting legal and geographical gray zones to make tracking and fund recovery exceedingly difficult.
5 Critical Technical Deceptions Behind the Dewiqis Funnel
1. The Syndicate Mirror Architecture
dewiqis.lol is not an autonomous gambling company; it is an ephemeral frontend node routed into an offshore syndicate cluster (often tied to regional operations like “Gacor180”). These syndicates deploy content delivery networks (CDNs) and rotating reverse proxies to hide the real origin IP addresses of their backends. If dewiqis.lol is taken down, user sessions and database records are instantly pointed to another throwaway host without disrupting the syndicate’s operational flow.
2. Algorithmic Rigging & Simulated RTP
Legitimate, audited online casinos employ certified Random Number Generators (RNG) evaluated by independent laboratories (such as eCOGRA, iTech Labs, or BMM Testlabs). The claimed 98.9% Win Rate on Dewiqis is mathematically unviable for sustainable commercial house margins and serves purely as deceptive marketing. The backend logic is deliberately rigged: new users are often fed simulated “wins” on paper balances to incentivize larger deposits, followed by aggressive algorithm adjustments that zero out balances during subsequent sessions.
3. The Trojanized APK (PROMO DOWNLOAD APK)
The prominent orange PROMO DOWNLOAD APK button presents a major device-security threat. By directing mobile visitors to sideload an unvetted .apk file outside the Google Play Store, the site bypasses Android’s safety sandboxing and Play Protect warnings. These trojanized gaming APKs frequently request dangerous permissions:
android.permission.RECEIVE_SMSandREAD_SMS: Permitting malicious background scripts to read, parse, and exfiltrate two-factor authentication (2FA) and banking One-Time Passwords (OTPs).android.permission.BIND_ACCESSIBILITY_SERVICE: Granting the APK arbitrary UI automation power to read screen content, intercept keystrokes, and silently authorize background financial transfers.
4. Shadow Ownership & Absence of Legal Recourse
The platform provides no verifiable corporate registry, no published physical headquarters address, no data controller disclosures under GDPR/DPDP, and no recognized gaming licenses (such as from the Malta Gaming Authority, UKGC, or Curaçao eGaming). Operators maintain absolute anonymity via privacy-masked WHOIS records and bulletproof hosting providers, leaving victims with zero legal recourse when disputes occur.
5. Asymmetric Withdrawal Traps & “Clearance Fee” Extortion
Deposits on the platform are credited near-instantly, but outgoing withdrawals run into intentional artificial roadblocks. When a user requests a payout, the platform flags the transaction with arbitrary technical errors—such as “turnover requirement unfulfilled,” “anti-money laundering account verification required,” or “customs tax clearance pending.” The user is instructed to pay an upfront “clearance fee” or “unlock deposit.” If paid, the syndicate pockets the additional money and terminates the account entirely.
5. Emergency Remediation & Financial Recovery
If you or someone you know has interacted with dewiqis.lol, submitted banking details, or processed transactions via UPI/Net Banking, prompt remediation is essential.
       [FINANCIAL COMPROMISE TIMELINE]
                      │
 0 - 2 Hours          ▼
 (Golden Hour)  [Call 1930 / cybercrime.gov.in]
                • Request immediate transaction lien
                • Provide UPI Ref / UTR / Transaction ID
                      │
 2 - 24 Hours         ▼
                [Bank Branch Visit & Grievance]
                • Request freeze of associated VPA
                • Lodge written dispute & get Acknowledgement
                      │
 Ongoing              ▼
                [Report Vectors & Address Liens]
                • Report scam communication on DoT Chakshu
                • Resolve Section 106 BNSS / 102 CrPC notices
The Golden-Hour Protocol (India)
- Dial 1930 Immediately: Call the National Cybercrime Helpline (1930) within the critical first two hours of an unauthorized or deceptive transaction. Inform the desk officer of the exact transaction reference number (UTR/UPI transaction ID), recipient UPI VPA, sending bank account, and timestamp.
- File an Official Incident Report: Submit a formal complaint on the National Cybercrime Reporting Portal (cybercrime.gov.in). Provide unedited screenshots of the transaction, the
dewiqis.lolinterface, chat logs with handlers, and the recipient payment details. Keep a printed copy of the formal Crime Reference Number (ACK Number).
Handling Cyber Cell Debit Freezes & Liens (Section 106 BNSS / 102 CrPC)
If your bank account experiences an unexpected debit freeze or financial lien, your account may have inadvertently interacted with an illicit money-mule chain used by the syndicate.
- Legal Basis: Police officers and state Cyber Cells have the authority to freeze suspicious bank accounts during investigations into cyber fraud networks under Section 106 of the Bharatiya Nagarik Suraksha Sanhita (BNSS), 2023 (formerly Section 102 of the Code of Criminal Procedure / CrPC).
- Remediation Steps:
- Visit your home bank branch and request the Notice Details: Obtain the name of the investigating Cyber Cell, the Police Station, the formal Case/Crime Number (FIR/CSR), and the Investigating Officer’s (IO) official email address.
- Draft a formal representation clearly stating your status as an aggrieved victim rather than an operating mule. Attach your 1930 cyber complaint receipt, bank statements showing outgoing debits, and screenshots of the fraudulent funnel.
- Submit this packet to the assigned IO and request a partial lien reduction or account unfreeze once they confirm your legitimate non-collusion status.
Reporting Communication Vectors on DoT Chakshu
Report any mobile numbers, SMS headers, or WhatsApp/Telegram accounts used to circulate links to dewiqis.lol on the Chakshu portal hosted on the Department of Telecommunications (DoT) Sanchar Saathi platform (sancharsaathi.gov.in). This initiates telecom-level blacklisting of the numbers used to distribute the scam.
Android Quarantine & Spyware Neutralization
If you clicked PROMO DOWNLOAD APK and installed any file from the site, your device must be quarantined immediately to prevent OTP theft and silent account takeover.
   [Step 1: Isolate] ──► Toggle Airplane Mode ON (Sever C2 Server Comms)
            │
   [Step 2: Safe Mode] ─► Boot Device into Safe Mode (Suppresses 3rd Party Apps)
            │
   [Step 3: Revoke] ────► Settings > Security > Device Admin Apps (Strip Rights)
            │
   [Step 4: Purge] ─────► Settings > Apps > Uninstall Rogue / Nameless APK
            │
   [Step 5: Reset] ─────► Reset Default SMS App & Clear Accessibility Permissions
- Sever Active Data Connections: Immediately turn on Airplane Mode to sever active Command-and-Control (C2) communication channels between the trojanized APK and the attacker’s server.
- Reboot into Android Safe Mode:
- Press and hold the physical Power button.
- Tap and hold the on-screen Power Off or Restart icon until the prompt “Reboot to safe mode” appears. Confirm by tapping OK.
- Safe Mode disables all third-party apps from executing background processes upon boot.
- Revoke Device Administrator Privileges:
- Navigate to
Settings$\rightarrow$Security & Privacy$\rightarrow$More Security Settings$\rightarrow$Device Admin Apps. - Check for any unfamiliar apps (often disguised as “System Update”, “Google Services”, “Slot Engine”, or appearing with blank/generic names). Toggle off and revoke their administrative permissions.
- Locate and Uninstall the Rogue Package:
- Go to
Settings$\rightarrow$Apps$\rightarrow$See all apps. - Inspect the entire list. Look for applications installed on the date you accessed the site, applications with blank icons, or apps bearing titles like Dewiqis, Gacor, SLT, or Casino.
- Select the application, tap Force Stop, select Storage & Cache $\rightarrow$ Clear All Data, and tap Uninstall.
- Reset Default SMS App and Accessibility Settings:
- Navigate to
Settings$\rightarrow$Accessibility. Verify that no rogue services have toggled accessibility interception privileges. - Go to
Settings$\rightarrow$Apps$\rightarrow$Default apps$\rightarrow$SMS appand ensure your device’s legitimate messaging tool (e.g., official Messages by Google) is the sole active default application.
Recommended Security Resources & Protection Tools
:::caution Security Advisory
When dealing with cross-border syndicates that employ automated credential-harvesting scripts and malicious sideloaded APKs, manual cleanup should be reinforced with professional security monitoring.
:::
- Mobile Antivirus & Malware Removal Tool:
Deploy a certified mobile security solution (e.g., Bitdefender Total Security, Malwarebytes Mobile, or Sophos Intercept X) to scan for hidden payloads, stalkerware scripts, and accessibility-hijacking binaries. - Identity Theft & Credit Monitoring:
If banking details or identity proofs were uploaded todewiqis.lolor shared with handler accounts, monitor your credit reports continuously via legal credit bureaus (such as CIBIL, Experian, or Equifax) for unauthorized loan inquiries or newly opened credit facilities. - Anti-Phishing VPN & Secure DNS:
Deploy a privacy-focused VPN equipped with DNS-level malicious domain blocking (such as NextDNS, Cloudflare 1.1.1.2/3, or ProtonVPN with NetShield) to automatically block requests to known throwaway TLDs like.lol,.top, and.vip.
Frequently Asked Questions (FAQ)
Is Dewiqis.lol Scam or Legit?
Dewiqis.lol is an outright scam. It is an unlicensed, offshore illicit gambling portal disguised as a reliable gaming hub. The site operates on disposable infrastructure, publishes false win-rate metrics, lacks any verified regulatory license, and uses high-risk sideloaded Android APKs designed to intercept private data and compromise user funds.
Is Dewiqis.lol Legit for Real Money Gaming?
No, Dewiqis.lol is completely illegitimate. It provides no consumer protection, no verified Random Number Generation (RNG) certificates, and no lawful corporate presence. Deposits made via UPI or alternative rails are routed through high-risk money-mule accounts, and users face arbitrary withdrawal freezes or extortion demands when attempting to cash out balances.
Why is my Indian bank account frozen after using sites like Dewiqis?
If your bank account was placed under a debit freeze or financial lien, it is likely because the funds you deposited or received were routed through bank accounts flagged in a criminal investigation. State Cyber Cells issue freeze directives to banks under Section 106 of the Bharatiya Nagarik Suraksha Sanhita (BNSS) / Section 102 CrPC to track and halt money-laundering pipelines run by offshore gambling syndicates.
What should I do if I installed the APK from Dewiqis.lol?
Disconnect your phone from the internet immediately by enabling Airplane Mode. Restart your device in Android Safe Mode, revoke any administrator access given to unfamiliar apps under your device’s Security settings, and completely uninstall the sideloaded application. Finally, change your online banking and primary account passwords from an uncompromised secondary device.
Can I recover money lost on Dewiqis.lol?
Recovery depends on acting as quickly as possible. If you report the transaction to the 1930 National Cybercrime Helpline and file a complaint on cybercrime.gov.in within the “golden hour” (the first 2 hours), the investigating cyber cell can notify the receiving bank or payment gateway to put a temporary hold on the funds before the syndicate moves them out of the destination mule account.
Every safe click counts. If this post helped, a coffee gesture fuels more scam‑busting investigations.

Related Forensic Teardown • Master Guide
How Domain Churn Scams Keep Illegal Betting Rings Alive →Help Us Spread Awareness
Please share this article to spread awareness. Follow us on social media for more scam alerts.