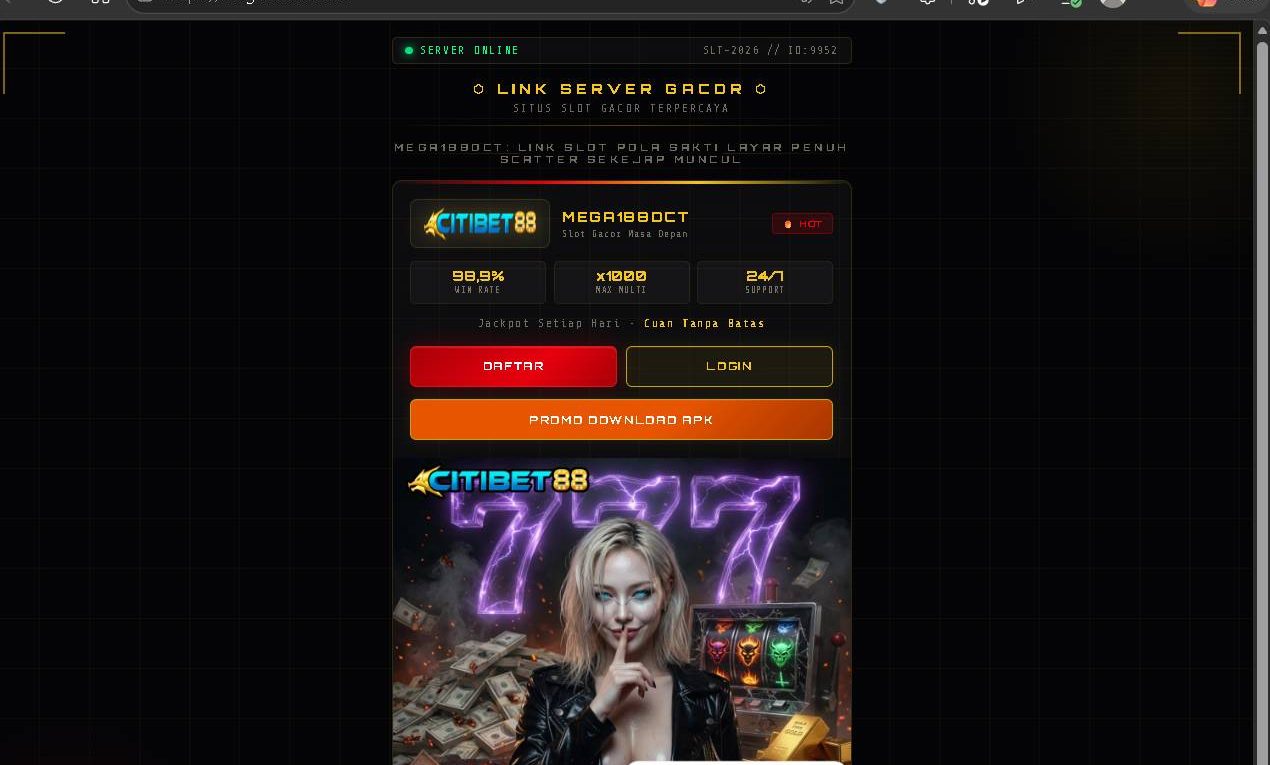
Mega188oct.site Review: Temporal Domain Spinning, Rigged Slot Emulation, and Capital Protection Guide
Mega188oct.site is an unregulated shadow betting mirror operating without statutory licensing charters, certified cryptographic fairness auditing, or legally protected client fund segregation.
The domain pairs the established black-market gambling brand “Mega188” with a temporal month-stamped string (oct) and an inexpensive generic top-level domain (.site).
This specific configuration serves as an ephemeral operational node in an automated domain-churning pipeline. These networks are engineered to bypass national telecommunications blacklists (such as Indonesia’s Kominfo/TrustPositif DNS sinkholes and regional ISP firewalls), game organic search engine ranking signals through calendar-based freshness exploits, and route unprotected player deposits into anonymous peer-to-peer money-mule accounts.
If you encountered Mega188oct.site via unsolicited direct messages on Telegram, automated invitations inside WhatsApp community groups, SMS spam blasts promising time-limited deposit matches, or compromised WordPress redirects advertising high-RTP “pola gacor” (winning patterns), exercise extreme caution.
Engaging with this URL exposes users to acute financial and digital hazards, including arbitrary withdrawal withholding, credential interception, device fingerprinting, and secondary social engineering fraud.
Suspicious Link or Courier SMS?
Verify URLs, APKs, or parcel alerts against our threat database before clicking.
Technical Deconstruction: The Temporal Domain-Spinning Infrastructure
Illicit iGaming syndicates operating in restricted jurisdictions face persistent disruption from law enforcement takedowns, ISP-level domain sinkholes, and search engine algorithmic de-indexing. To maintain continuous customer acquisition without establishing legitimate regulatory compliance, these rings deploy automated domain-generation engines.
Within this architecture, Mega188oct.site is not a permanent digital brand. It functions as an expendable front-end endpoint designed to exist for weeks or months before being replaced:
[ Calendar-Themed SMS / Social Bio Shunts / Compromised Doorways ]
                                │
                                ▼
                    [ Mega188oct.site ]  <── Disposable Monthly Node
                                │
        ┌───────────────────────┴───────────────────────┐
        ▼                                               ▼
[ Reverse-Proxy Data Harvester ]            [ Cloned Backend Slot Engine ]
        │                                               │
        ▼                                               ▼
Credential & E-Wallet Hijacking             The "System Desynchronization" Trap
Understanding how this setup operates reveals three primary threat mechanisms:
1. Calendar-Based Algorithmic Spinning
Unregulated syndicates routinely deploy temporal identifiers—such as month tags (oct, sep, nov) or seasonal keywords—to project an illusion of freshness. When regional authorities blacklist preceding iterations (such as Mega188sep), the operator’s automated nameserver infrastructure routes inbound traffic directly to Mega188oct.site. This seasonal naming convention also exploits user search behavior: prospective players frequently append current month tags to search queries when looking for accessible, unblocked login mirrors.
2. Reverse-Proxy Ingestion and Session Hijacking
Because unlicensed mirror operators maintain no legitimate software distribution partnerships with certified studio providers, platforms like Mega188oct.site frequently function as reverse proxies. When visitors submit credentials on the landing dashboard, client-side scripts intercept plaintext passwords, session cookies, telephone numbers, and banking details. These captured records are systematically cross-referenced against regional digital banking applications or compiled into marketable lead sheets circulated across underground trading channels.
3. Mule-Ring Payment Aggregation
Regulated operators route capital through licensed Payment Service Providers (PSPs) bound by Anti-Money Laundering (AML) and Counter-Terrorist Financing (CTF) mandates, keeping player funds in segregated escrow accounts. In contrast, Mega188oct.site routes transactions through:
- Shifting Peer-to-Peer (P2P) Accounts: Deposits are sent directly to temporary personal bank accounts belonging to recruited or compromised local third parties (“money mules”).
- Shell QRIS Barcodes: Dynamic and static QR codes registered to fictitious micro-enterprises that circumvent merchant-category verification.
- Burner Crypto Wallets: Rapid-hop cryptocurrency addresses that immediately funnel deposits into automated decentralized mixers or cross-chain bridges, permanently cutting off chargeback avenues.
📧 Need Legal Assistance?
Contact the author for legal consultations, case evaluations, and professional inquiries.
Technical Audit: Mega188oct.site vs. Regulated Standards
| Forensic & Governance Metric | Mega188oct.site Audit Findings | Regulated Authority Benchmark (MGA, UKGC, Curacao CEG) | Risk Severity |
| Statutory Gaming Charter | Completely absent; operating illicitly | Verifiable statutory license with searchable public registry | Critical |
| Corporate Identity & Registry | Shell entity; records masked behind privacy proxies | Transparent corporate entity with verified directors and physical address | Critical |
| Random Number Generator (RNG) | Uncertified, pirated server scripts | Independent cryptographic fairness audits (eCOGRA, BMM, GLI) | Critical |
| Banking Gateways | Ephemeral P2P bank mules and unvetted QRIS codes | PCI-DSS compliant acquiring banks with segregated player escrow | High |
| Dispute Resolution Channels | None; live chat operators terminate sessions at will | Enforceable Alternative Dispute Resolution (ADR) ombudsman | Critical |
| Data Protection Governance | Non-existent; user data shared across telemarketing rings | Strict compliance with statutory data privacy standards (GDPR, APPI) | High |
Modus Operandi: Predatory Traps Identified on Mega188oct.site
1. Counterfeit Game Scripts and Asymmetric Volatility
Legitimate online casinos never execute slot mathematics or live dealer logic on their own web servers; certified games run inside encrypted iframes delivered directly from studio Content Delivery Networks (such as Pragmatic Play, PG Soft, or Evolution Gaming), where server-side seeds cannot be altered.
Unlicensed mirrors like Mega188oct.site host cracked or reverse-engineered game software on untracked private servers. This enables predatory manipulation:
- The “Honeypot” Onboarding Phase: Micro-wagers and introductory bets are programmatically boosted to trigger frequent free spins and multiplier bonuses, generating artificial confidence.
- Algorithmic Throttling: Once account deposits scale up or higher stake thresholds are reached, server-side parameters suppress hit rates, making sustained play mathematically ruinous.
- Session Desynchronization: During bonus rounds or high-multiplier scatter sequences, the server intentionally introduces latency drops, forcing game crashes that void winning spin records.
2. The Advance-Fee “Turnover Verification” Trap
When an account amasses a significant balance and attempts an outbound withdrawal, the platform enforces systematic advance-fee barriers:
- The “Wagering Discrepancy” Flag: Live support claims backend risk algorithms identified “abnormal bet cadence,” “unauthorized third-party software,” or “unsettled session tokens.”
- The “Account Synchronization” Fee: The player is instructed to deposit an external verification charge—often 20% to 50% of the withdrawal total—to “clear the gateway.”
- The Reality: Regulated financial and iGaming institutions deduct applicable processing costs or withholding taxes directly from existing platform balances. They never demand external cash top-ups to authorize a withdrawal. Paying this fee does not unlock the funds; it merely deepens the financial loss before the account is terminated.
3. Secondary Identity Harvesting and Lead Monopolization
During onboarding on Mega188oct.site, users submit sensitive personal identifying information: legal names, phone numbers linked to electronic wallets, and personal bank account details.
- Unsecured offshore databases store these records without adequate encryption or security safeguards.
- Churned contact databases are monetized across illicit telemarketing networks, exposing victims to illegal micro-lending apps (pinjol ilegal), fraudulent investment schemes, and credential-stuffing campaigns across their personal digital accounts.
Every safe click counts. If this post helped, a coffee gesture fuels more scam‑busting investigations.

Domain Infrastructure & Digital Footprint Analysis
Technical inspection of the digital infrastructure underlying Mega188oct.site highlights operational characteristics typical of disposable setups:
- Short Registry Horizon: The domain was registered under a minimal one-year lease on a low-cost generic TLD (
.site). Disposable leases allow operators to discard the domain once security software, telecommunication watchdogs, and search engine algorithms flag it. - Obfuscated Infrastructure: Origin hosting IPs and geographic servers are shielded behind reverse-proxy routing networks (such as Cloudflare). This conceals physical server locations and complicates law enforcement inquiries.
- Non-Binding Terms of Service: The website lacks authentic legal terms, omitting corporate headquarters addresses, business registration numbers, dispute mechanisms, and designated data protection officers.
Incident Containment: What to Do If You Interacted with Mega188oct.site
If you have deposited capital, shared personal credentials, or registered an account on Mega188oct.site, immediate defensive measures are required:
1. Cease All Outbound Transfers
Do not send additional capital under any pretext. Demands for “system re-synchronization fees,” “KYC verification deposits,” or “tax releases” are advance-fee fraud tactics. Any additional funds sent to this site will be permanently lost.
2. Protect Compromised Financial Accounts
- If you transacted via local banking transfers, call your bank’s fraud department immediately. Report that you transferred funds to an unauthorized account affiliated with an unlicensed gaming portal, state the exact beneficiary account number, and request that it be flagged as a suspected money mule.
- Request your bank to issue a fresh virtual account token or adjust online banking login credentials to stop unauthorized automated clearinghouse debits.
- If payment card details were submitted, cancel the card immediately to block unauthorized tokenized charges.
- If your login credentials on Mega188oct.site match those of your primary email, banking portal, or digital wallets, change those passwords immediately using a separate, secure device.
- Enable Time-Based One-Time Password (TOTP) two-factor authentication via apps such as Google Authenticator or Microsoft Authenticator across all primary accounts. Avoid SMS-based two-factor authentication, as phone numbers entered on rogue portals are prime targets for SIM-swap attacks.
4. Guard Against Secondary “Asset Recovery” Scams
Victims of rogue platforms are often approached on messaging boards or social platforms by parties claiming to be “ethical hackers,” “blockchain tracers,” or “recovery specialists.”
- These individuals claim they can breach offshore servers or reverse banking transactions for an upfront fee.
- These are secondary scams targeting users who have already experienced financial loss. Independent third parties cannot legally or technically force refunds from illicit offshore operators. Legitimate recovery can only occur through official banking disputes, regulatory complaints, and formal law enforcement filings.
Frequently Asked Questions (FAQ)
No. Mega188oct.site holds no valid operating licenses, statutory permits, or regulatory oversight from recognized international gaming commissions (such as the Malta Gaming Authority, UK Gambling Commission, Curacao Gaming Control Board, or PAGCOR). It operates as an unauthorized offshore shadow domain.
What does the “oct” string in Mega188oct.site indicate?
Rogue gambling networks use temporal tags like “oct” to create fresh, disposable domain names that target search engine queries for unblocked access during specific calendar months, cycling out addresses once earlier mirrors are blacklisted.
Can I withdraw my deposited capital or winnings from Mega188oct.site?
Direct withdrawal from this platform is highly improbable once an administrative hold or wagering flag is introduced. Unregulated mirrors routinely stall payouts, demand advance clearance fees, or terminate accounts when users request fund extractions.
Why is customer support demanding a fee to unfreeze my account?
Demanding advance cash payments to unlock existing balances is an advance-fee fraud mechanism. Legitimate services deduct settlement fees directly from internal balances—they never require outside cash injections to process a cashout.
Are the slot machines and casino games on Mega188oct.site fair?
No. Because the backend software operates without mandatory independent lab audits (from agencies such as BMM Testlabs, GLI, or eCOGRA), site administrators can manipulate win rates, reduce RTP percentages, and alter game outcomes at their discretion.
Final Assessment
Mega188oct.site represents a critical financial and cybersecurity threat. The platform combines disposable domain structures, absent regulatory compliance, pirated software scripts, and predatory withdrawal traps. Do not deposit funds, register personal credentials, or share identity data with this site. Always rely on licensed, transparent platforms bound by established legal frameworks, provably fair gaming algorithms, and independent consumer arbitration bodies.
Related Forensic Teardown
How Domain Churn Scams Keep Illegal Betting Rings Alive →Help Us Spread Awareness
Please share this article to spread awareness. Follow us on social media for more scam alerts.