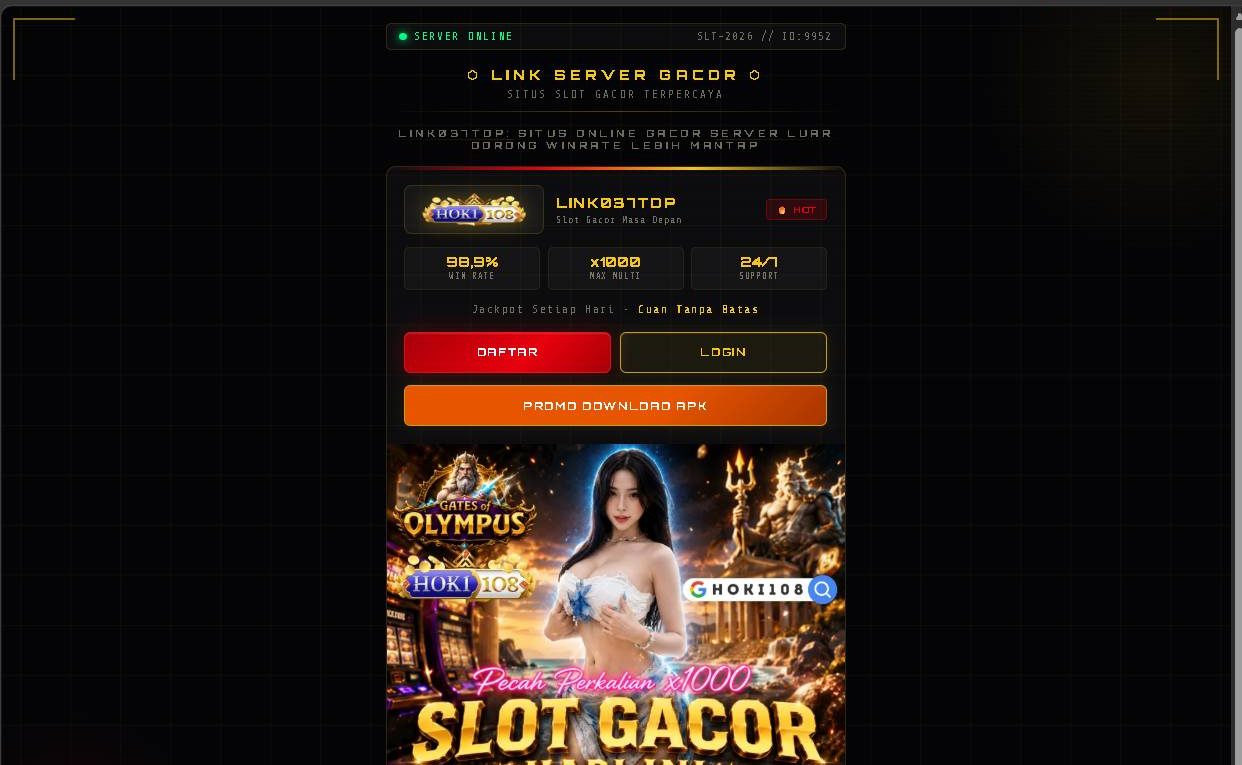
Link037top.live Review: Domain Flipping Forensics, Shadow Traffic Funnels, and Fund Recovery Protocol
Link037top.live is an unverified, black-market proxy mirror operating without statutory gaming licenses, verifiable corporate registration, or statutory consumer balance protections. Using a combination of generic navigation keywords (Link), sequential counter strings (037), high-intent promotion suffixes (top), and a low-cost live-streaming top-level domain (.live), this website functions as a transient endpoint within an automated offshore network.
These networks are engineered to bypass regional telecommunications firewalls (such as Indonesia’s Kominfo/Internet Positif sinkholes and telecom ISP filters), hijack organic search indexing, and channel unprotected retail deposits into untraceable payment mule chains.
If you arrived at Link037top.live via an automated direct message on Telegram, an invite link in a WhatsApp chat group, an unsolicited SMS containing an alleged VIP bonus code, or a search engine redirect promising exclusive slot RTP (Return-to-Player) leaks, exercise extreme caution. Engaging with this URL introduces severe vulnerabilities, including balance confiscation, unrecoverable peer-to-peer deposits, and the exposure of private banking credentials to secondary fraud syndicates.
Technical Deconstruction: The Link037top.live Threat Architecture
Unlike legitimate digital platforms that invest in consistent brand equity, persistent domain names, and visible corporate governance, Link037top.live belongs to a class of disposable domains generated by automated spinning scripts.
When telecommunications regulators or internet service providers block antecedent addresses (such as Link035top or Link036top), the operator’s DNS orchestrator automatically points the next sequential host in the pool—in this case, Link037top.live—to their offshore origin servers.
[ Automated Spam SMS / Social Bio Shunts / Search Cloaking ]
                            │
                            ▼
                [ Link037top.live ]  <── Disposable Alphanumeric Node
                            │
       ┌────────────────────┴────────────────────┐
       ▼                                         ▼
[ Session / Cookie Hijacking ]         [ Counterfeit iGaming Engine ]
       │                                         │
       ▼                                         ▼
Unauthorized E-Wallet Drains           Fabricated Turnover & Lockout ("Rungkad")
This disposable architecture carries out three predatory operations:
1. Dynamic Domain Flipping and DNS Cloaking
Disposable domains using generic numeric-string formulas are deployed as high-turnover proxies. The site deploys conditional HTTP routing: web scrapers, automated search bot crawlers, and IP subnets affiliated with international cybersecurity firms are served static landing pages or simulated error codes (HTTP 403/503). Meanwhile, residential mobile visitors routed from target geographic regions are instantly served an unmonitored betting terminal, effectively cloaking the site from automated regulatory detection.
Suspicious Link or Courier SMS?
Verify URLs, APKs, or parcel alerts against our threat database before clicking.
2. Reverse-Proxy Token Capture
Because platforms like Link037top.live lack legitimate direct software distribution agreements with accredited gaming studios, many operate as man-in-the-middle reverse proxies. When users log in, the front-end interface captures credentials, session authorization tokens, and personal telephone numbers. These harvested credentials can be leveraged to hijack balances on older affiliated nodes or packaged into high-intent phishing databases.
3. Layered Money-Mule Payment Ingestion
Certified digital merchants route payments through licensed payment service providers (PSPs) bound by Know Your Customer (KYC) and Anti-Money Laundering (AML) standards. Link037top.live evades standard banking scrutiny by relying on:
- Rotating Peer-to-Peer (P2P) Accounts: Deposits are directed to temporary personal bank accounts belonging to recruited or compromised local account holders (“money mules”).
- Static Shell QRIS Codes: Barcodes registered under fabricated small-business names that bypass commercial merchant categorization.
- Burner Crypto Wallets: Rapid-hop cryptocurrency addresses that immediately sweep deposited digital assets into decentralized cross-chain bridges or mixers, preventing direct chargebacks.
📧 Need Legal Assistance?
Contact the author for legal consultations, case evaluations, and professional inquiries.
Forensic Benchmark: Link037top.live vs. Regulated Financial Standards
Evaluating Link037top.live against standard regulatory requirements highlights critical operational deficiencies:
| Security & Governance Dimension | Link037top.live Audit Status | Certified Industry Standard | Risk Severity |
| Statutory Gaming License | None documented; operating illicitly | Tier-1 / Tier-2 License (MGA, UKGC, Curacao GCB, PAGCOR) | Critical |
| Corporate Disclosure | Ghost entity; shielded by anonymizing proxy registrars | Publicly registered business entity with transparent corporate directors | Critical |
| Software Provenance | Pirated, cracked API calls; no third-party hash validation | Hosted directly on vendor CDNs with publicly audited cryptographic seeds | Critical |
| Banking Infrastructure | Rotating P2P mule bank accounts, burner crypto wallets | PCI-DSS Level 1 compliant merchant processors with segregated escrow | High |
| Alternative Dispute Resolution | Completely absent; live chat terminates at administrative whim | Enforceable external arbitration (e.g., eCOGRA, IBAS, relevant ombudsmen) | Critical |
| Data Protection Governance | No verifiable privacy framework; data harvested for marketing lists | Strict compliance with data privacy mandates (GDPR, APPI, or local equivalents) | High |
Modus Operandi: Predatory Exploits Identified on Link037top.live
1. Counterfeit Game Scripts and Algorithmic Manipulation
Legitimate iGaming platforms do not host game logic on their internal web servers; instead, they serve authenticated iframes delivered directly from audited studio content delivery networks (such as Pragmatic Play, PG Soft, or Microgaming).
In contrast, unverified shadow domains frequently execute cloned, pirate-hosted game scripts. These unauthorized copies exhibit severe security flaws:
- Configurable RTP Profiles: Site administrators can manually dial Return-to-Player percentages below statistical norms, ensuring mathematically impossible long-term player profitability.
- Honeypot Volatility: New accounts or small deposits receive programmed bursts of micro-wins to engineer a false sense of legitimacy, enticing users to commit larger sums of capital.
- Multi-Multiplier Erasure: High-value payouts are frequently intercepted by intentional server-side latency scripts, causing game sessions to desynchronize right before a major winning round is finalized.
Every safe click counts. If this post helped, a coffee gesture fuels more scam‑busting investigations.

2. The Advance-Fee “Turnover Trap”
When a player attempts to extract accrued winnings from Link037top.live, customer support introduces multi-layered procedural barriers:
- The “Irregular Bet” Accusation: The platform claims that backend algorithms detected “abnormal betting patterns,” “arbitrage latency exploitation,” or “bonus turnover circumvention.”
- The Verification Surcharge: To resolve the manufactured flag, the user is instructed to deposit an external “verification fee” or “tax bond” equal to 20% to 50% of the withdrawal request. Legitimate platforms deduct applicable administrative fees directly from existing platform balances—they never demand outbound deposits to authorize payouts.
- Account Elimination: If the user sends the requested fee, customer support abruptly severs live communication, revokes access credentials, and blacklists the user’s IP range at the firewall layer.
3. Contact Siphoning and Secondary Cybercrime Exploitation
During the onboarding process on Link037top.live, users are required to supply their legal name, personal phone number, and primary bank details. On unregulated networks:
- These dossiers are retained without encryption on poorly configured offshore databases.
- Churned contact records are regularly compiled and sold on underground forums, exposing the victim to automated robocall scams, illegal peer-to-peer micro-lending apps (pinjol ilegal), and targeted WhatsApp social engineering attacks.
Infrastructure Footprint & Domain Red Flags
Technical analysis of Link037top.live reveals technical anomalies characteristic of ephemeral infrastructure:
- Minimal Registration Lifespan: The domain is secured under a standard one-year registration lease, indicating that the controllers have no intention of building sustainable domain equity.
- Aggressive Proxy Cloaking: Authoritative nameservers, web hosting origin IPs, and physical infrastructure details are obscured behind third-party reverse proxies (such as Cloudflare). This conceals the physical server coordinates from regional law enforcement agencies.
- Non-Binding Terms of Service: The platform lacks legally enforceable user terms, omitting corporate jurisdiction disclosures, registered company numbers, and verifiable arbitration clauses.
Emergency Protocol: What to Do If You Interacted with Link037top.live
If you have already deposited capital, shared personal credentials, or registered an account on Link037top.live, take immediate protective action:
1. Refuse All Further Demands for Capital
Under no circumstances should you deposit additional money to “clear an audit,” “unfreeze a pending balance,” or “pay tax clearances.” Demanding upfront cash to release funds is a classic advance-fee fraud tactic. Any additional capital sent to this operator will be permanently lost.
2. Secure Compromised Banking Channels
- If you transacted using online banking or virtual accounts (VA), contact the fraud operations division of your financial institution immediately. Report that you transferred funds to an account tied to an illicit, unlicensed platform and identify the recipient details as a suspected commercial money-mule account.
- Request your bank to refresh your digital banking tokens, issue new account numbers if direct access was exposed, and place an outbound monitoring hold on unverified third-party debits.
- If a payment card was used, request an immediate cancellation and card re-issuance to prevent unauthorized recurring tokenized charges.
Rogue operations exploit password reuse habits across unrelated digital platforms:
- If you used an email and password combination on Link037top.live that matches your primary email, banking portal, social media, or cryptocurrency accounts, change those passwords immediately using a secure, uncompromised device.
- Upgrade authentication across all sensitive platforms to time-based one-time password (TOTP) hardware security keys or authenticator apps (such as Google Authenticator, Microsoft Authenticator, or Yubikey). Avoid SMS-based two-factor authentication wherever possible, as phone numbers submitted to rogue domains are prime targets for SIM-swapping attempts.
4. Resist Secondary Asset Recovery Scams
Victims of illicit online platforms are frequently targeted on social networks, messaging channels, and web forums by fraudulent entities posing as “independent recovery firms,” “certified cyber investigators,” or “ethical hacking syndicates.”
- These operations claim they can tap into private offshore servers or reverse blockchain transactions for an upfront fee.
- In reality, private third parties have no legal authority or technical capability to seize assets from rogue offshore servers. Legitimate recovery can only proceed through official bank dispute mechanisms, regulatory complaints, and formal law enforcement filings.
Frequently Asked Questions (FAQ)
Is Link037top.live a licensed or legitimate online betting platform?
No. Link037top.live possesses no verifiable regulatory licensing, operational permits, or compliance oversight from recognized gaming commissions (such as the Malta Gaming Authority, UK Gambling Commission, Curacao Gaming Control Board, or PAGCOR). It operates as an unauthorized offshore shadow domain.
Why does Link037top.live use sequential numbers like “037”?
Illicit gambling syndicates employ sequential numerical formulas (such as 035, 036, 037) within their URLs to rapidly rotate domains. This allows operators to spin up fresh addresses and continue routing traffic whenever earlier mirrors are blocked by telecommunications firewalls or ISP filters.
Can I withdraw my deposited capital or winnings from Link037top.live?
Direct withdrawal from this platform is highly unlikely once an administrative delay or wagering flag is introduced. Unregulated mirrors frequently stall payouts, demand advance clearance fees, or terminate accounts when users request fund extractions.
Why is customer support demanding a fee to unfreeze my account?
Demanding advance cash payments to unlock existing balances is an advance-fee fraud mechanism. Legitimate financial and gaming services deduct any applicable settlement or administrative costs directly from internal platform balances—they never require outside cash injections to process a cashout.
Are the slot machines and casino games on Link037top.live fair?
No. Because the backend software operates without mandatory independent lab audits (from agencies such as BMM Testlabs, GLI, or eCOGRA), site administrators can manipulate win rates, reduce RTP percentages, and alter game outcomes at their discretion.
Final Assessment
Link037top.live is an unregulated, high-risk clone portal built to extract user deposits through pirated scripts and predatory withdrawal locks. The combination of concealed operator identities, disposable domain infrastructure, and lack of player protections makes interaction with this platform dangerous. Do not deposit funds, register personal credentials, or share identity data with this site.
Related Forensic Teardown
How Domain Churn Scams Keep Illegal Betting Rings Alive →Help Us Spread Awareness
Please share this article to spread awareness. Follow us on social media for more scam alerts.