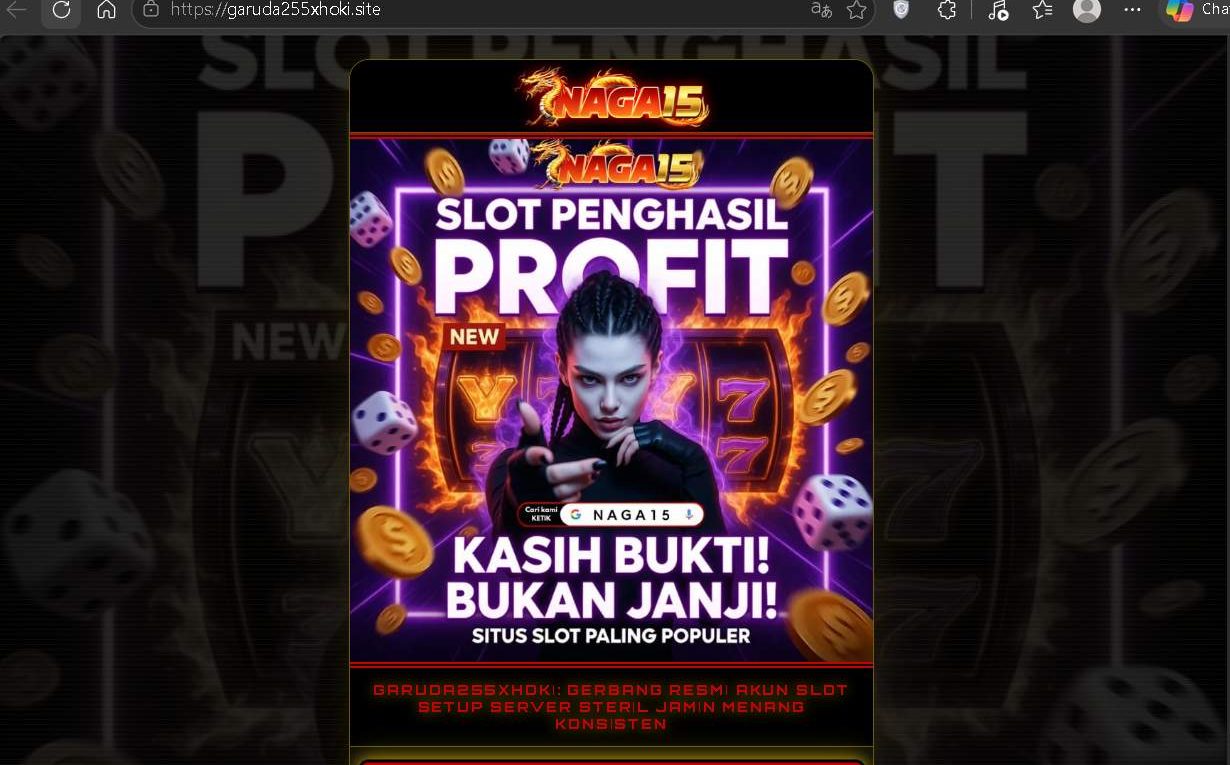
Garuda255xhoki.site Review: Algorithmic SEO Hijacking, Cloned iGaming Scripts, and Fund Defense Protocol
Garuda255xhoki.site is an unauthorized, high-risk black-market gambling mirror operating without recognized statutory gaming licenses, independent cryptographic fairness audits, or statutory consumer balance protections. Combining the cultural motif “Garuda,” sequential numerical counters (255), high-intent gambling buzzwords (xhoki, referencing the localized term for luck), and an inexpensive generic top-level domain (.site), this address forms an operational node within an offshore syndication network.
These setups operate to bypass regional telecommunications firewalls (such as Indonesia’s Kominfo TrustPositif filters and ISP DNS blocks), hijack high-volume search engine queries through automated parasite SEO, and lure retail depositors into untraceable payment pipelines.
If you arrived at Garuda255xhoki.site through automated WhatsApp blasts, spam SMS broadcasts, Telegram predictor groups, or compromised WordPress redirects promising “anti-rungkad” (anti-loss) slot algorithms or leaked admin RTP metrics, treat the site with extreme suspicion. Interacting with this domain exposes players to irreversible capital loss, manipulated game mathematics, and digital identity theft.
Technical Threat Profile: Anatomy of the Garuda255xhoki.site Network
Offshore black-market operators face continuous disruption from state cyber agencies, payment processor blacklists, and automated search engine de-indexing. To maintain uninterrupted cash inflow, syndicates deploy automated domain-generation engines. Garuda255xhoki.site is not a standalone enterprise; it is an ephemeral endpoint in a broader mirror matrix.
[ Compromised Web Redirects / Parasite SEO / Telegram Funnels ]
                               │
                               ▼
                   [ Garuda255xhoki.site ]  <── Ephemeral Mirror Node
                               │
        ┌──────────────────────┴──────────────────────┐
        ▼                                             ▼
[ Fake QRIS / Mule Account Ingestion ]      [ Tampered Slot & Togel Scripts ]
        │                                             │
        ▼                                             ▼
Irreversible Capital Dissipation            The "Pending System Audit" Lockout
Understanding its structural behavior reveals three predatory mechanics:
1. Parasite SEO and Automated SERP Hijacking
Platforms like Garuda255xhoki.site frequently deploy automated SEO cloaking scripts. Syndicates inject thousands of doorway pages into compromised governmental (.go.id), educational (.ac.id / .edu), and municipal websites using SQL injections or outdated plugin vulnerabilities. These compromised doorways silently forward organic Google search visitors directly to Garuda255xhoki.site, capturing traffic before search engines remove the hacked URLs.
2. Reverse-Proxy Game Framing and Altered RTP
Legitimate online casinos integrate slot games via encrypted server-to-server Application Programming Interfaces (APIs) connected to certified providers (such as Pragmatic Play, PG Soft, or Microgaming). Unlicensed mirrors like Garuda255xhoki.site run pirated scripts or route game sessions through illicit man-in-the-middle reverse proxies:
- Asymmetric Volatility: The operator can alter payout ratios. Initial sessions on low stakes often produce micro-wins to build false confidence.
- Winning-Streak Throttling: When wagers increase, backend configurations throttle payout triggers, ensuring the house edge is 100% over extended play.
3. Mule-Ring Payment Aggregation
Regulated operators route deposits through licensed Payment Service Providers (PSPs) subject to Know Your Customer (KYC) and Anti-Money Laundering (AML) statutory oversight. Garuda255xhoki.site routes player deposits through layered peer-to-peer (P2P) local bank transfers, burner static QRIS barcodes registered to fictitious micro-enterprises, or unmonitored cryptocurrency deposit addresses. Once deposited, automation scripts sweep funds across multiple mule accounts within minutes, rendering automated chargebacks and transaction recalls impossible.
Suspicious Link or Courier SMS?
Verify URLs, APKs, or parcel alerts against our threat database before clicking.
Technical Audit: Garuda255xhoki.site vs. Regulated Standards
| Forensic & Compliance Indicator | Garuda255xhoki.site Audit Status | Regulated Authority Standard (MGA, UKGC, Curacao CEG) | Risk Severity |
| Statutory Gaming Charter | None documented; operating illegally | Verifiable statutory license with public regulatory register | Critical |
| Corporate Identity & Registry | Shell operator; masked via privacy proxies | Publicly listed corporate entity with verifiable directors | Critical |
| Random Number Generator (RNG) | Uncertified pirated game copies | Audited cryptographic fairness (eCOGRA, BMM, GLI) | Critical |
| Banking Gateways | Ephemeral P2P bank mules & shell QRIS | PCI-DSS compliant acquiring banks and segregated balances | High |
| Dispute Resolution Infrastructure | None; support disconnects at will | Mandatory, legally binding Alternative Dispute Resolution (ADR) | Critical |
| Data Protection Standards | Non-existent; logs sold to telemarketing rings | Full compliance with statutory data privacy standards (GDPR) | High |
📧 Need Legal Assistance?
Contact the author for legal consultations, case evaluations, and professional inquiries.
Modus Operandi: Predatory Traps Deployed on Garuda255xhoki.site
1. The “VIP Tier / Admin Leak” (Bocoran Admin) Trap
A common funnel for Garuda255xhoki.site relies on social channels claiming to share insider “Pattern Hacks” or “RTP Leaks” guaranteeing wins on specific slot titles.
- Players are instructed to register on Garuda255xhoki.site and deposit a minimum threshold to unlock the algorithm.
- Early spins may show superficial returns, but as the user increases their bet sizing to capitalize on the “pattern,” the software executes systemic losing spins.
- The operator disclaims responsibility, attributing losses to “expired patterns” and prompting the user to deposit again for “updated VIP coordinates.”
2. The Advance-Fee “Account Synchronization” Hold
When a player amasses a substantial balance and attempts an outbound withdrawal, the platform enforces advance-fee roadblocks:
- The “Data Desynchronization” Claim: Customer support informs the player that their turnover was flagged by automated bots for “irregular betting rhythms” or “IP address conflicts.”
- The Unfreeze Surcharge: The operator demands the user deposit an additional 25% to 50% of the total withdrawal amount as a “security collateral” or “tax clearance fee” to prove account authenticity.
- The Reality: Legitimate operators never demand external funds to process withdrawals—operational fees or withholding taxes are always deducted directly from account balances. Depositing additional “clearance funds” merely amplifies the financial loss before the operator disables the user’s account entirely.
3. Secondary Identity Harvesting
Unlicensed platforms are frequently connected to wider cybercrime networks. When registering on Garuda255xhoki.site, users enter their legal name, personal mobile number, and banking details.
- These details are compiled into actionable lead registries.
- Churned contact databases are monetized across illicit telemarketing networks, exposing victims to illegal micro-lending apps (pinjol ilegal), fraudulent investment schemes, and credential-stuffing campaigns across their personal digital accounts.
Every safe click counts. If this post helped, a coffee gesture fuels more scam‑busting investigations.

Infrastructure Analysis & Red Flags
Technical evaluation of the digital footprint behind Garuda255xhoki.site highlights multiple operational anomalies:
- Short-Cycle Registry Horizon: The domain was secured on a minimal one-year lease on a low-cost generic TLD (
.site). Throwaway registrations allow operators to discard the domain once security software, telecommunication watchdogs, and search engine algorithms flag it. - Obfuscated Infrastructure: Origin hosting IPs and geographic servers are shielded behind reverse-proxy routing networks (such as Cloudflare). This conceals physical server locations and complicates law enforcement inquiries.
- Non-Binding Terms of Service: The website lacks authentic legal terms, omitting corporate headquarters addresses, business registration numbers, dispute mechanisms, and designated data protection officers.
Incident Containment: What to Do If You Interacted with Garuda255xhoki.site
If you have deposited capital, entered banking credentials, or created an account on Garuda255xhoki.site, immediate defensive measures are required:
1. Cease All Outbound Transfers
Do not send additional capital under any pretext. Demands for “system re-synchronization fees,” “KYC verification deposits,” or “tax releases” are advance-fee fraud tactics. Any additional funds sent to this site will be permanently lost.
2. Protect Compromised Financial Accounts
- If you transacted via local banking transfers, call your bank’s fraud department immediately. Report that you transferred funds to an unauthorized account affiliated with an unlicensed gaming portal, state the exact beneficiary account number, and request that it be flagged as a suspected money mule.
- Request your bank to issue a fresh virtual account token or adjust online banking login credentials to stop unauthorized automated clearinghouse debits.
- If payment card details were submitted, cancel the card immediately to block unauthorized tokenized charges.
- If your login credentials on Garuda255xhoki.site match those of your primary email, banking portal, or digital wallets, change those passwords immediately using a separate, secure device.
- Enable Time-Based One-Time Password (TOTP) two-factor authentication via apps such as Google Authenticator or Microsoft Authenticator across all primary accounts. Avoid SMS-based two-factor authentication, as phone numbers entered on rogue portals are prime targets for SIM-swap attacks.
4. Guard Against Secondary “Asset Recovery” Scams
Victims of rogue platforms are often approached on messaging boards or social platforms by parties claiming to be “ethical hackers,” “blockchain tracers,” or “recovery specialists.”
- These individuals claim they can breach offshore servers or reverse banking transactions for an upfront fee.
- These are secondary scams targeting users who have already experienced financial loss. Independent third parties cannot legally or technically force refunds from illicit offshore operators. Legitimate recovery can only occur through official banking disputes, regulatory complaints, and formal law enforcement filings.
Frequently Asked Questions (FAQ)
Is Garuda255xhoki.site a licensed or legitimate online betting platform?
No. Garuda255xhoki.site holds no valid operating licenses, statutory permits, or regulatory oversight from recognized international gaming commissions (such as the Malta Gaming Authority, UK Gambling Commission, Curacao Gaming Control Board, or PAGCOR). It operates as an unauthorized offshore shadow domain.
What does the “xhoki” naming convention indicate?
Rogue gambling networks use high-intent keywords like “hoki” (luck) paired with sequential numbers (such as 255) and prefix/suffix characters to attract regional search queries and quickly rotate domain variations when older links are blocked by ISP firewalls.
Can I withdraw my deposited capital or winnings from Garuda255xhoki.site?
Withdrawing funds from unverified shadow mirrors is exceptionally unlikely once an administrative flag or payout delay is triggered. The platform routinely blocks cashout requests, creates impossible wagering terms, or demands additional external fees to stall payouts.
Why is customer service asking for a deposit to release my payout?
Demanding external cash to unlock a withdrawal is an advance-fee scam tactic. Legitimate, regulated financial and gaming operations deduct any applicable transaction fees directly from internal account balances—they never require players to send outside cash to authorize a withdrawal.
Are the slot machines and games on Garuda255xhoki.site fair?
No. Because the software runs without independent laboratory auditing (from agencies such as BMM Testlabs, GLI, or eCOGRA), site administrators can manipulate win rates, suppress RTP percentages, and alter game outcomes at their discretion.
Final Assessment
Garuda255xhoki.site represents a critical financial and cybersecurity threat. The platform combines disposable domain structures, absent regulatory compliance, pirated software scripts, and predatory withdrawal traps. Do not deposit funds, register personal credentials, or share identity data with this site. Always rely on licensed, transparent platforms bound by established legal frameworks, provably fair gaming algorithms, and independent consumer arbitration bodies.
Related Forensic Teardown
How Domain Churn Scams Keep Illegal Betting Rings Alive →Help Us Spread Awareness
Please share this article to spread awareness. Follow us on social media for more scam alerts.