Zoro.ink Review: Legit Gaming Hub, UPI Trap, or Syndicate Mirror?
Executive Summary & Verdict Callout
Zoro.ink is a deceptive, high-risk fraudulent surrogate portal and unlicensed offshore gambling gateway fronting for the illicit “DEWA90” syndicate network. Operating behind a pop-culture brand alias designed to exploit anime search trends and evade automated domain blocks, the interface functions as a top-of-funnel customer acquisition trap for underground laundering networks.
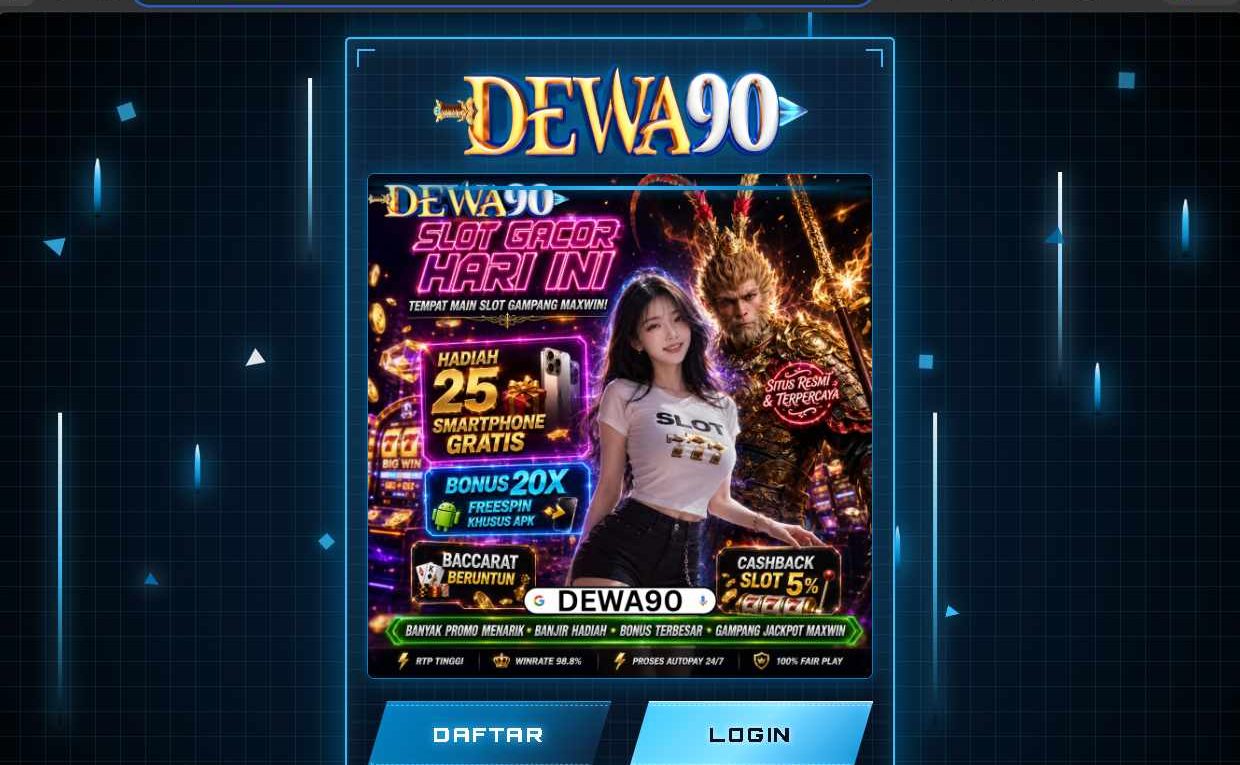
The site lures users with fabricated reward incentives—including claims of “25 Smartphone Gratis” giveaways, a hardcoded “98.8% Win Rate”, and an exclusive “Bonus 20X Freespin Khusus APK” incentive.
Sideloading this promoted Android binary exposes users to weaponized background interception trojans, while deposits submitted via dynamic virtual payment addresses (VPAs) link directly into money-mule networks, exposing players to severe legal ramifications including a bank account cyber cell debit freeze under Section 106 BNSS / Section 102 CrPC.
Technical Audit & Forensic Parameters
| Forensic Parameter | Technical Finding & Visual Artifacts |
| Active Domain URL | [https://zoro.ink](https://zoro.ink) (Lower Header Node: “ZORO: LINK SITUS SLOT PENARIKAN BESAR…”) |
| Observed Syndicated Brands | DEWA90 (“Situs Resmi & Terpercaya” / “Slot Gacor Hari Ini”) |
| On-Screen Linguistic Artifacts | “HADIAH 25 SMARTPHONE GRATIS”, “BONUS 20X FREESPIN KHUSUS APK”, “TEMPAT MAIN SLOT GAMPANG MAXWIN!”, “BACCARAT BERUNTUN”, “CASHBACK SLOT 5%”, “PROSES AUTOPAY 24/7”, “100% FAIR PLAY” |
| Promoted Multipliers & Odds | WINRATE 98.8%, RTP TINGGI badge, Bonus 20X Freespin multiplier |
| Direct Distribution Endpoints | Standalone promotional vector: BONUS 20X FREESPIN KHUSUS APK (featuring the Android green robot emblem) |
| Primary Interaction Selectors | High-contrast registration button: DAFTAR and account access: LOGIN |
| Financial Settlement Infrastructure | Dynamic peer-to-peer mule UPI IDs, illicit third-party shadow wallets, and automated P2P crypto rails |
| Regulatory & Licensing Status | Completely Unlicensed. Zero operational licensing, audit certifications, or consumer compliance filings with recognized regulatory bodies. |
Linguistic & Visual Dissection (Evidence-Based from Screenshot)
1. Trademark Parasitism & The Disposable .ink Namespace
The domain zoro.ink leverages an evasion strategy. The string “Zoro” borrows directly from globally recognized anime intellectual property (Roronoa Zoro from One Piece), functioning as a deliberate pop-culture keyword hijack. By using an established cultural name, the operators generate artificial trust and hijack organic search queries from younger, media-focused demographics.
Pairing this keyword with the .ink top-level domain provides operational agility. Domain registrars offering .ink zones allow anonymous, bulk registration with minimal KYC checks. Because .ink domains are cheap and disposable, syndicates easily discard them the moment telecommunications firewalls, antivirus databases, or cybercrime portals blacklist the URL, pointing DNS records to identical mirror nodes in minutes.
2. UI Camouflage: Sensory Traps & Hardware Giveaways
The visual composition relies on layered psychological manipulation:
- The Hardware Incentive Trap: Dominating the upper-left promo badge is the claim: “HADIAH 25 SMARTPHONE GRATIS” displaying a high-end smartphone render beside stacked gold coins. Promising physical luxury assets for creating a free account is an advance-fee scam mechanism designed to hook low-income users.
- The Sun Wukong / Mythological Authority Framing: Flanking the central female model (wearing a branded “SLOT” crop-top) is an armored rendering of Sun Wukong, the Monkey King. Grounded in popular East Asian myth and popular video game tropes, the figure projects invincibility and power, reinforcing the nearby label: “SITUS RESMI & TERPERCAYA” (Official & Trusted Site).
- The “Khusus APK” Trojan Incentive: The platform features an explicit APK installation trap: “BONUS 20X FREESPIN KHUSUS APK” accompanied by the official Android mascot. Offering game-specific perks exclusively on the sideloaded application pushes mobile visitors off secure web browsers and onto an unvetted APK installation funnel.
- Trust Badging & Algorithmic Manipulation: Across the bottom ribbon, the UI stacks badges claiming “RTP TINGGI”, “WINRATE 98.8%”, “PROSES AUTOPAY 24/7”, and “100% FAIR PLAY”. Below this sits a Google search bar reading “G DEWA90”, engineered to drive Google search velocity and boost the syndicate’s search footprint.
3. Cross-Border Traffic Funnels
While the visual identity and phrasing are framed entirely in Indonesian dialect (Tempat Main Slot Gampang Maxwin!), these mirrors are deployed to capture traffic internationally. Syndicates buy ad placements on pirated anime streaming sites, illegal cricket broadcasts, and rogue Telegram prediction groups across South Asia. When Indian users click these links, dynamic IP-forwarding scripts adapt the checkout portal to local payment gateways, serving Unified Payments Interface (UPI) corridors directly to the visitor.
Suspicious Link or Courier SMS?
Verify URLs, APKs, or parcel alerts against our threat database before clicking.
5 Critical Technical Deceptions
[ User Enters Zoro.ink ]
            │
      ┌─────┴────────────────────────────────┐
      ▼                                      ▼
[ "DAFTAR" Registration ]       [ "BONUS 20X FREESPIN KHUSUS APK" ]
      │                                      │
  Rotating Mule UPI Allocation           Unsigned Android APK Sideload
      │                                      │
  Layered Money Laundering Rails         Spyware & Accessibility Exploits
      │                                  (`RECEIVE_SMS`, `BIND_ACCESSIBILITY`)
      ▼                                      ▼
Bank Account Cyber Cell Debit Freeze    Silent Background OTP Interception
(Section 106 BNSS / 102 CrPC)
1. Dynamic Mule Account Money Laundering
When a user initiates a deposit on zoro.ink, funds are not processed by a legitimate corporate merchant. Instead, the backend API dynamically allocates temporary virtual payment addresses (VPAs) or bank accounts registered to compromised “mules”—often created using leased, forged, or stolen KYC documents. Once the UPI transaction is processed, automated liquidity bots bounce the funds through multiple intermediary tiers before off-ramping the capital into crypto assets (USDT) on P2P exchanges, leaving the original depositor legally exposed to cybercrime tracing.
2. Algorithmic Rigging & Simulated RTP
The featured Winrate 98.8% and RTP Tinggi claims are fabricated. Certified, fair-play online slots run on cryptographically verified Pseudo-Random Number Generators (PRNGs) audited by accredited laboratories, maintaining an average house edge between 4% and 8%. Syndicate clones like DEWA90 use manipulated game scripts where odds are manually tweaked from backend administrative dashboards, intentionally staging an initial “winning streak” to lure users into depositing larger sums before triggering a complete loss cascade.
3. Sideloaded APK Vector & Silent OTP Interception
The BONUS 20X FREESPIN KHUSUS APK banner pushes an off-store application file directly to the user’s phone, intentionally bypassing the security verifications of the Google Play Store. Decompiled packages of this syndicate cluster frequently reveal high-risk Android permissions:
android.permission.RECEIVE_SMS&READ_SMS: Grants background access to all incoming text messages, enabling the operator to intercept banking OTPs in real-time.android.permission.BIND_ACCESSIBILITY_SERVICE: Gives the malware permission to read screen content, track keystrokes, and automatically dismiss security prompts without manual user intervention.
4. Zero Corporate Accountability & Bulletproof Hosting
The platform conceals its operators behind complete anonymity. It lists no verifiable corporate identity, no headquarters address, and no operational licensing numbers. Its hosting infrastructure is managed via bulletproof reverse proxies located in non-cooperative offshore jurisdictions, specifically configured to ignore international copyright takedown notices and law enforcement requests.
5. Advance-Fee Withdrawal Blocks
While inbound payments clear immediately, the platform enforces asymmetric friction on withdrawals. When a user requests a payout of their balance, the transaction is flagged for “system verification,” “anti-money laundering clearance,” or “autopay maintenance.” The victim is instructed to deposit an upfront “processing fee” or “withholding tax” to clear the queue. Every additional fee transferred is stolen, and the account is ultimately terminated.
Emergency Remediation & Financial Recovery
If you have transferred funds to, shared credentials with, or downloaded software from zoro.ink, take these actions immediately:
1. Golden-Hour Fraud Response
- Call 1930 Helpline Immediately: If you are in India, report the incident immediately via the National Cybercrime Reporting Helpline (1930). Dialing within the “golden hour” allows authorities to notify participating banks and freeze the recipient mule account before the funds are dispersed into crypto channels.
- Lodge an Incident at cybercrime.gov.in: File a comprehensive fraud dossier on the National Cybercrime Reporting Portal. Upload unedited screenshots of your transaction details, the recipient VPA, UTR numbers, and any chat logs from the platform.
- Initiate a Bank Chargeback: Immediately alert your bank’s fraud control unit. Report that you were redirected to a fraudulent peer-to-peer mule account via deceptive merchant misrepresentation, and file an unauthorized transaction dispute.
2. Resolving a Cyber Cell Debit Freeze (Section 106 BNSS / 102 CrPC)
If your bank account is placed under a debit freeze or police lien after paying this platform, your transfer connected directly into an active cybercrime syndicate investigation:
- Contact your bank’s nodal officer to obtain the formal Freezing Order, which includes the Crime Reference Number, the originating Police Station/State Cyber Cell, and the Investigating Officer’s (I.O.) contact email.
- Compile a complete evidentiary paper trail showing your payment flow, proof of the fraudulent gameplay, and bank statements establishing that you were an unwitting victim rather than an accomplice operating a mule account.
- Submit this dossier directly to the Investigating Officer to request a No Objection Certificate (NOC) and unfreeze the unencumbered balance in your bank account.
3. Report Phishing Vectors via Chakshu
If you received links to zoro.ink via unsolicited SMS broadcasts, WhatsApp messages, or spoofed phone numbers, report these details on the Chakshu portal within the Department of Telecommunications’ Sanchar Saathi platform (sancharsaathi.gov.in) to aid in blacklisting the perpetrators’ telecommunication assets.
Android Quarantine & Spyware Neutralization
If you interacted with the BONUS 20X FREESPIN KHUSUS APK banner and installed the sideloaded file, treat your mobile device as compromised:
- Sever Network Connections: Turn on Airplane Mode and disable Wi-Fi immediately to cut off real-time exfiltration of credentials and remote command-and-control access.
- Reboot into Safe Mode:
- Hold down your phone’s physical Power button.
- Long-press the onscreen Power Off or Restart icon until the Reboot to Safe Mode prompt appears. Confirm the selection. Safe Mode boots the Android OS with all downloaded third-party code completely deactivated.
- Revoke Device Administrator Rights:
- Open
Settings➔Security➔Device Admin Apps. - Look for unrecognized applications masquerading as “System Updates,” “Dewa Engine,” or “Flash Player” and immediately toggle off their administrative rights.
- Open
- Uninstall the Malicious Package:
- Open
Settings➔Apps➔See All Apps. - Find the downloaded APK or any newly installed, unfamiliar applications and tap Uninstall.
- Open
- Restore Messaging Defaults & Scan the Device:
- Navigate to
Settings➔Apps➔Default Appsand verify that your device’s native messaging client is assigned as the default SMS application. - Open the Google Play Store, tap your profile icon, open Play Protect, and execute a full device security scan.
- Navigate to
High-RPM Cybersecurity Resource Block
🛡️ Personal Threat Defense Suite
- Mobile Antivirus & Spyware Removal: Identify and remove hidden remote-access trojans (RATs) and malicious APK droppers using an industry-recognized mobile security scanner (e.g., Bitdefender Mobile Security or Malwarebytes).
- Identity Theft & Credit Protection: Guard your personal details and prevent unauthorized loans or account creation if your KYC data was shared on unverified portals (e.g., Aura or Experian IdentityWorks).
- Anti-Phishing & Traffic Protection VPN: Automatically block fraudulent mirrors, rogue proxies, and malicious scripts at the DNS layer using advanced web-filtering software (e.g., NordVPN Threat Protection or Surfshark CleanWeb).
Frequently Asked Questions (FAQ)
Is Zoro.ink Scam?
Yes, Zoro.ink is an active online scam. The website functions as an unlicensed surrogate proxy that uses counterfeit 98.8% win probabilities, fake hardware giveaways (“25 Smartphone Gratis”), and rotating mule payment rails to steal user deposits without honoring withdrawals.
Is Zoro.ink Legit?
No, Zoro.ink is completely illegitimate. It holds no valid gaming licenses, has no verified corporate registration, and mimics legitimate gaming brands to route users into an unregulated syndicate network operating outside consumer protection laws.
What is the risk of downloading the “Bonus 20X Freespin Khusus APK”?
The promoted APK bypasses Google Play Protect checks. Sideloading this unverified file exposes your smartphone to banking spyware and Trojans capable of abusing SMS and Accessibility permissions to intercept banking OTPs and steal private account information.
Why is my bank account frozen after depositing into Zoro.ink?
Your account was likely placed under a debit freeze under Section 106 BNSS / Section 102 CrPC because your payment was routed into an active money-laundering mule account. When cyber police departments investigate syndicate accounts, every linked account in the transaction trail is temporarily frozen.
Can I withdraw my deposited funds or winnings from Zoro.ink?
No. Balances displayed on the screen are simulated by the site’s operators. When you attempt to withdraw, the platform blocks the transaction and often demands additional “verification fees” or “clearance taxes,” which simply leads to further financial loss.
Every safe click counts. If this post helped, a coffee gesture fuels more scam‑busting investigations.

Related Forensic Teardown • Master Guide
How Domain Churn Scams Keep Illegal Betting Rings Alive →Help Us Spread Awareness
Please share this article to spread awareness. Follow us on social media for more scam alerts.