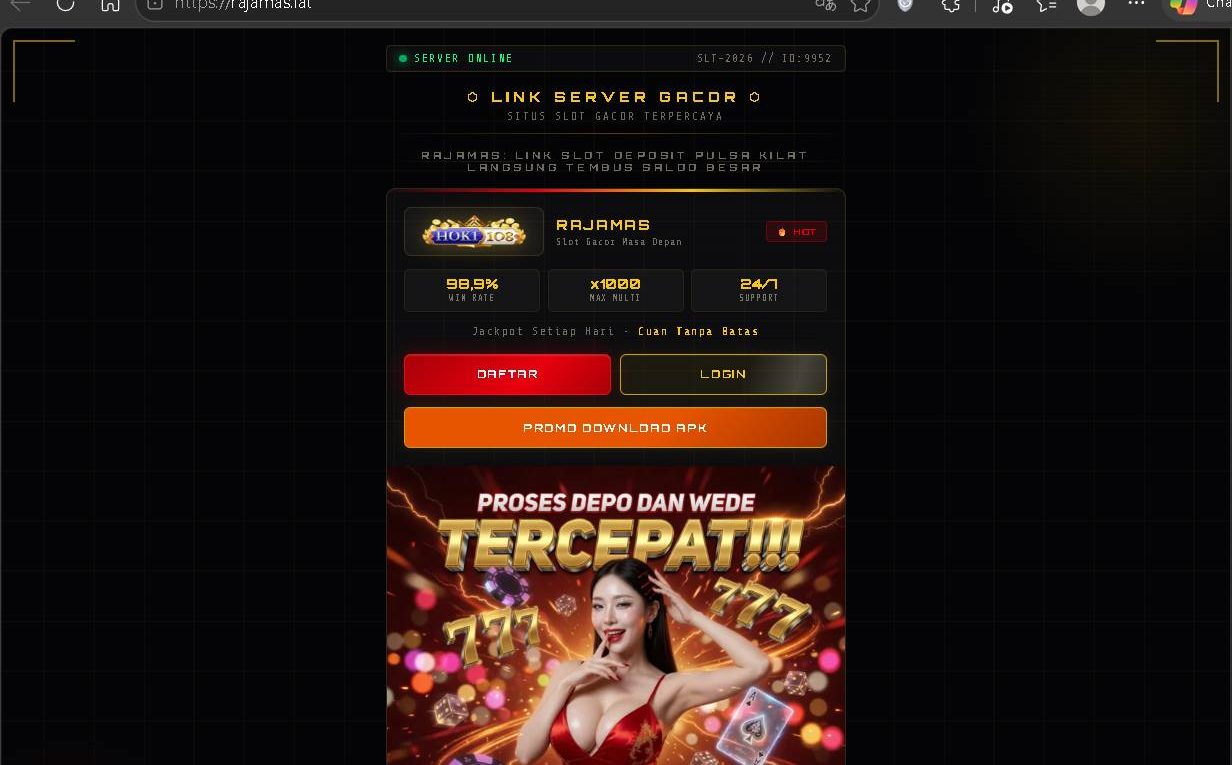
Rajamas.lat Review: Investigating The Bait-and-Switch (RTP Manipulation) in Disposable Mirror Networks
When navigating digital gaming promotions, landing pages like Rajamas.lat often present a tempting façade of guaranteed wins, but an objective technical review reveals how The Bait-and-Switch (RTP Manipulation) operates as an engineered financial drain. By stripping away mathematically audited randomness in favor of operator-controlled scripts, illicit betting funnels systematically extract user deposits while eliminating fair probability.
For users who stumble across this address via viral messaging channels, automated social promotions, or search engine redirects, recognizing the underlying risks is vital. Platforms operating on transient domains use identical, cloned infrastructure to impersonate legitimate iGaming providers, exposing visitors to frozen withdrawals, predatory deposit funnels, and persistent mobile malware threats.
What Is Rajamas.lat and How Does It Operate?
Rajamas.lat is not a legitimate, self-contained gaming portal. Instead, it functions as a lightweight bridge domain and alternate redirect link (link alternatif) designed to route retail internet traffic into unauthorized offshore betting networks—specifically operations associated with the RAJAMAS brand.
Because national telecommunication bodies and cyber task forces actively block black-market gambling domains, offshore syndicates deploy disposable bridge pages across low-cost top-level domains (.lat, .fit, .site, .wiki).
Suspicious Link or Courier SMS?
Verify URLs or APKs before clicking.
[ Cold Traffic: Social Feeds / Telegram Spam / Redirect Links ]
                                │
                                ▼
                     ┌────────────────────┐
                     │    Rajamas.lat     │  ◄── Lightweight Gateway
                     └────────────────────┘
                                │
         (Bypasses Regional Telecom Blacklists / Firewalls)
                                │
                                ▼
          ┌───────────────────────────────────────────┐
          │     Unregulated Offshore Betting Host     │
          │   - Front-end Brand: RAJAMAS              │
          │   - Automated One-Way Deposit Channels    │
          │   - Scripted Clones with Adjustable Odds  │
          │   - Direct APK Sideloading Vector         │
          └───────────────────────────────────────────┘
The portal uses a stripped-down, terminal-style layout designed for near-instant rendering on mobile connections. The page features a pseudo-technical header (“SLT-2026 // ID:9952”), immediate authentication buttons (DAFTAR and LOGIN), and an external file trigger labeled PROMO DOWNLOAD APK. Every interaction channels the visitor straight into an unvetted offshore administrative database.
Player Safety Blueprint: Prevention & Solutions
Protect assets before interacting with unverified mirrors, or follow mitigation steps if data was shared.
Never pay secondary “clearance taxes” or “unlock fees” to release trapped funds.
Uninstall suspicious packages, reboot into Safe Mode, and run an updated antivirus scan.
Reset passwords on linked emails/wallets immediately and enable authenticator-app 2FA.
Contact your bank’s fraud desk to dispute transactions under merchant fraud.
Block unsolicited contacts and disregard third-party “fund recovery” hackers requesting fees.
Core Claims and Advertised Products
The promotional interface of Rajamas.lat relies heavily on psychological triggers and misleading industry jargon:
- Unrealistic 98.9% Win Rate: The hero console prominently advertises a “98,9% Win Rate” alongside an “x1000 Max Multi” and claims of “Jackpot Setiap Hari · Cuan Tanpa Batas” (daily jackpots, limitless profits).
- Instant Mobile-Balance Funding: The site markets “Link Slot Deposit Pulsa Kilat Langsung Tembus Saldo Besar,” encouraging users to bypass traditional bank scrutiny by funding accounts through mobile phone credit transfers.
- Direct App Sideloading: A highlighted orange button prompts visitors to install external software via
PROMO DOWNLOAD APK, circumventing mobile operating system safety controls. - Fabricated Trust Badges: The page displays claims of “Link Server Gacor Terpercaya” and “24/7 Support,” despite offering no verifiable corporate registration, business address, or legal jurisdiction details.
Explaining The Bait-and-Switch (RTP Manipulation)
To understand why players consistently face financial losses through portals like Rajamas.lat, one must understand how The Bait-and-Switch (RTP Manipulation) works beneath the interface.
Audited Game Studios vs. Pirated Clone Engines
In legally regulated jurisdictions, online gaming platforms host certified titles from licensed studios like NetEnt, Microgaming, or Pragmatic Play. The Return-to-Player (RTP) rate—typically fixed between 94% and 97%—is locked on remote studio servers audited by accredited testing facilities like eCOGRA, iTech Labs, or BMM Testlabs.
Unregulated networks, on the other hand, run pirated, reverse-engineered software copies hosted on private offshore servers. This lets operators manually modify payout outcomes:
Audited iGaming Standard:
[Player Spin] ───► [Audited Studio Server] ───► [Locked RTP (94-97%)] ──► Provably Fair Outcome

Predatory Offshore Setup:
[Player Spin] ───► [Cloned Host Script]    ───► [Operator Control Panel] ──► Algorithmic Depletion
                                                               ▲
                                                    (Dialed down after deposit)
The Phased Extraction Strategy
- The Initial Hook: On early spins with micro-stakes, the server is calibrated to return small, frequent wins. This creates a quick dopamine loop and makes the player believe the advertised “98.9% win rate” is legitimate.
- The Account Reload: Encouraged by early success, the player deposits a larger sum using bank transfers, e-wallets, or cellular credit.
- The Backend Adjustment: Operators quietly dial down the Return-to-Player rate to near zero, or configure bonus rounds to never trigger.
- The Complete Depletion: The player’s balance is drained through long losing streaks, which the player mistakenly attributes to ordinary variance rather than deliberate algorithmic tampering.
Five Critical Red Flags on Rajamas.lat
A. Statistically Impossible Payout Claims (98.9% Win Rate)
No real commercial gaming platform offers a genuine 98.9% win rate. Commercial casino titles are mathematically designed with an audited house edge. Promising nearly certain returns alongside guaranteed daily jackpots is a deceptive marketing hook designed to exploit novice players.
B. High-Risk Sideloading via Untrusted APK Files
The inclusion of a direct PROMO DOWNLOAD APK button represents a serious cybersecurity threat. Downloading and installing an unverified Android application from an arbitrary browser link bypasses Google Play Protect screening. Such packages often contain spyware, remote access tools, or SMS-intercepting malware designed to compromise mobile banking credentials and steal one-time passwords (OTP).
C. Total Lack of Regulatory Licensing
Authorized gaming operators prominently display verifiable licensing credentials issued by established regulators like the Malta Gaming Authority, the UK Gambling Commission, or the Isle of Man Gambling Supervision Commission. Rajamas.lat features zero verifiable license numbers, zero corporate registry data, and no physical headquarters. Players have no legal recourse or consumer dispute channels when funds disappear.
D. Use of Disposable .lat Infrastructure
Operating a casino redirect on an inexpensive .lat domain with hidden WHOIS records is a standard hallmark of short-lived mirror networks. Operators acquire these domains in bulk so they can abandon them the moment internet service providers block the link, pointing incoming traffic to a fresh mirror while maintaining their offshore infrastructure.
E. Asymmetric Payment Controls and Data Harvesting
Depositing money on the site is instant and frictionless, but withdrawing funds is routinely blocked. When players attempt to withdraw significant winnings, operators typically demand additional advance “tax” payments, claim sudden technical errors, or ban the account entirely.
Furthermore, personal details submitted during registration (phone numbers, WhatsApp handles, bank accounts) are routinely compiled and traded across gray-market telemarketing and illegal loan networks.
Direct Protection Guide: Securing Your Information and Finances
If you have already interacted with Rajamas.lat, submitted sensitive credentials, or downloaded files from the domain, take these protective measures immediately:
- Delete the Downloaded APK and Scan Your Device: If you installed the external
.apkfile, delete it from your smartphone immediately. Run a comprehensive scan with a reputable mobile antivirus program, and check your device administrator settings to ensure no unauthorized application has background access or SMS-reading permissions. - Stop Sending Additional Funds: If customer support claims you must pay a “clearance fee,” “tax surcharge,” or meet an unexpected turnover requirement to unlock your balance, do not send any money. These are advance-fee extortion tactics designed to extract more capital before closing your account.
- Notify Your Financial Institution: Contact your bank or payment provider to report that your details were submitted to an unverified payment merchant. Request a block on suspicious online transactions and consider reissuing your payment cards.
- Update Passwords and Enable Multi-Factor Authentication: If your casino login shares credentials with your email, banking apps, or social media accounts, change those passwords immediately. Switch two-factor authentication from SMS verification to an app-based authenticator (such as Google Authenticator).
- Ignore Unsolicited “Fund Recovery” Offers: Do not hire third-party individuals on social platforms claiming they can hack offshore servers to recover lost balances. These operators run secondary recovery scams that target individuals who have already lost money.
Frequently Asked Questions
1. Is Rajamas.lat Scam?
Yes. Rajamas.lat displays all the hallmarks of an unregulated, high-risk gambling gateway. It operates without regulatory licensing, advertises unrealistic win rates, distributes unverified mobile applications, and channels player funds into offshore databases known for blocking payouts.
2. Is Rajamas.lat Legit?
No, Rajamas.lat is not legitimate. Legitimate online entertainment and iGaming companies operate with verifiable corporate registrations, hold active licenses from recognized regulatory authorities, and publish independently audited software compliance records—none of which are present on this platform.
3. What makes The Bait-and-Switch (RTP Manipulation) dangerous?
This tactic creates a false impression of fair odds by giving users small, early wins on low stakes. Once larger deposits are made, backend operators quietly lower the game’s payout percentage, ensuring the user’s balance empties out quickly.
4. What are the security risks of downloading the APK from Rajamas.lat?
Installing an unverified APK from an unauthorized browser link bypasses device security controls. These packages can conceal harmful software designed to monitor keystrokes, intercept SMS two-factor authentication codes, and compromise your mobile banking applications.
5. Why do these gambling gateways rely on cheap extensions like .lat?
Unregulated gaming syndicates purchase cheap, non-standard domain extensions in bulk to bypass domestic ISP bans and telecom filters. When one web address is blacklisted, they can switch to another disposable mirror without disrupting their backend operations.
6. Can lost balances on Rajamas.lat be recovered?
Recovering funds directly from unregulated offshore entities is very difficult because they operate outside local jurisdictions. Your most viable option is to contact your bank or credit card fraud department to file an unauthorized transaction dispute or investigate chargeback options.
7. Are game outcomes on Rajamas.lat independently audited?
No. There is no evidence of software certification from accredited testing agencies such as eCOGRA or iTech Labs. Games on unverified mirror portals often run on cloned scripts that allow administrators to manipulate payout odds and volatility.
8. How can a user verify if an online casino platform is genuine?
Check the operator’s license number in the public registry of an established regulator, such as the Malta Gaming Authority or the Isle of Man Gambling Supervision Commission. Legitimate sites provide clear corporate ownership information, transparent terms of service, and direct streams from licensed game developers.
Every safe click counts. If this post helped, a coffee gesture fuels more scam‑busting investigations.

Help Us Spread Awareness
Please share this article to spread awareness. Follow us on social media for more scam alerts.