Pisangin.fit Exposed: How This Disguised Casino Uses Brand Deception and Wagering Funnels
When you sit at any gaming table, your first job is spotting the mark; if you can’t spot them within ten minutes, you are the mark. Stumbling across Pisangin.fit pulls casual web users straight into a textbook Brand Deception / Impersonation Risks Scam, dangling an innocent URL while operating a predatory, unauthorized online casino.
Instead of health metrics or fresh agricultural goods, this domain runs a Deceptive Bait-and-Switch Wagering Funnel Scam aimed at intercepting unsuspecting traffic and siphoning deposits before visitor skepticism kicks in.
In modern traffic brokering, rogue affiliates treat domain registrations like throwaway chips. By picking web addresses that look like benign lifestyle utilities, these networks sidestep automated safety scanners, lure in curious searchers, and funnels them straight toward unregulated offshore slot machines.
This forensic report exposes the exact backend mechanics of Pisangin.fit, examines how its affiliate funnel siphons user capital into the Homebet88 syndicate, and outlines concrete countermeasures to secure your accounts if you interacted with this setup.
Anatomy of a Bait-and-Switch Wagering Network
In digital asset defense, a deceptive wagering funnel operates like a back-alley gambling den hidden behind an ordinary fruit market awning. Unregulated offshore operators specifically purchase top-level domains like .fit because these extensions have clean reputation scores with major domain registries. Web security algorithms generally classify .fit websites under lifestyle, athletic coaching, or dietary tracking categories.
That semantic cover is the trap. The split-second contradiction between what you expect to see (a wellness portal or nutrition blog) and what actually renders (flashing slot machines and high-stakes banners) triggers cognitive disorientation.
Before your critical guard goes up, aggressive call-to-action buttons push you toward quick deposits and application downloads. The syndicates behind these pages deliberately mix third-party brand names into disposable shell domains.
If one entry domain gets blocked by telecom regulators or flagged by antivirus programs, the operator simply points their DNS records to a fresh, cheap domain name overnight while preserving their backend cash collection pipeline.
Player Safety Blueprint: Prevention Rules & Actionable Solutions
Protect your digital assets before interacting with unverified gambling mirrors, or follow the mitigation sequence if you have already shared data.
Never pay secondary “clearance taxes,” “unlock fees,” or “verification deposits.” Unregulated syndicates use these requests to extract extra funds before blocking your account.
Uninstall any browser-downloaded package immediately. Reboot into Safe Mode, run an updated antivirus scan, and revoke any suspicious SMS or Accessibility permissions.
Reset passwords on any email accounts, crypto wallets, or payment platforms that shared login credentials with the mirror site. Turn on app-based 2FA (e.g., Google Authenticator).
If you deposited using debit or credit rails, call your issuing bank’s dispute desk immediately to file a chargeback under merchant fraud or failure of service delivery.
Report and block WhatsApp or Telegram spam numbers. Ignore third-party “fund recovery agents” claiming they can hack back your balance for an upfront retainer.
Technical Teardown: How Pisangin.fit Funnels Player Deposits
Evaluating the front-end layout of Pisangin.fit reveals a synchronized conversion pipeline built to strip away friction from money transfers:
Promotional Claims vs. Statistical Reality
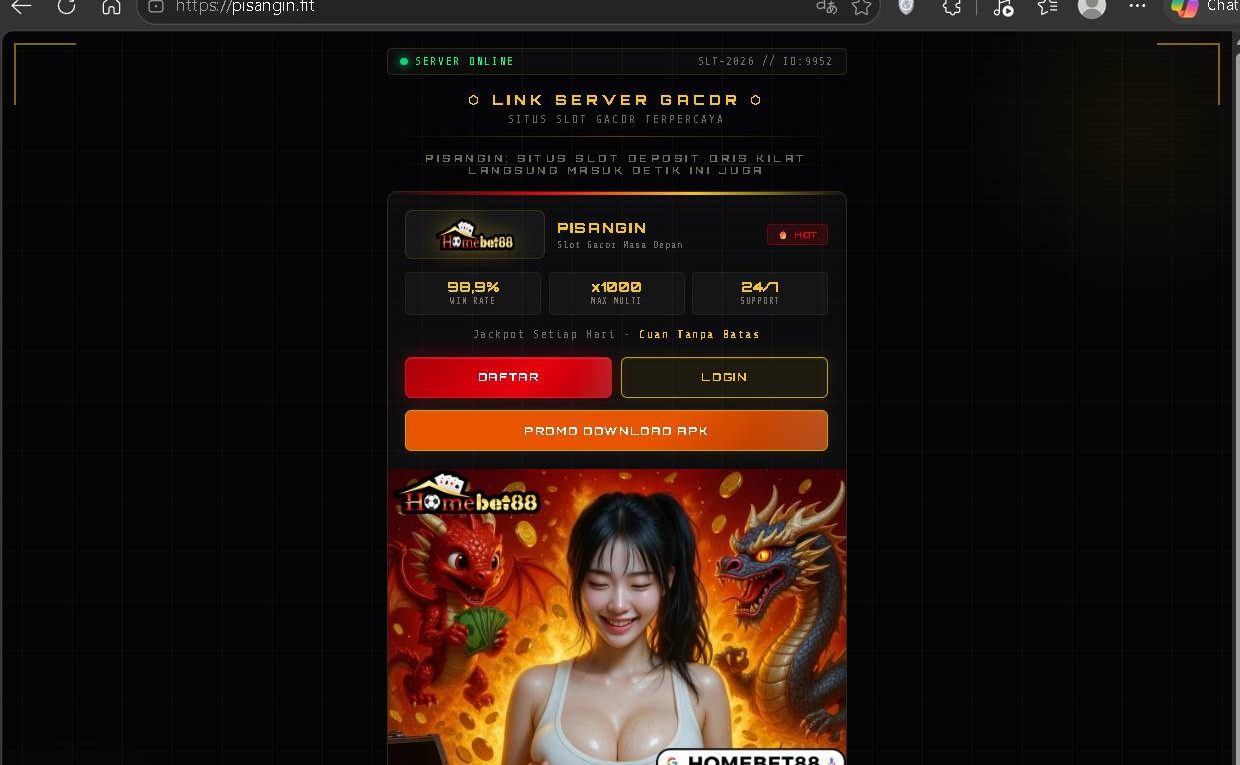
The landing page renders in high-contrast black and gold, decorated with an animated dragon graphic and an Asian-themed mascot designed to mimic licensed mobile social casino games. The top status bar flashes an active session indicator (SLT-2026 // ID: 9952), creating false urgency by implying an exclusive, real-time connection to a private server.
The site’s primary promotional text—“Situs Slot Deposit QRIS Kilat Langsung Masuk Detik Ini Juga”—promises instantaneous fund clearance. Alongside this, the platform advertises metrics that defy the mathematical reality of regulated electronic gambling:
- A claimed 98.9% Win Rate, an impossible figure for games that depend on mathematical house edges.
- A promised x1000 Maximum Multiplier with uncapped profit slogans (“Cuan Tanpa Batas”).
- Purported 24/7 technical and withdrawal support.
Suspicious Link or Courier SMS?
Verify URLs, APKs, or parcel alerts against our threat database before clicking.
Backend Architecture: The Homebet88 Funnel
The domain does not run proprietary, verified game engines. Instead, it operates as a throwaway affiliate feeder:
- Cloaked Traffic Routing: The platform buys cheap pop-under traffic and search queries that bypass corporate content filters thanks to the
.fitextension. - Third-Party Brand Embedding: The layout features persistent Google-style search badges explicitly reading HOMEBET88. This confirms that Pisangin.fit is an unaccredited front door routing player signups into an external gambling syndicate.
- Frictionless QRIS Clearing: Traditional online merchants require credit card verification, PCI-DSS compliance, and user identity confirmation. Pisangin.fit bypasses this by utilizing QR-based peer-to-peer transfers. Once scanned via mobile banking apps, your payment clears irreversibly into an untraceable intermediary account.
- App Sideloading Pipeline: Rather than hosting a responsive web portal, the site emphasizes an orange button marked “Promo Download APK”. This prompts Android users to manually install unverified application files, creating severe mobile security risks.
5 Critical Red Flags on Pisangin.fit
Experienced risk managers inspect the plumbing of a site before placing trust in it. Reviewing Pisangin.fit against international web security and consumer protection standards reveals five critical danger signs:
- Complete Semantic Incoherence: The word “pisang” (banana) paired with a fitness extension (
.fit) forms a deliberate mask that has no relation to the digital slot platform running on the page. - Mathematically Fraudulent Payoff Ratios: Promoting a 98.9% sustained player return violates basic probability theory. Certified casinos subject their Random Number Generator (RNG) code to strict testing bodies like eCOGRA or BMM Testlabs; unverified portals fabricate payout rates purely to entice speculative deposits.
- Dangerous APK Sideloading: Urging users to download an off-market
.apkpackage bypasses Google Play Protect and device sandboxing. Rogue gambling APKs frequently request broad device permissions, leaving smartphones vulnerable to SMS interceptors, notification eavesdroppers, and banking trojans. - Absence of Corporate Identity and Licensing: The site provides no legal corporate entity name, physical jurisdiction, dispute policy, or registration credentials from recognized gaming authorities (such as Curacao eGaming, the Malta Gaming Authority, or the UK Gambling Commission).
- Unprotected Payment Funnels: Pushing automated instant-clearance transfers deprives users of banking chargeback mechanisms, card association arbitration, and consumer protection coverage.
Immediate Steps to Secure Your Accounts and Devices
If you landed on this portal, entered personal data, or initiated a financial transaction, take these defensive measures immediately:
- Delete Any Downloaded
.apkFiles: If you downloaded the mobile installation package, do not open it. Remove the.apkfile from your device storage, wipe your browser cache, and run a scan using mobile security tools like Malwarebytes or Bitdefender. - Monitor Linked Payment Channels: If you scanned a QRIS code or authorized a payment via a digital wallet, review your bank statement immediately. Flag unauthorized merchant transactions with your bank’s fraud department and request a block on outgoing peer-to-peer authorizations if suspicious debits appear.
- Change Shared Credentials: If you used the site’s “Daftar” (Registration) button and entered a username and password that you use elsewhere, update your credentials on your email and banking accounts immediately.
- Submit Formal Cyber Fraud Reports: Log the domain details and transaction IDs with national digital protection portals, such as the National Cyber Crime Reporting Portal (in India), Action Fraud (UK), or the IC3 (US), to help block the underlying payment rails.
Frequently Asked Questions (FAQs)
1. Is Pisangin.fit a scam?
Yes. Pisangin.fit demonstrates clear characteristics of a predatory online gambling trap, including deceptive domain masking, fabricated win-rate figures, unmonitored payment funnels, and unverified software downloads. Depositing funds on this portal exposes users to total capital loss.
2. Is Pisangin.fit legit?
No. Pisangin.fit is not an authorized health portal, licensed bookmaker, or legitimate gaming operator. It operates without regulatory oversight, audits, or verifiable corporate registration.
3. What is the connection between Pisangin.fit and Homebet88?
Pisangin.fit functions as an affiliate bridge for Homebet88. Syndicates deploy disposable landing pages to capture search queries and funnel new players into external gaming networks while insulating the primary brand from search engine penalties.
4. What are the specific security risks of downloading the Pisangin.fit APK?
Installing an unverified Android application package (.apk) from an untrusted domain bypasses official app store safety checks. Malicious APKs distributed by offshore gambling funnels can contain trojans capable of harvesting device data, reading incoming two-factor authentication (2FA) codes, and compromising mobile banking apps.
5. Can I reverse a QRIS payment sent through Pisangin.fit?
Reversing instant QR code transactions is exceptionally difficult because funds settle immediately into recipient accounts. Contact your mobile wallet provider or bank fraud desk immediately to report the transaction as deceptive merchant fraud, providing screenshots of the landing page as evidence.
6. Why do offshore slot platforms use .fit web extensions?
Rogue gambling networks purchase generic top-level domains like .fit because search engines categorize them as wellness or fitness pages. This semantic camouflage helps the sites slip past ad blockers, workplace network filters, and automated keyword blacklists.
7. What does “Server Gacor” mean on Pisangin.fit?
In Southeast Asian gambling parlance, “gacor” translates to a slot machine that pays out frequently. On sites like Pisangin.fit, it is used purely as marketing clickbait to convince inexperienced players that the platform’s algorithms are set to pay out higher winnings than regulated casinos.
8. How can I confirm whether an online casino is officially licensed?
Legitimate online casinos link their license credentials directly to public validation registers run by recognized regulators (such as Curacao, Malta, or Gibraltar). They publish their legal operating company, maintain audited RNG certificates from firms like iTech Labs, and use verified, standard merchant payment processors.
Every safe click counts. If this post helped, a coffee gesture fuels more scam‑busting investigations.

Help Us Spread Awareness
Please share this article to spread awareness. Follow us on social media for more scam alerts.