Pgslow.ink Review: Legit Gaming Hub, UPI Trap, or Syndicate Mirror?
Executive Summary & Verdict Callout
Pgslow.ink is an active, high-risk fraudulent surrogate funnel and unverified offshore gambling proxy engineered to channel retail deposits into transnational money laundering corridors while distributing weaponized mobile applications. Masquerading behind the unauthorized branding of “HOKI108” and a bogus server connection terminal, the landing page acts as a feeder link designed to funnel web traffic directly into unregulated syndicate clusters.
The portal lures users with mathematically fraudulent return metrics—including a hardcoded 98.9% win rate and a 1000x multiplier promise—while offering an unverified side-channel PROMO DOWNLOAD APK installer. When victims initiate deposits through these interfaces, their funds do not land in certified merchant reserves; instead, they are absorbed into decentralized networks of rotating mule accounts, exposing unsuspecting depositors to direct bank account cyber cell debit freezes under Section 106 of the Bharatiya Nagarik Suraksha Sanhita (BNSS) / Section 102 CrPC.
Technical Audit & Forensic Parameters
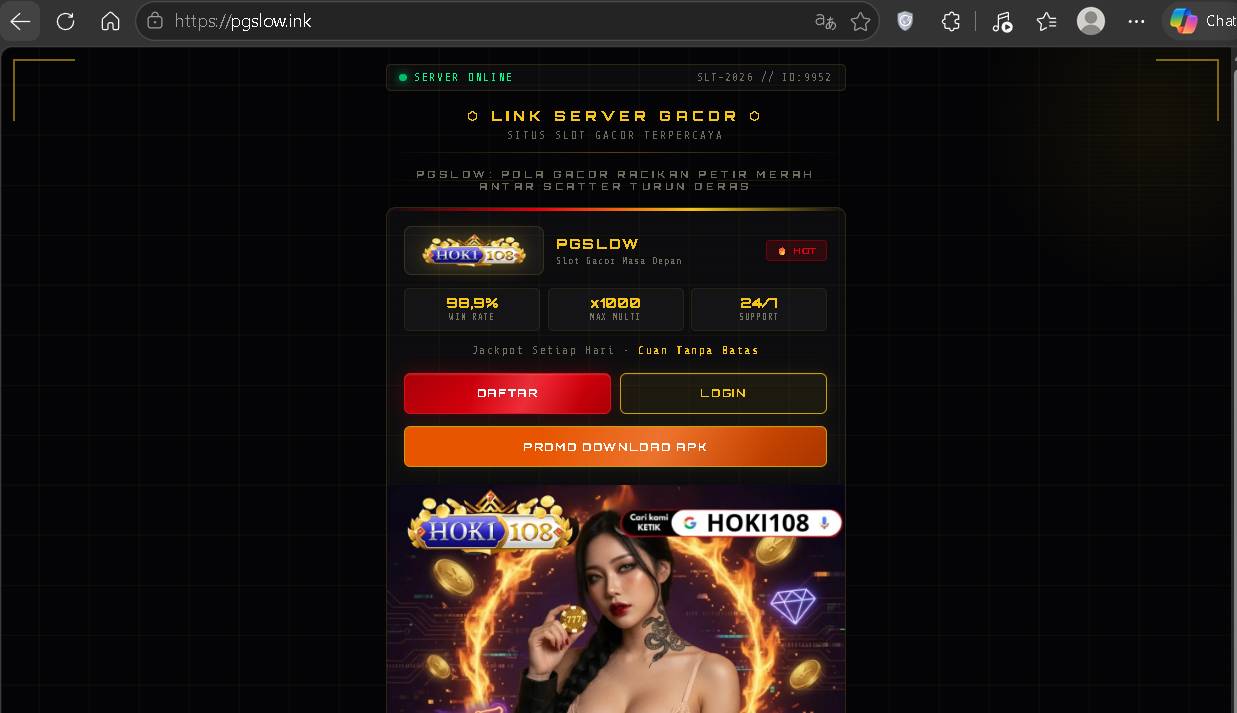
| Forensic Parameter | Technical Finding & Visual Artifacts |
| Active Domain URL | [https://pgslow.ink](https://pgslow.ink) (Observed Node Header: SLT-2026 // ID: 9952) |
| Observed Brand Identifiers | PGSLOW (“Slot Gacor Masa Depan”) / HOKI108 (“Situs Slot Gacor Terpercaya”) |
| On-Screen Linguistic Artifacts | “Pola Gacor Racikan Petir Merah Antar Scatter Turun Deras”, “Cuan Tanpa Batas”, “Jackpot Setiap Hari”, “Cari kami KETIK G HOKI108” |
| Promoted Multipliers & Odds | 98.9% Win Rate (Fabricated PRNG claim), x1000 Max Multi, 24/7 Support badge |
| Direct Distribution Endpoints | Standalone orange action button: PROMO DOWNLOAD APK |
| Primary Interaction Selectors | High-contrast callouts: DAFTAR (Registration) and LOGIN |
| Financial Routing Architecture | Peer-to-peer mule VPAs, unlisted UPI collection endpoints, shadow aggregator wallets, and off-chain crypto rails |
| Regulatory & Licensing Disclosures | Completely Absent. Operating without compliance licenses from any regulated gaming board or consumer protection agency. |
📧 Need Legal Assistance?
Contact the author for legal consultations, case evaluations, and professional inquiries.
Linguistic & Visual Dissection (Evidence-Based from Screenshot)
1. The Domain Namespace Evasion (Pgslow.ink)
The target URL pgslow.ink relies on a multi-tiered evasion strategy. The string borrows the prefix “PG”—a calculated typo-squat on PG Soft (Pocket Games Soft), an established provider in the mobile iGaming space—concatenated with the counter-intuitive suffix “slow” to generate a cheap, unindexed alphanumeric label.
Pairing this label with the .ink generic top-level domain (gTLD) serves operational evasion. The registry allows bulk, automated domain registration with practically nonexistent Know-Your-Customer (KYC) oversight. Because .ink domains are cheap and infrequently flagged by legacy corporate keyword blacklists, the syndicate can rotate these mirrors immediately whenever internet service providers (ISPs) or enforcement agencies block an active node.
2. UI Deconstruction: The Pseudo-Terminal & The “Petir Merah” Hook
The visual layout relies on calculated sensory priming:
- The “Server Online” Illusion: The upper diagnostic readout displaying
🟢 SERVER ONLINEalongsideSLT-2026 // ID: 9952replicates the look of an active cloud console. This is intended to deceive users into believing they are connecting to an exclusive, latency-optimized gaming server rather than a static phishing shell. - The “Petir Merah” Mythos: The header specifically proclaims: “PGSLOW: POLA GACOR RACIKAN PETIR MERAH ANTAR SCATTER TURUN DERAS”. In Southeast Asian gambling slang, “Petir Merah” (Red Lightning) refers directly to high-multiplier bonus strikes in games like Pragmatic Play’s Gates of Olympus. By claiming an automated “concoction” (racikan) guarantees heavy scatter drops (turun deras), the platform promises an algorithmic exploit that simply does not exist.
- Visual Anchor & Urgency Badges: The central figure holds a lucky golden chip inside a blazing ring of fire, flanked by flying coins and glowing diamonds. This visual wealth-anchor works directly alongside the red
HOTtag and the slogan “Cuan Tanpa Batas” (Endless Profits) to suspend skepticism and drive clicks into the bright redDAFTARbutton. - Search Engine Parasitism Prompt: The UI explicitly commands: “Cari kami KETIK G HOKI108” (Find us by typing HOKI108 into Google). This instructs users to create search velocity for specific syndicate keywords, manipulating algorithmic trends and driving brand retention across social media filters.
3. The Cross-Border Proxy Arbitrage
The visual artifacts and text are framed entirely in Indonesian dialect, yet mirror infrastructure of this nature is systematically leveraged in multi-geo campaigns across South Asia. Advertised heavily via compromised social media profiles, surrogate sports streaming feeds, and rogue Telegram channels, Indian users tapping into these networks are redirected based on geo-IP headers into dynamic checkout gateways configured to solicit local Unified Payments Interface (UPI) payments.
5 Critical Technical Deceptions
[ User Lands on Pgslow.ink ]
            │
      ┌─────┴────────────────────────────────┐
      ▼                                      ▼
[ "DAFTAR" / Account Creation ]       [ "PROMO DOWNLOAD APK" ]
      │                                      │
  Rotated Mule Account UPI Request       Off-Market Package (.apk) Sideload
      │                                      │
  Fund Layering & P2P Crypto Channelling  Interception Permissions
      │                                  (`RECEIVE_SMS`, `ACCESSIBILITY`)
      ▼                                      ▼
Interstate Cyber Cell Bank Lien / Freeze   Silent OTP Theft & Account Hijacking
(Section 106 BNSS / 102 CrPC)
1. Transnational Mule Syndicate Integration
When a player initiates a deposit, pgslow.ink does not process the transaction through verified financial gateways. The backend dynamically allocates rotating virtual payment addresses (VPAs) or local bank accounts belonging to recruited “money mules.” Once a UPI transaction is executed, automated liquidity scripts rapidly bounce the capital across intermediate accounts before buying USDT through peer-to-peer crypto exchanges, laundering the funds across borders.
2. Fabricated PRNG & Hardcoded RTP
The interface prominently displays a 98.9% Win Rate and x1000 Max Multi. Legitimate, audited online gaming algorithms maintain certified Pseudo-Random Number Generators (PRNGs) with published house advantages (typically producing RTPs between 92% and 96%). The engine running behind Gacor/Hoki white-label networks runs cracked, client-manipulated code that allows administrators to calibrate volatility, induce deposit streaks, and ensure zero mathematical possibility of sustained profit.
3. Sideloaded APK Vector & Silent OTP Interception
The PROMO DOWNLOAD APK button delivers an unsigned package directly from untrusted server storage. Once manually installed, these files frequently request intrusive Android permissions:
android.permission.RECEIVE_SMS/READ_SMS: Enables the app to read incoming verification messages. Threat actors use this for background OTP interception to authorize balance transfers or password resets.android.permission.BIND_ACCESSIBILITY_SERVICE: Allows malicious actors to execute automated screen taps, log keystrokes, and bypass Google Play Protect restrictions without physical user interaction.
4. Zero Corporate Attribution
The website exhibits complete structural anonymity. There is no verifiable corporate address, no company registration number, no data protection officer contact, and no functional regulatory license. The domain is shielded behind offshore proxy networks designed to resist legal take-downs and law enforcement inquiries.
5. Advance-Fee Withdrawal Roadblocks
The platform is intentionally designed with asymmetric payment flow: deposit channels remain instantly operational, but withdrawal capabilities are artificially halted. When an account attempts to withdraw “winnings,” the system triggers automated failures, demanding “tax fees,” “clearing channel deposits,” or “tier verification payments.” Every supplemental fee submitted is immediately retained, leaving the user permanently locked out.
Suspicious Link or Courier SMS?
Verify URLs, APKs, or parcel alerts against our threat database before clicking.
Emergency Remediation & Financial Recovery
If you have interacted with pgslow.ink, submitted banking details, or processed transactions to these mule networks, immediate mitigation is required:
1. Rapid Fraud Response Protocol
- Call 1930 Immediately: The national financial fraud reporting helpline operates the Citizen Financial Cyber Fraud Reporting and Management System (CFCFRMS). Calling within the “golden hour” enables authorities to deploy an emergency transit-hold on the recipient mule account before funds are converted into crypto assets.
- Lodge Evidence on the Cybercrime Portal: File a formal complaint at cybercrime.gov.in. Upload complete, uncropped transaction receipts displaying the target VPA, beneficiary bank details, the UTR number, and screenshots of the platform interaction.
- Instruct Your Bank to Reverse the Transaction: Contact your bank’s fraud monitoring department immediately. Cite an unauthorized merchant diversion or cyber fraud to request an immediate clawback/chargeback on the transaction.
2. Mitigating a Cyber Cell Debit Freeze (Section 106 BNSS / 102 CrPC)
If your bank informs you that a debit freeze or forensic lien has been placed on your account, your transfer touched an active cyber syndicate account flagged in an ongoing investigation:
- Demand the complete freezing notice from your bank’s nodal officer, including the Crime Reference Number, the originating Police Station/State Cyber Cell, and the Investigating Officer’s (I.O.) contact email.
- Compile a structured paper trail showing your payment context, chat records, and bank statements confirming that you were a victim of an illicit gaming trap rather than an accomplice operating a mule account.
- Submit this evidentiary documentation directly to the investigating officer to secure an official No Objection Certificate (NOC) for lifting the lien on your unaffected balance.
3. Telecommunication Phishing Reporting via Chakshu
If you received the URL or registration invitations via SMS, WhatsApp, or spoofed phone calls, report the sending identifiers through the Chakshu portal on the Department of Telecommunications’ Sanchar Saathi platform (sancharsaathi.gov.in) to aid in blacklisting the syndicate’s operational hardware.
Android Quarantine & Spyware Neutralization
If you tapped PROMO DOWNLOAD APK and installed the sideloaded file on an Android device, treat the hardware as actively compromised:
- Sever All Connectivity: Instantly enable Airplane Mode and disable Wi-Fi to stop remote command-and-control communication and data exfiltration.
- Reboot into Safe Mode:
- Hold the physical power button.
- Long-press the onscreen Power Off or Restart icon until the Reboot to Safe Mode prompt appears. Confirm the reboot. Safe Mode halts all unapproved third-party apps from executing background scripts.
- Strip Device Administrator Permissions:
- Open
Settings➔Security➔Device Admin Apps. - Look for unrecognized applications masquerading as “System Services,” “Gacor Engine,” or “Flash Player.” Toggle off their administrative rights immediately.
- Open
- Remove Malicious Packages:
- Open
Settings➔Apps➔See All Apps. - Locate the downloaded APK or any recently installed, nameless application package and select Uninstall.
- Open
- Verify Core Security Settings:
- Verify under
Settings➔Apps➔Default Appsthat your standard messaging client remains the designated default SMS app. - Open Google Play Store, select your profile, open Play Protect, and execute a full scan to verify system integrity.
- Verify under
High-RPM Cybersecurity Resource Block
🛡️ Essential Personal Defense Tools
- Mobile Antivirus & Malware Removal: Clean deep-seated APK spyware and RAT payloads using an enterprise-grade mobile threat scanner (e.g., Bitdefender Mobile Security or Malwarebytes).
- Identity Theft & Credit Monitoring: Prevent bad actors from leveraging leaked financial data or KYC documents for synthetic loan applications using comprehensive identity monitoring (e.g., Aura or Experian IdentityWorks).
- Anti-Phishing & Traffic Obfuscation VPN: Block rogue surrogate mirrors, malicious scripts, and malicious gambling networks automatically with advanced DNS threat filtering (e.g., NordVPN Threat Protection or Surfshark CleanWeb).
Frequently Asked Questions (FAQ)
Is Pgslow.ink Scam?
Yes, Pgslow.ink is an active online scam. It functions as an uncertified offshore mirror engineered to lure retail users through fabricated 98.9% win probabilities, deceptive visual server prompts, and dynamic mule accounts that systematically withhold deposited funds.
Is Pgslow.ink Legit?
No, Pgslow.ink is completely illegitimate. The website has no corporate registrations, lacks certified gaming licenses, runs unverified slot engines without audited random number generation, and relies on illicit payment rails that directly contravene financial regulations.
Why does Pgslow.ink distribute an off-market APK instead of using the Play Store?
The PROMO DOWNLOAD APK vector is utilized to bypass Google Play Protect security checks. Off-market APK packages distributed by illicit gambling portals often request invasive permissions, such as background SMS reading and Accessibility Services, exposing users to OTP interception and device takeover.
What should I do if my bank account faces a cyber cell freeze after using this site?
If your bank account is frozen under Section 106 BNSS / Section 102 CrPC, your transfer was routed into an active money laundering funnel. You must obtain the Crime Reference Number and Investigating Officer’s contact from your bank, submit proof that you were an unwitting victim, and seek an official NOC from the relevant Cyber Police Station to release the account lien.
Can I retrieve money deposited into Pgslow.ink?
Direct withdrawals through the platform are consistently denied, often accompanied by deceptive demands for additional “tax” or “clearance” fees. Your best chance for recovery is immediate action: report the fraud to the 1930 National Cybercrime Reporting helpline and request a formal transaction dispute through your bank during the golden-hour window.
Every safe click counts. If this post helped, a coffee gesture fuels more scam‑busting investigations.

Related Forensic Teardown • Master Guide
How Domain Churn Scams Keep Illegal Betting Rings Alive →Help Us Spread Awareness
Please share this article to spread awareness. Follow us on social media for more scam alerts.