Ormas.lol Review: High-Risk Scam Gateway, Cross-Border UPI Trap, or Syndicate Mirror?
Executive Summary & Verdict Callout
Verdict: High-Risk Scam Gateway / Unlicensed Financial Funnel.
Ormas.lol operates as an aggressive, cross-border fraudulent portal designed to harvest user capital and compromise mobile security under the guise of an online entertainment and gaming platform. Our forensic analysis reveals a dangerous convergence of deceptive marketing, Southeast Asian white-label gambling syndicates (fronted under the “DEWA90” brand), and high-risk APK distribution vectors.
Operating completely outside recognized regulatory frameworks, the platform deploys asymmetric withdrawal rules, multi-tiered fee extortions, and opaque payment routes that routinely expose unsuspecting participants to severe financial loss, bank account freezes, and malicious data harvesting.
Suspicious Link or Courier SMS?
Verify URLs, APKs, or parcel alerts against our threat database before clicking.
Technical Audit & Forensic Parameters
| Forensic Parameter | Observed Technical Detail / Evidence |
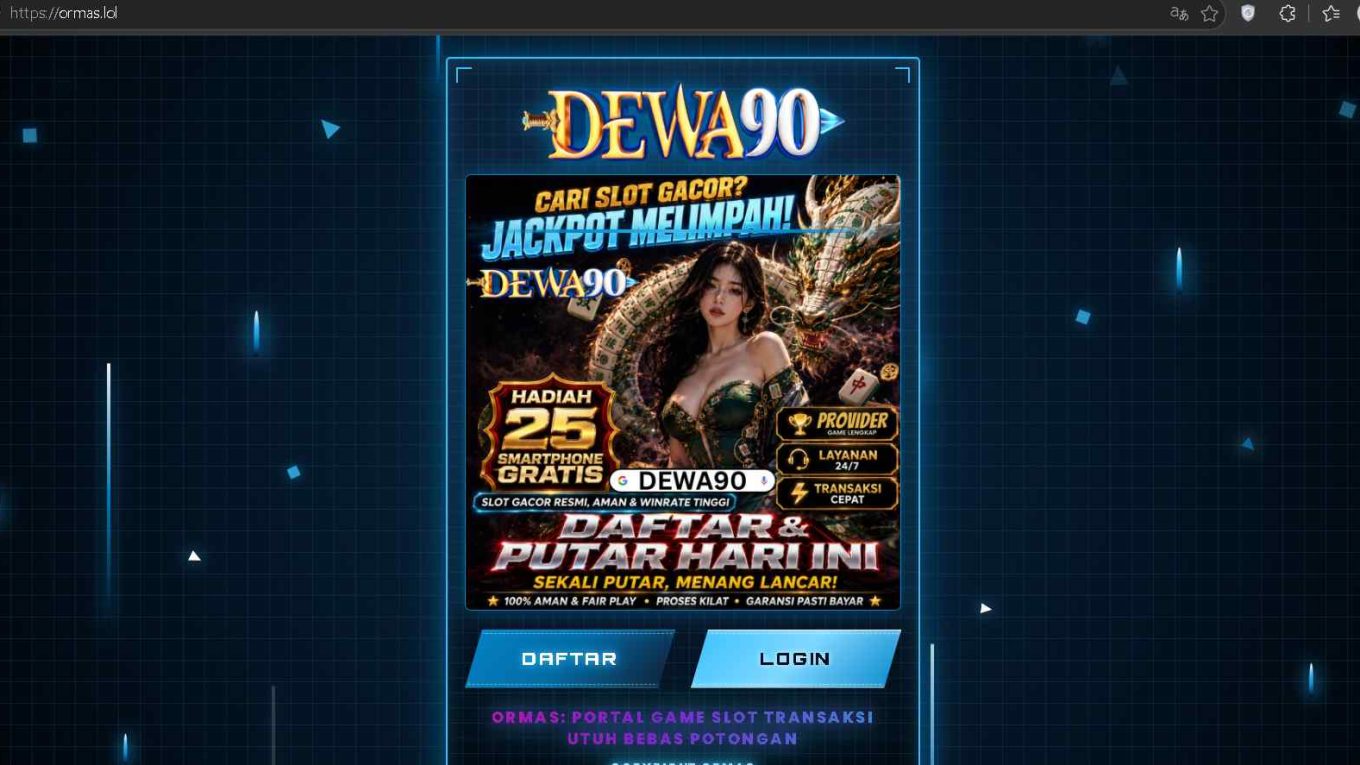
| Active Domain URL | [https://ormas.lol](https://ormas.lol) |
| Observed Brand Names | DEWA90, Ormas Portal Game Slot |
| Foreign / Regional Taglines | “CARI SLOT GACOR?”, “JACKPOT MELIMPAH!”, “HADIAH 25 SMARTPHONE GRATIS”, “DAFTAR & PUTAR HARI INI”, “SEKALI PUTAR, MENANG LANCAR!” |
| Claimed RTP / Multipliers | High win-rate claims (“Winrate Tinggi”, 100% Fair Play, “Garansi Pasti Bayar”) |
| Payment Vectors | UPI gateways, dynamic virtual payment addresses (VPAs), rotating peer-to-peer mule accounts |
| APK Distribution Vectors | Direct sideloading prompts, device permission hooks, third-party package installers |
| Regulatory Status | Completely unlicensed; zero corporate registration, no valid gaming commission credentials, and anonymous WHOIS registry protection |
Linguistic & Visual Dissection (Evidence-Based from Screenshot)
Domain Naming Convention & TLD Strategy
The domain Ormas.lol utilizes a deliberate linguistic engineering strategy. The term “Ormas” (commonly associated with Organisasi Masyarakat or mass organizations in Indonesian socio-political contexts) is paired with the .lol top-level domain (TLD). By selecting a non-traditional gTLD typically associated with humor or casual forums, syndicate operators intentionally bypass primitive corporate firewall keyword filters and automated social media spam blacklists. This low-cost, disposable TLD structure allows operators to rapidly spin up mirror links the moment their primary domain is flagged or blocked by internet service providers.
UI Camouflage & Psychological Hooks
An examination of the UI layout reveals a highly calculated design intended to induce trust and lower visitor inhibition:
- Thematic Aesthetic: Built upon a futuristic, cyber-blue grid background with neon vertical vector light bars, mimicking high-tech financial trading or secure cybersecurity terminals.
- Mascot & Imagery: Features a high-gloss promotional banner starring an AI-rendered or stock glamour model flanked by traditional Asian gaming symbols (mahjong tiles) and a golden dragon mascot, creating an illusion of prestige and high-stakes excitement.
- Deceptive Incentive Anchors: The interface heavily promotes a bait hook: “HADIAH 25 SMARTPHONE GRATIS” (Free Smartphone Giveaway) alongside sweeping guarantees like “100% AMAN & FAIR PLAY” and “GARANSI PASTI BAYAR” (Guaranteed Payout). These psychological triggers exploit cognitive biases, convincing victims that the platform is backed by a secure corporate entity.
Cross-Border Mismatch & Target Demographics
A glaring forensic anomaly is the linguistic mismatch on the platform. The banners are entirely written in Indonesian (“Cari slot gacor?” translating to “Looking for a loose/easy slot machine?”), yet the operational funnel is heavily pushed toward Indian digital users via Telegram channels, WhatsApp groups, and surrogate streaming ads. This jurisdictional disconnect is a hallmark of international cybercrime syndicates that route funds through multi-layered cross-border laundering channels to frustrate local law enforcement agencies.
5 Critical Technical Deceptions
- Backend Syndication & White-Label Laundering: Ormas.lol is not an independent gaming operator; it is a front-end shell connected to centralized, unregulated white-label APIs. These backends allow anonymous syndicates to manipulate game outcomes in real time while shielding the ultimate beneficiaries from legal liability.
- Fabricated Mathematical Odds (RNG/RTP Violations): Despite bold UI claims of “Winrate Tinggi” and fair play, the underlying software lacks any certified Random Number Generator (RNG) audit from reputable testing laboratories like eCOGRA or iTech Labs. Game parameters are dynamically adjusted on remote servers to ensure early, minor wins followed by catastrophic, unrecoverable losses.
- Android APK Permission Abuse: Users registering on the platform are frequently nudged to download standalone application packages (
.apk). Once installed, these malicious payloads request dangerous system permissions—such asRECEIVE_SMS,READ_SMS, andBIND_ACCESSIBILITY_SERVICE—allowing threat actors to execute background OTP interception and automated financial malware routines. - Anonymous Ownership & Cloudflare Masking: The domain utilizes enterprise-grade reverse proxies and privacy protection services to mask its true origin servers, physical hosting locations, and ownership details, leaving victims with zero legal recourse or points of contact.
- Upfront Clearance & Tax Fee Extortion: When a user manages to accumulate a nominal winning balance and attempts a withdrawal, the platform artificially blocks the transaction. Victims are informed that they must pay an upfront “tax clearance fee,” “channel activation deposit,” or “risk management verification charge” to release funds. Once paid, the operators demand further fees until the victim ceases communication.
Emergency Remediation & Financial Recovery (India & Global Context)
If you have already interacted with Ormas.lol, deposited funds via UPI, or shared personal financial information, execute the following emergency containment protocol immediately:
- Golden-Hour Cyber Helpline Reporting: Immediately dial 1930 (the national cybercrime helpline in India) or file an exhaustive incident report on the official portal at cybercrime.gov.in. Prompt reporting within the “golden hour” significantly increases the window for freezing funds in transit.
- Handling Cyber Cell Bank Account Freezes: If your bank account has been slapped with a debit freeze, lien, or hold under Section 106 of the Bharatiya Nagarik Suraksha Sanhita (BNSS) or Section 102 of the CrPC due to funds received from or sent to mule accounts associated with this syndicate:
- Contact your bank’s home branch cyber cell nodal officer to obtain the exact FIR number, Cyber Cell station, and investigating officer (IO) details tied to the lien.
- Submit a formal legal representation demonstrating your lack of criminal intent, including transaction statements, chat logs, and proof that you were an unwitting victim of an online financial fraud portal.
- Reporting Communication Vectors: Report all fraudulent WhatsApp groups, Telegram channels, and SMS phishing links used to promote Ormas.lol to the Department of Telecommunications (DoT) via the Chakshu portal on the Sanchar Saathi platform.
Android Quarantine & Spyware Neutralization
If you visited Ormas.lol on an Android device or downloaded any associated .apk file, execute these steps to disinfect your hardware:
- Boot into Safe Mode: Restart your smartphone into Safe Mode to temporarily disable all third-party applications and prevent malicious background services from executing.
- Revoke Device Administrator Access: Navigate to Settings > Security > Device Administrator Apps (or Special App Access). Inspect the list for any unfamiliar applications possessing administrator privileges and immediately disable them.
- Purge Hidden APK Packages: Go to Settings > Apps, locate any sideloaded applications or untrusted tools downloaded around the time of your interaction with the site, and completely uninstall them.
- Reset Default Messaging & Permissions: Verify your default SMS and accessibility settings to ensure no unauthorized app retains reading access to your incoming text messages and one-time passwords (OTPs). Perform a full system scan using a trusted mobile security solution.
Security Resource Block
🛡️ Recommended Digital Safety Stack
- Mobile Antivirus & Malware Removal: Protect your smartphone from background APK spyware, keyloggers, and malicious permission hooks with enterprise-grade mobile security suites (e.g., Bitdefender Mobile Security or Malwarebytes).
- Identity Theft & Credit Monitoring: Safeguard your personal PII, PAN, and Aadhaar data against unauthorized financial loan applications using active credit monitoring services.
- Anti-Phishing VPN: Shield your browsing traffic from DNS hijacking, rogue redirect scripts, and malicious IP logging with a verified zero-log Virtual Private Network.
Frequently Asked Questions (FAQ)
Is Ormas.lol a scam?
Yes, absolutely. Ormas.lol is an unlicensed fraudulent portal engineered to deceive users through false winning promises, fake promotional giveaways, and manipulated gaming mechanics designed solely to misappropriate deposited funds.
Is Ormas.lol legit?
No. The platform possesses no legal corporate registration, holds zero valid gaming licenses, and operates completely outside regulatory oversight, making every transaction on the site unsafe.
Why is my withdrawal blocked on Ormas.lol?
Withdrawals are intentionally blocked by design. The platform uses artificial friction—such as demanding upfront taxes, channel activation fees, or verification deposits—to extract additional money from victims before cutting off all communication.
Why has my bank account been frozen after interacting with this site?
When you transfer funds to or receive funds from platforms like Ormas.lol, you are often interacting with layered mule accounts. Law enforcement cyber cells tracking illicit money flows routinely place debit freezes and liens on all linked bank accounts under Section 106 BNSS / 102 CrPC.
What should I do if I downloaded an APK file from Ormas.lol?
Immediately disconnect your device from the internet, boot into Safe Mode, revoke any Device Administrator permissions granted to unfamiliar apps, uninstall the rogue APK package, and change your netbanking and UPI PINs from a secure, uncompromised device.
Every safe click counts. If this post helped, a coffee gesture fuels more scam‑busting investigations.

Related Forensic Teardown • Master Guide
How Domain Churn Scams Keep Illegal Betting Rings Alive →Help Us Spread Awareness
Please share this article to spread awareness. Follow us on social media for more scam alerts.