Menara.lol Review: Legit Gaming Hub, UPI Trap, or Syndicate Mirror?
Executive Summary & Verdict Callout
Menara.lol is an active, high-risk fraudulent surrogate funnel and uncertified offshore gambling mirror operating as a malicious acquisition vector for the “DEWA90” syndicate. Exploiting a humor-oriented generic top-level domain (.lol) and deceptive architectural keywords to slip through corporate web filters, the portal acts as a financial collection trap funneling retail traffic into illicit money-laundering channels.
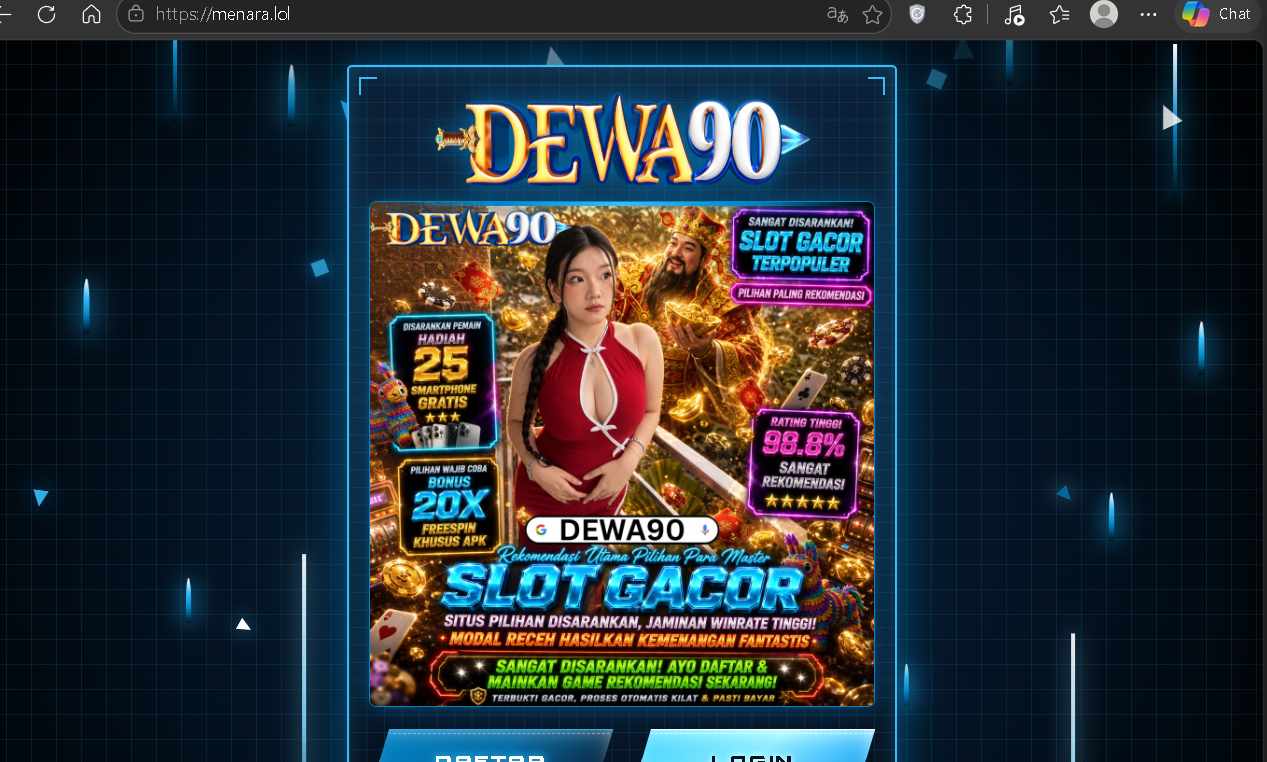
The site employs deceptive hooks—such as a fabricated “98.8% Rating Tinggi / Sangat Rekomendasi” score, fraudulent hardware incentives (“Hadiah 25 Smartphone Gratis”), and an unverified sideloaded Android app (“Bonus 20X Freespin Khusus APK”). Sending deposits to this platform exposes users to total loss of funds and immediate legal fallout, most critically an interstate bank account cyber cell debit freeze under Section 106 of the Bharatiya Nagarik Suraksha Sanhita (BNSS) / Section 102 CrPC.
Technical Audit & Forensic Parameters
| Forensic Parameter | Technical Finding & Visual Evidence |
|---|---|
| Active Domain URL | [https://menara.lol](https://menara.lol) (Observed browser URL bar) |
| Observed Syndicated Brands | DEWA90 (Stylized sword motif inside the “D”, dual top and central branding placements) |
| On-Screen Linguistic Artifacts | “SLOT GACOR TERPOPULER – PILIHAN PALING REKOMENDASI”, “HADIAH 25 SMARTPHONE GRATIS”, “PILIHAN WAJIB COBA BONUS 20X FREESPIN KHUSUS APK”, “MODAL RECEH HASILKAN KEMENANGAN FANTASTIS”, “TERBUKTI GACOR, PROSES OTOMATIS KILAT & PASTI BAYAR” |
| Claimed Odds & Multipliers | RATING TINGGI 98.8% (Fabricated PRNG metric), BONUS 20X FREESPIN, 5-star rating graphic badge J |
| Direct Distribution Endpoints | Standalone promotional vector: PILIHAN WAJIB COBA BONUS 20X FREESPIN KHUSUS APK |
| Portal Action Selectors | High-contrast registration: DAFTAR and user authentication: LOGIN |
| Financial Settlement Infrastructure | Dynamic peer-to-peer mule UPI IDs, unlisted merchant intent links, shadow cryptocurrency liquidity pools |
| Regulatory & Licensing Disclosures | Completely Absent. Zero operational licensing, dispute escalation protocols, or corporate audits filed under recognized gaming jurisdictions. |
Linguistic & Visual Dissection (Evidence-Based from Screenshot)
1. The “Menara” Disguise & The .lol TLD Evasion
The domain menara.lol demonstrates tactical namespace obfuscation. The word “Menara” translates to “Tower” or “Minaret” in Indonesian and Malay, evoking imagery of strength, stature, and institutional height. This naming convention is deliberately selected to project stability to cautious visitors navigating away from blocked casino domains.
Pairing this term with the .lol generic top-level domain serves operational evasion. Corporate firewalls, enterprise proxy layers, and social media content filters typically flag keywords related to wagering or finance, but categorize .lol alongside entertainment, humor, and meme repositories. Bulk .lol registries impose virtually zero Know-Your-Customer (KYC) friction, allowing the DEWA90 syndicate to mass-register and deploy mirror domains instantly whenever telecom operators or cyber police units issue DNS takedown notices.
2. UI Camouflage: Cultural Imagery & Hardware Bait
The visual composition relies on calculated psychological manipulation:
- The “Smartphone Gratis” Incentive: Positioned on the left side is a high-contrast promotional card: “DISARANKAN PEMAIN – HADIAH 25 SMARTPHONE GRATIS”, displaying the render of a flagship smartphone draped in gold coins. Promising physical consumer electronics for mere registration lowers user resistance, drawing in budget-conscious demographics through an advance-fee lure.
- The Wealth Deity & Sensual Framing: Flanking the central female model (dressed in a crimson, keyhole-slit cheongsam) is an armored representation of Caishen, the Chinese God of Wealth, holding a glowing golden ingot (sycee). Surrounded by traditional pinatas, flying gold ingots, floating playing cards, and glowing red lanterns, this cultural imagery creates the impression of sudden, divinely sanctioned wealth.
Suspicious Link or Courier SMS?
Verify URLs, APKs, or parcel alerts against our threat database before clicking.
- The “Khusus APK” Trojan Trap: The interface highlights a dedicated download card: “PILIHAN WAJIB COBA BONUS 20X FREESPIN KHUSUS APK”. Offering a 20x free-spin multiplier only on the sideloaded application pushes mobile visitors off sandboxed web browsers and into installing an unverified APK package directly onto their devices.
- Algorithmic Search Manipulation (The Google Search Pill): Sitting directly below the central model is a simulated Google search box reading “G DEWA90”. This prompt instructs users to manually look up the brand on search engines, artificially driving search volume to preserve the syndicate’s search footprint against ongoing domain blocks.
- The “Modal Receh” Reassurance: At the bottom, the banner reassures users with “MODAL RECEH HASILKAN KEMENANGAN FANTASTIS” (Small change yields fantastic wins) and claims “PASTI BAYAR” (Guaranteed Payout). This framing is designed to overcome hesitation regarding transaction security.
3. Cross-Border Traffic Funnels
While the visual artifacts and text are framed entirely in Indonesian dialect, the platform is deployed within an international traffic funnel. Syndicates purchase surrogate ad placements across pirated anime networks, sports streaming feeds, and rogue Telegram tipster groups targeting Indian and South Asian demographics. When non-Indonesian IP addresses land on menara.lol, dynamic IP-forwarding scripts adapt the checkout portal to local payment gateways, serving Unified Payments Interface (UPI) corridors directly to the visitor.
5 Critical Technical Deceptions
[ User Lands on Menara.lol ]
               │
       ┌───────┴────────────────────────────────┐
       ▼                                        ▼
[ "DAFTAR" (Account Creation) ]       [ "BONUS 20X FREESPIN KHUSUS APK" ]
       │                                        │
  Rotating Mule UPI / VPA Route            Unsigned Android APK Sideload
       │                                        │
  Multi-Tier P2P Crypto Laundering         Intrusive Spyware Permissions
       │                                   (`RECEIVE_SMS`, `ACCESSIBILITY`)
       ▼                                        ▼
Interstate Cyber Cell Bank Lien / Freeze      Silent OTP Interception & Account Drain
(Section 106 BNSS / 102 CrPC)
1. Transnational Mule Syndicate Integration
Deposits initiated on menara.lol bypass certified corporate merchant accounts. Transactions execute via dynamic API calls serving rotating UPI Virtual Payment Addresses (VPAs) assigned to recruited money mules. These accounts—often procured from financially vulnerable individuals—funnel the deposits through layered intermediary tiers before converting the fiat currency into crypto assets (USDT) on P2P desks. Consequently, the depositor’s personal account is directly implicated in illegal fund transfers.
2. Algorithmic Rigging & Simulated RTP
The interface prominently displays a Rating Tinggi 98.8% badge alongside a 5-star graphic. Legitimate, audited online gaming algorithms maintain certified Pseudo-Random Number Generators (PRNGs) with published house advantages (typically producing RTPs between 92% and 96%). The engine running behind DEWA90 uses manipulated, client-side scripts where administrators can adjust win frequencies to induce deposits before initiating a complete liquidity freeze.
3. Sideloaded APK Vector & Background OTP Interception
The BONUS 20X FREESPIN KHUSUS APK banner delivers an unverified package directly from untrusted server storage, bypassing Google Play Protect. Decompiled variants of these syndicate APKs frequently reveal high-risk Android permissions:
android.permission.RECEIVE_SMS&READ_SMS: Grants silent access to incoming SMS streams, allowing threat actors to intercept bank-issued one-time passwords (OTPs).android.permission.BIND_ACCESSIBILITY_SERVICE: Enables the malicious payload to log keystrokes, capture screen elements, and authorize background fund transfers without the user’s manual input.
4. Zero Corporate Attribution & Infrastructure Obfuscation
Menara.lol provides zero corporate disclosures. There is no registered company name, no physical headquarters address, no data protection officer contact, and no functional regulatory license. The domain is routed through bulletproof reverse proxy servers configured to ignore DMCA notices and law enforcement takedown requests.
5. Advance-Fee Withdrawal Blocks & Fabricated Audits
Deposits clear instantaneously, but withdrawals are blocked by design. Once a user attempts to cash out their balance or simulated winnings, the platform issues automated security flags claiming “tier verification mismatch,” “system audit failure,” or “clearance tax required.” The user is instructed to deposit an upfront processing fee to release the queue. Every additional fee transferred is stolen, and the account is ultimately terminated.
Emergency Remediation & Financial Recovery
If you have transferred funds to, shared personal data with, or downloaded software from menara.lol, execute these containment steps immediately:
1. Golden-Hour Fraud Response
- Call 1930 Helpline Immediately: If you are in India, report the incident immediately via the National Cybercrime Reporting Helpline (1930). Dialing within the “golden hour” allows authorities to notify participating banks and freeze the recipient mule account before the funds are dispersed into crypto channels.
- Lodge an Official Case at cybercrime.gov.in: File a comprehensive fraud dossier on the National Cybercrime Reporting Portal. Upload unedited screenshots of your transaction details, the recipient VPA, UTR numbers, and any chat logs from the platform.
- Initiate a Bank Dispute: Immediately alert your issuing bank’s fraud control department. Report that you were redirected to a fraudulent peer-to-peer mule account via deceptive merchant misrepresentation, and file an unauthorized transaction dispute and recall.
2. Resolving a Cyber Cell Debit Freeze (Section 106 BNSS / 102 CrPC)
If your bank account is placed under a debit freeze or police lien after paying this platform, your transfer connected directly into an active cybercrime syndicate investigation:
- Contact your bank’s nodal officer to obtain the formal Freezing Order, which includes the Crime Reference Number, the originating Police Station/State Cyber Cell, and the Investigating Officer’s (I.O.) contact email.
- Compile a complete evidentiary paper trail showing your payment flow, proof of the fraudulent gameplay, and bank statements establishing that you were an unwitting victim rather than an accomplice operating a mule account.
- Submit this dossier directly to the Investigating Officer to request a No Objection Certificate (NOC) and unfreeze the unencumbered balance in your bank account.
3. Report Phishing Vectors via Chakshu
If you received links to menara.lol via unsolicited SMS broadcasts, WhatsApp messages, or spoofed phone numbers, report these details on the Chakshu portal within the Department of Telecommunications’ Sanchar Saathi platform (sancharsaathi.gov.in) to aid in blacklisting the perpetrators’ telecommunication assets.
Android Quarantine & Spyware Neutralization
If you interacted with the BONUS 20X FREESPIN KHUSUS APK banner and installed the sideloaded file, treat your mobile device as compromised:
- Sever Network Connections: Turn on Airplane Mode and disable Wi-Fi immediately to cut off real-time exfiltration of credentials and remote command-and-control access.
- Reboot into Safe Mode:
- Hold down your phone’s physical Power button.
- Long-press the onscreen Power Off or Restart icon until the Reboot to Safe Mode prompt appears. Confirm the selection. Safe Mode boots the Android OS with all downloaded third-party code completely deactivated.
- Revoke Device Administrator Rights:
- Open
Settings➔Security➔Device Admin Apps. - Look for unrecognized applications masquerading as “System Updates,” “Menara Engine,” or “Media Service” and immediately toggle off their administrative rights.
- Open
- Uninstall the Malicious Package:
- Open
Settings➔Apps➔See All Apps. - Find the downloaded APK or any newly installed, unfamiliar applications and tap Uninstall.
- Open
- Restore Messaging Defaults & Scan the Device:
- Navigate to
Settings➔Apps➔Default Appsand verify that your device’s native messaging client is assigned as the default SMS application. - Open the Google Play Store, tap your profile icon, open Play Protect, and execute a full device security scan.
- Navigate to
Cybersecurity Resource Block
🛡️ Personal Threat Defense Suite
- Mobile Antivirus & Spyware Removal: Identify and clean deep-seated APK spyware and RAT payloads using an industry-recognized mobile security scanner (e.g., Bitdefender Mobile Security or Malwarebytes).
- Identity Theft & Credit Protection: Guard your personal details and prevent unauthorized loans or account creation if your KYC data was shared on unverified portals (e.g., Aura or Experian IdentityWorks).
- Anti-Phishing & Traffic Protection VPN: Automatically block fraudulent mirrors, rogue proxies, and malicious scripts at the DNS layer using advanced web-filtering software (e.g., NordVPN Threat Protection or Surfshark CleanWeb).
Frequently Asked Questions (FAQ)
Is Menara.lol Scam?
Yes, Menara.lol is an active online scam. The website functions as an unlicensed surrogate proxy that uses counterfeit 98.8% rating metrics, deceptive hardware giveaways (“25 Smartphone Gratis”), and rotating mule payment rails to steal user deposits without honoring withdrawals.
Is Menara.lol Legit?
No, Menara.lol is completely illegitimate. It holds no valid gaming licenses, has no verified corporate registration, and uses a comedic domain extension (.lol) alongside structural camouflage (“Menara”) to evade security filters while operating unregulated, predatory software.
What is the risk of downloading the “Bonus 20X Freespin Khusus APK”?
The promoted APK bypasses Google Play Protect checks. Sideloading this unverified file exposes your smartphone to banking spyware and Trojans capable of abusing SMS and Accessibility permissions to intercept banking OTPs and steal private account information.
Why is my bank account frozen after depositing into Menara.lol?
Your account was likely placed under a debit freeze under Section 106 BNSS / Section 102 CrPC because your payment was routed into an active money-laundering mule account. When cyber police departments investigate syndicate accounts, every linked account in the transaction trail is temporarily frozen.
Can I withdraw my deposited funds or winnings from Menara.lol?
No. Balances displayed on the screen are simulated by the site’s operators. When you attempt to withdraw, the platform blocks the transaction and often demands additional verification fees or clearance taxes, which simply leads to further financial loss.
Every safe click counts. If this post helped, a coffee gesture fuels more scam‑busting investigations.

Related Forensic Teardown • Master Guide
How Domain Churn Scams Keep Illegal Betting Rings Alive →Help Us Spread Awareness
Please share this article to spread awareness. Follow us on social media for more scam alerts.