Mawara.world Investigation: The Hidden Risks of This Predatory Casino Portal
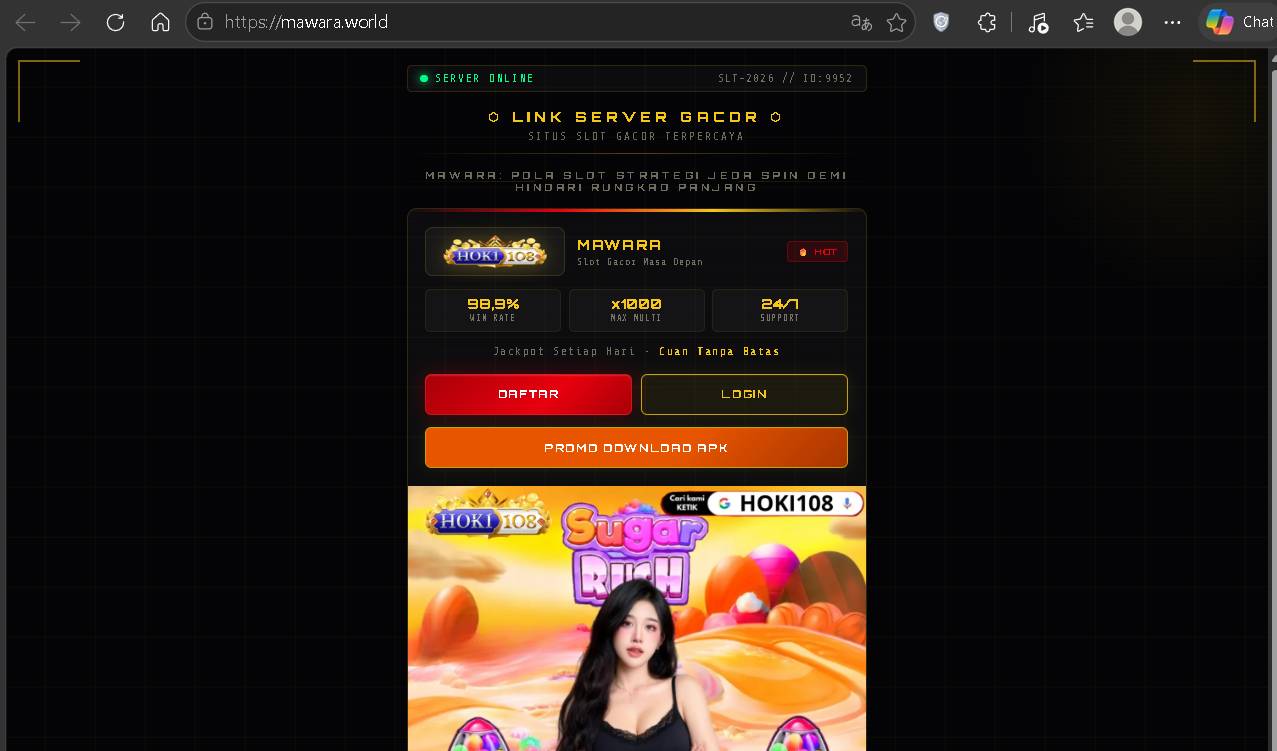
The website Mawara.world operates as an entry point for an illicit digital gambling ring, presenting a serious threat in the form of an unregulated, black-market “Judi Online” (Judol) scam. At first glance, the webpage appears to be a sleek gaming hub branded under names like HOKI108, featuring flashy neon graphics and promises of astronomical returns.
Behind this polished exterior lies an aggressive financial trap designed to drain user balances while harvesting sensitive credentials. Instead of providing licensed, fair entertainment, portals operating under generic domains like Mawara.world act as transient landing pages engineered to evade regulatory takedowns and capture user deposits through untraceable payment channels.
What Does Mawara.world Claim and Offer?
The landing page positions itself as an elite, high-yield gaming portal:
- Guaranteed Payout Claims: The site advertises a “98.9% Win Rate” alongside a “x1000 Max Multiplier”, presenting high-risk casino games as consistent income opportunities.
- Game Aggregation: It advertises access to prominent slot clones (such as themed titles like Sugar Rush), live dealer tables, sportsbook wagering, and regional lotteries (togel).
- Automated Convenience: Marketing slogans highlight 24/7 technical support, instant deposit channels, and unlimited daily cash-out capabilities (“Cuan Tanpa Batas”).
- Direct Mobile Installations: The interface features a prominent “PROMO DOWNLOAD APK” button, urging visitors to bypass standard app stores and install proprietary software directly onto their mobile devices.
Suspicious Link or Courier SMS?
Verify URLs, APKs, or parcel alerts against our threat database before clicking.
Behind the Screen: How the Platform Operates
Mawara.world functions as a redirect gateway (link alternatif or link server gacor). Visitors are not connecting directly to a registered, legally accountable corporation. Instead, clicking the registration or login buttons routes users to mirrored offshore hosting setups designed to mask operator identities.
Once an account is registered using a mobile phone number and bank details, users are instructed to transfer funds via peer-to-peer digital wallets or individual bank checking accounts. The games presented run on uncertified software scripts where house edges and payout frequencies can be altered behind the scenes. When a player attempts to withdraw accumulated balances, the system stalls—either by imposing impossible wagering turnover requirements or by locking the account entirely under the guise of technical audits.
Deep Dive: The “Slot Gacor” Trap and Mobile Malware (APK) Risks
The most hazardous element of Mawara.world is its dual-threat operational model: combining psychological gaming deception with raw mobile security exposure.
The “Slot Gacor” Psychological Trap
The site leans heavily on regional gaming slang, framing its system as an elite “Server Gacor”. The word gacor implies a machine that is loose, constantly striking winning lines, and easily exploited by savvy players.
To reinforce this illusion, the portal promotes specific play patterns—touting phrases like “Pola slot strategi jeda spin demi hindari rungkad panjang” (a spin-pause strategy to avoid devastating losses). This is a deliberate psychological ploy known in fraud psychology as an illusion-of-control trap.
By leading users to believe that specific sequences of manual spins or strategic pauses can bypass the underlying mathematics, the operators keep players wagering real money on games that are fundamentally rigged. Legitimate slot titles rely on true pseudo-random mathematics; they do not possess secret timing codes that grant retail players a guaranteed edge.
Player Safety Blueprint: Prevention Rules & Actionable Solutions
Protect your digital assets before interacting with unverified gambling mirrors, or follow the mitigation sequence if you have already shared data.
Never pay secondary “clearance taxes,” “unlock fees,” or “verification deposits.” Unregulated syndicates use these requests to extract extra funds before blocking your account.
Uninstall any browser-downloaded package immediately. Reboot into Safe Mode, run an updated antivirus scan, and revoke any suspicious SMS or Accessibility permissions.
Reset passwords on any email accounts, crypto wallets, or payment platforms that shared login credentials with the mirror site. Turn on app-based 2FA (e.g., Google Authenticator).
If you deposited using debit or credit rails, call your issuing bank’s dispute desk immediately to file a chargeback under merchant fraud or failure of service delivery.
Report and block WhatsApp or Telegram spam numbers. Ignore third-party “fund recovery agents” claiming they can hack back your balance for an upfront retainer.
Mobile Malware and Rogue APK Sideloading Risks
While losing funds to rigged odds is damaging, sideloading the platform’s unverified Android application package (APK) introduces catastrophic device-level vulnerabilities:
- Bypassing App Store Sandboxing: Official app marketplaces scan application packages for known malicious code signatures, unauthorized permission escalations, and backdoors before approval. Downloading an APK directly from Mawara.world removes every foundational security barrier provided by your device’s operating system.
- SMS Stealers and Two-Factor Authentication (2FA) Interception: Rogue casino APKs frequently request broad permissions, including
READ_SMSandRECEIVE_SMS. This allows malicious background services to silently intercept incoming one-time passwords (OTPs) sent by your commercial bank, email provider, or cryptocurrency exchange. - Accessibility Service Abuse: Sophisticated Android banking trojans abuse Android’s Accessibility Services to capture keystrokes (keylogging), read screen text, and perform unauthorized account actions directly over your banking applications.
- Persistent Spyware and Contact Scraping: Once installed, rogue APKs often vacuum device contact lists, call logs, and location data. This gathered intelligence is routinely fed to illegal debt collection syndicates (pinjol ilegal) and high-pressure telemarketing scam rings.
5 Critical Red Flags on Mawara.world
+---------------------------------------------------------------------------------------+
|                               MAWARA.WORLD THREAT MATRIX                              |
+------------------------------------+--------------------------------------------------+
| Risk Factor                        | Concrete Diagnostic Indicator                    |
+------------------------------------+--------------------------------------------------+
| 1. Fabricated Win Metrics          | Advertises impossible fixed 98.9% win rates      |
| 2. Sideloaded APK Prompts          | Bypasses Google Play/App Store security checks   |
| 3. Pseudo-Scientific "Pola" Advice | Exploits cognitive biases with false spin tricks |
| 4. Ephemeral Infrastructure        | Uses throwaway mirror domains (.world)           |
| 5. Zero Statutory Licensing        | Lacks regulatory oversight or player protections |
+------------------------------------+--------------------------------------------------+
1. Mathematically Impossible Payout Guarantees
Advertising an overarching 98.9% Win Rate is a direct indicator of deceptive marketing. Certified casino titles operate with theoretical Return to Player (RTP) parameters calculated over millions of spins—they never offer flat, near-certain win probabilities. Real mathematical systems acknowledge variance; black-market operations manufacture deceptive metrics to entice deposits.
2. High-Pressure Prompts to Sideload Unknown Applications
A gambling storefront pushing direct .apk downloads is a critical cybersecurity red flag. Legitimate, regulated international operators deploy native apps through verified app stores that comply with strict developer policies and code integrity audits. Unsigned APK downloads from random domains are a primary distribution method for mobile malware.
3. Exploitation of “Pola Slot” Pseudo-Strategies
Promoting gameplay formulas that promise to avoid financial wipeouts (hindari rungkad) demonstrates bad-faith manipulation. Real iGaming regulatory standards forbid operators from advertising false strategies that guarantee outcomes or mislead consumers regarding house odds.
4. Throwaway Domain Architecture
The .world top-level domain, combined with internal identifiers like SLT-2026 // ID:9952, indicates that this website is simply one disposable node in an expansive network of mirror links. Illicit networks cycle through disposable web addresses as soon as telecommunication regulators and cybersecurity providers block active URLs.
5. Absence of Verified Licensing and Corporate Governance
The site carries no registered company details, no registered physical address, and no verifiable licensing credentials from recognized jurisdictions like the Malta Gaming Authority, the UK Gambling Commission, or the Curacao Gaming Control Board. Without a verifiable license, users possess zero legal standing to dispute withheld balances or audit code integrity.
Immediate Steps to Protect Your Money and Personal Data
If you have visited Mawara.world, submitted personal details, or downloaded files from the platform, take these decisive security measures immediately:
- Uninstall Any Sideloaded Apps Immediately: If you tapped “PROMO DOWNLOAD APK” and installed the package on your phone, go to your device settings, locate the app, clear its storage cache, and uninstall it. Run a thorough scan using a reputable mobile antivirus tool like Bitdefender, Malwarebytes, or Sophos.
- Revoke Dangerous Device Permissions: Check your device settings under Accessibility, Special App Access, and Display Over Other Apps. Ensure no unrecognized services hold permission to read screen content or control system inputs.
- Contact Your Financial Institution: If you transferred funds to unverified checking accounts or shared your debit card/banking numbers, reach out to your bank’s fraud prevention unit immediately. Request a block on suspicious direct debits and request a replacement card if necessary.
- Activate Credit Monitoring and Fraud Alerts: When your full legal name, mobile number, and banking credentials are entered into unverified portals, they are often shared across identity fraud networks. Placing a fraud alert or credit freeze with major credit reporting bureaus helps prevent identity theft and unauthorized line-of-credit openings.
- Report the Domain: Forward the URL to national internet safety portals (such as your local consumer protection bureau, the FBI’s IC3, or national content filtering registries like Indonesia’s Aduan Konten) to help speed up domain takedowns and protect other users.
Frequently Asked Questions (FAQ)
1. Is Mawara.world a scam?
Yes. Mawara.world exhibits the definitive hallmarks of an unlicensed, predatory black-market gambling trap. It combines deceptive win metrics, unlicensed game hosting, and unverified software downloads to extract funds and exploit user devices without providing a secure or fair gaming environment.
2. Is Mawara.world legit?
No. Mawara.world is not a legitimate online gaming or casino operator. It lacks valid licensing from recognized international regulatory bodies, operates through disposable hosting infrastructure, and fails to disclose basic corporate registration details.
3. What makes the APK download on Mawara.world dangerous?
Downloading an application package directly from an unverified website bypasses mobile operating system security protections. Sideloaded casino APKs frequently request invasive permissions that can allow bad actors to monitor device usage, steal one-time authentication codes (OTPs), and intercept online banking credentials.
4. What does “Server Gacor” mean on sites like Mawara.world?
The term “Server Gacor” is a regional marketing phrase used to convince prospective players that a server or game is configured to deliver frequent, massive payouts. In reality, it is a psychological persuasion tool used by unregulated platforms to solicit deposits on rigged games.
5. Can a “pola slot” strategy really prevent losses?
No. Slot outcomes depend entirely on underlying software algorithms and house mathematical advantages. Payouts cannot be systematically outmaneuvered by pausing spins or altering tap intervals. Claiming that a specific timing formula prevents losses (anti-rungkad) is a deceptive practice used to keep players wagering.
6. Can I recover funds sent to Mawara.world?
Recovering funds sent to illicit black-market gambling sites is very challenging because transactions typically flow through money mule bank accounts or unmonitored digital wallets. While you should inform your bank’s unauthorized transaction desk immediately, remain cautious of third-party “asset recovery services” online that demand upfront fees to retrieve lost capital.
7. Why do black-market casinos constantly switch domain names?
Illegal gambling websites face constant operational bans and network firewalls from government watchdogs and internet service providers. Operators build automated mirroring systems on cheap domains like .world or .lol so they can migrate their player traffic as soon as an older link gets blocked.
8. How can I verify if an online casino platform is legally safe?
A genuine online casino will operate in a jurisdiction where digital betting is formally legalized and regulated. It will display a clear, clickable licensing badge issued by a respected authority, use industry-standard HTTPS security with commercial merchant gateways, and host games tested for fairness by certified testing laboratories like eCOGRA or iTech Labs.
Every safe click counts. If this post helped, a coffee gesture fuels more scam‑busting investigations.

Help Us Spread Awareness
Please share this article to spread awareness. Follow us on social media for more scam alerts.