HexTrainer Review: Game Trainer Library Features, Safety Analysis, and Safe Modding Guide
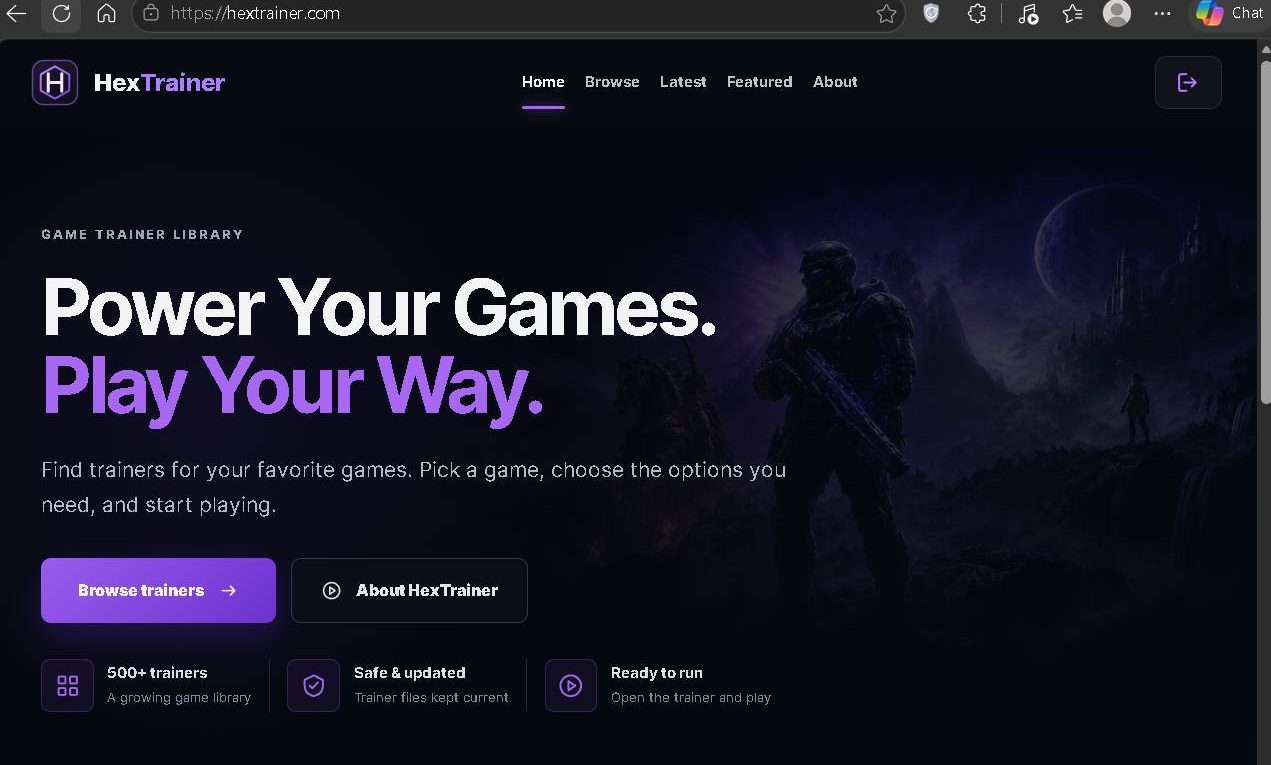
PC gamers looking to customize single-player gameplay, bypass grinding, or test mechanics often search for third-party utilities on HexTrainer, an online platform branding itself as HexTrainer. Built with a modern gaming aesthetic and promoting a library of over 500 game trainers under the slogan “Power Your Games. Play Your Way,” the platform presents itself as an accessible hub for offline PC game modifications.
However, running third-party executables on a PC requires evaluating software authenticity, security reputation, and operational safety. This review provides an objective analysis of HexTrainer, examines how game trainers interact with system memory, highlights key security considerations, and outlines safe alternatives for single-player modding.
What Is a Game Trainer and How Does It Work?
A PC game trainer is a specialized software program created to alter the behavior of a video game while it runs. Rather than modifying core game files on disk, trainers interact with dynamic memory addresses assigned to the game process.
- Memory Hooking and Address Injection: When a game launches, values like player health, in-game currency, stamina, and ammunition are stored at specific RAM memory offsets. Trainers find these addresses and inject modified values to enable features like unlimited health or instant resource generation.
- Process Modification: Trainers utilize Windows API functions (such as
WriteProcessMemoryandOpenProcess) to intercept and adjust the running game thread. - Antivirus Heuristics: Because trainers inject code into active processes, security programs and Windows Defender frequently flag them as “riskware” or “heuristics/hacktool” detections. While benign trainers trigger false positives due to their memory-hooking behavior, this same overlap makes trainer distribution sites a target for malicious software masking.
E-Commerce Protection Checklist
-
1
Break the In-App Browser Funnel
Never check out inside Instagram or TikTok web-views. Copy the link and open a standalone browser to remove referral tracking tokens and inspect the real root domain.
-
2
Run a 60-Second Background Check
Look up the domain age via WHOIS (avoid sites under 6 months old) and reverse-search product imagery on Google Lens to verify whether cheap wholesale duplicates exist.
-
3
Verify Corporate Entity Details
Check the website footer for a registered legal company name, verifiable physical address on Google Maps, and dedicated phone support—not just an anonymous web form.
-
4
Demand Insulated Payment Options
Refuse direct bank deposits, UPI QR codes, crypto, or debit transfers. Use zero-liability credit cards or protected checkout channels like PayPal Goods & Services.
-
1
Stop Waiting for Merchant Email Replies
Do not waste dispute windows negotiating with automated helpdesks or generic tracking updates. Deceptive pop-up storefronts stall purposely to exhaust chargeback timelines.
-
2
Initiate a Bank Chargeback Within 24-48 Hours
Call the phone number printed on the back of your card. Request an immediate dispute categorized under Merchant Fraud, Goods Not Delivered, or Misrepresentation.
-
3
Freeze Billing and Replace Card Credentials
Instruct your bank’s fraud desk to block future merchant authorizations under that descriptor and re-issue a fresh card number to prevent hidden recurring subscription debits.
-
4
Preserve Order & Ad Evidence
Save full-page screenshots of the product page, transaction debit receipts, and tracking communications to upload directly into your card issuer’s dispute portal.
Overview of HexTrainer Platform Architecture
Evaluating the public interface of HexTrainer shows a streamlined digital layout focused on quick discovery and execution.
                [ HexTrainer.com Web Portal ]
     ┌──────────────────────────────────────────────────┐
     │  UI Categories: Browse | Latest | Featured       │
     │  Claimed Library: 500+ Game Trainers             │
     │  Core Promise: "Safe & updated | Ready to run"   │
     └────────────────────────┬─────────────────────────┘
                              │
               (User Selects Game / Download)
                              │
                              ▼
            ┌────────────────────────────────────┐
            │       Binary / Archive Payload     │
            │   • Memory Hook Executables (.exe) │
            │   • Process Injection Modifiers    │
            └─────────────────┬──────────────────┘
                              │
            ┌─────────────────┴──────────────────┐
            ▼                                    ▼
 [ Legitimate Trainer Utility ]        [ Potential Security Risks ]
 • Functional in-memory mods           • Unsigned executable code
 • Offline game value tweaks           • False-positive masking
HexTrainer uses a dark-mode user interface designed to match modern PC gaming clients. The site offers clean top navigation with sections for Browse, Latest, Featured, and About, supported by a responsive search bar to filter supported games.
The landing page highlights three primary selling points:
- 500+ Trainers: An expanding library covering major action, RPG, and adventure titles.
- Safe & Updated: Files marketed as up-to-date with current game patches.
- Ready to Run: Standalone executables designed to open and run alongside your game without complex installation steps.
Suspicious Link or Courier SMS?
Verify URLs, APKs, or parcel alerts against our threat database before clicking.
Technical & Security Analysis: Key Considerations for HexTrainer
1. Domain Registration and Trust Metrics
Domain records indicate that HexTrainer was registered in late August 2026. Because the domain is relatively new, it lacks a long-standing reputation history with cybersecurity monitoring organizations. Independent analysis tools give early-stage utility domains lower baseline trust ratings until long-term community vetting and transparent software signatures are established.
2. Executable Code Signing and Verification
When running downloaded .exe files, the presence of a verified digital signature confirms that the software has not been altered by third parties. Unsigned binaries from newer aggregator platforms require caution. Users should verify whether downloaded trainer packages contain verifiable publisher signatures or come packaged in compressed archives (.zip / .rar) that bypass basic browser screening.
3. Aggregated vs. Original Development
The PC modding ecosystem relies on established developers and reverse-engineers (such as FLiNG, MrAntiFun, and independent Cheat Engine table creators). Aggregator platforms often curate, bundle, or mirror scripts from open developer communities. When using an aggregator, evaluate whether the platform clearly credits the original reverse-engineers or repackages standalone tools behind ad-supported links.
4. Titles Supported in the Catalog
A common quality indicator for trainer repositories is the catalog listing. While trainers for offline single-player games (like RPGs, narrative adventures, and single-player shooters) work reliably, trainers listed for multiplayer-only or server-authoritative titles cannot alter cloud-synchronized player stats. Gamers should stick exclusively to single-player modes to avoid triggering online anti-cheat protections (such as Easy Anti-Cheat, BattlEye, or Ricochet).
Safe Computing Practices: How to Test and Run Game Trainers
If you choose to test software utilities from third-party repositories like HexTrainer, following standard cybersecurity hygiene helps keep your system secure:
- Analyze Files with Multi-Engine Scanners: Before opening any downloaded
.exeor.dllfile, upload the file directly to VirusTotal (virustotal.com). Examine the detailed detection tab to differentiate generic “HackTool” or “Trainer” signatures from trojans, droppers, or credential stealers. - Test Inside an Isolated Environment: Launch unfamiliar binaries inside Windows Sandbox or a dedicated Virtual Machine (VM). Testing tools in an isolated sandbox lets you observe memory-hooking behavior and outbound network requests without risking your primary operating system.
- Monitor Network Activity: Legitimate offline trainers do not need outbound internet connections to alter single-player values in local RAM. Use firewall software to block external network access for trainer executables.
- Keep Core Antivirus Defenses Active: Avoid wholesale disabling of your real-time antivirus software. Instead of turning off system-wide protections, add a targeted folder exclusion only after manually scanning the file.
- Maintain Dedicated Offline Saves: Memory injection can occasionally cause unexpected stability issues or corrupt save files. Always back up your single-player save folders before running trainer hotkeys.
Safe and Established Alternatives for Single-Player Game Modding
Gamers seeking established platforms with verified community track records have several reliable options:
- FLiNG Trainer (flingtrainer.com): One of the longest-running and most widely respected standalone trainer developers in PC gaming, offering clean standalone executables and active update logs.
- WeMod (wemod.com): A unified desktop client featuring digitally signed trainer applications, automatic game-version detection, and an active moderation team.
- Cheat Engine & Fearless Revolution (fearlessrevolution.com): An open-source memory scanning utility that allows players to use community-audited
.CT(Cheat Table) scripts without executing compiled third-party binaries.
Frequently Asked Questions
What is HexTrainer?
HexTrainer (hextrainer.com) is an online catalog that indexes and distributes PC game trainers, offering memory-modifying tools to adjust parameters like health, currency, and ammo in single-player games.
Is HexTrainer safe to use?
Because HexTrainer is a newly registered platform distributing executable files, users should exercise caution. Always scan downloaded .exe files through multi-engine scanners like VirusTotal and run them in an isolated test environment before deploying them on your primary system.
Why do antivirus scanners flag game trainers?
Game trainers modify the active memory of other running applications, using programming calls similar to those flagged by heuristic security monitors. This behavior often triggers “HackTool” or generic riskware warnings even in benign trainers.
Can using HexTrainer result in an account ban?
Using trainers in single-player, offline modes does not violate platform rules on services like Steam or Epic Games. However, attempting to use memory modifiers in online multiplayer games can trigger anti-cheat software and lead to permanent account bans.
Are trainers on HexTrainer free?
HexTrainer presents its trainer library as accessible downloads without upfront retail purchase requirements, though external mirror links or partner ads may be used.
How do I safely remove a game trainer?
Most standalone trainers do not install background system services. To remove a trainer, close the running process, delete the executable file, and restart your PC to clear any temporary RAM modifications.
Every safe click counts. If this post helped, a coffee gesture fuels more scam‑busting investigations.

For more shady sites exposed, check our Shopping Scam Directory — your quick guide to staying safe online.
Help Us Spread Awareness
Please share this article to spread awareness. Follow us on social media for more scam alerts.