Inside the GACOR180 Pipeline: How Dewian.lol Exploits UPI Rails and Weaponized APKs
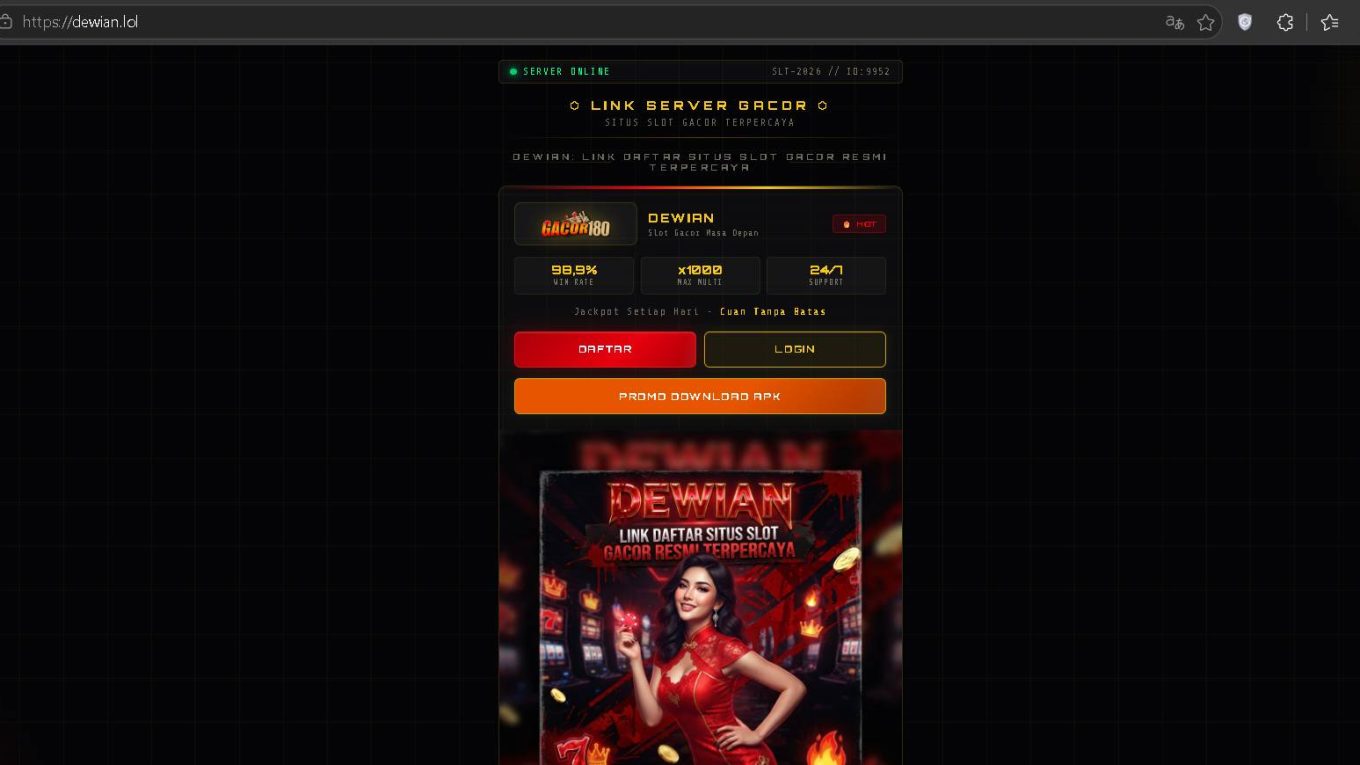
An aggressive digital trap is currently making the rounds across surrogate ad feeds and encrypted broadcast chats, fronting a platform named Dewian.lol. Behind its glowing neon interface sits an unverified frontend funneling traffic straight into the illicit Southeast Asian gambling network known as GACOR180.
Rather than functioning as a genuine entertainment portal, digital forensic analysis shows that Dewian.lol is an unlicensed money extraction mechanism. By pairing fabricated statistical returns with off-market Android package distribution and unregulated peer-to-peer payment routing, the platform routinely catches transacting participants in financial loss, mobile spyware exposure, and multi-state bank account freezes.
Technical Audit Snapshot
| Investigation Vector | Technical Finding / UI Artifact |
| Monitored Endpoint | [https://dewian.lol](https://dewian.lol) |
| Underlying Syndication Identity | GACOR180 (Co-branded on dashboard) |
| Reported Operational Telemetry | Server Online indicator (SLT-2026 // TO: 9953) |
| Advertised Return Multipliers | Win Rate: 98,9% | Max Multiplier: x1000 |
| Interactive Call-to-Actions | DAFTAR (Registration), LOGIN, PROMO DOWNLOAD APK |
| Financial Routing Architecture | Layered UPI Virtual Payment Addresses (VPAs) & rotating mule accounts |
| Mobile Delivery Vector | Direct sideloaded .apk distribution via promotional banner |
| Statutory Licensing Status | Unlicensed; zero recognized gaming accreditation or legal corporate identity |
Anatomy of the Deception: Decentering the GACOR180 Frontend
Visiting Dewian.lol reveals an interface engineered to project technical legitimacy while triggering immediate action.
[Promotional Feed / Surrogate Ads]
               │
               ▼
   [Dewian.lol Landing Node] ──▶ [Terminal Aesthetics: "SERVER ONLINE // TO: 9953"]
               │
      ┌────────┴────────┐
      ▼                 ▼
[UPI P2P Routing]   [PROMO DOWNLOAD APK]
      │                 │
      ▼                 ▼
[Mule Account Trap]  [Background SMS/OTP Interception]
      │
      ▼
[Bank Lien via BNSS §106]
Suspicious Link or Courier SMS?
Verify URLs, APKs, or parcel alerts against our threat database before clicking.
1. Terminal Camouflage and False Operational Health
The landing page opts for a command-center aesthetic rather than a conventional gaming storefront. The dark charcoal grid is anchored by a persistent status header: 🟢 SERVER ONLINE flanked by mock diagnostic metrics like SLT-2026 // TO: 9953. This layout is a deliberate psychological ploy: it borrows the visual language of professional trading stations and secure financial mainframes, disarming visitor skepticism before they register.
2. The Cultural Hook: The Cheongsam Siren & “Cuan Tanpa Batas”
Directly beneath the registration triggers, the site deploys an eye-catching promotional graphic featuring an AI-rendered model in a scarlet silk cheongsam, surrounded by cascading gold coinage, card suits, and blazing red text declaring “DEWIAN: LINK DAFTAR SITUS SLOT GACOR RESMI TERPERCAYA”.
Coupled with the tagline “Jackpot Setiap Hari – Cuan Tanpa Batas” (Daily Jackpots – Limitless Wealth), the design exploits cognitive reward anticipation. Promising uninhibited profit while claiming official status (“Resmi Terpercaya”) creates a false impression of corporate security that completely contradicts the site’s anonymous offshore setup.
3. Exploiting the .lol Domain Shield
Why does a Southeast Asian gambling cluster deploy a .lol domain? The choice is strategic:
- Bypassing Enterprise Threat Filters: Mainstream firewalls, school proxies, and workplace safety filters often classify
.lolunder novelty or entertainment rather than financial risk or gambling, allowing traffic to flow unimpeded. - Low-Cost Horizontal Scaling: Because these disposable domain extensions cost only a fraction of traditional gTLDs, syndicate operators purchase them in bulk. If regulatory watchdogs block
Dewian.lol, the entire template is re-routed to a sister domain within minutes without disrupting backend deposit harvesting.
The Cross-Border Jurisdiction Arbitrage
A glaring contradiction on Dewian.lol is its linguistic targeting. The entire UI is rendered in Indonesian slot vernacular—featuring colloquial terms like Gacor, Cuan, and Daftar. Yet the operational funnel is aggressively pushed toward digital users in India through surrogate social campaigns, pirated sports broadcasts, and Telegram “earning” tipster networks.
This cross-border disconnect serves a critical tactical purpose for cyber syndicates:
- Domestic UPI Ingestion: Indian depositors send funds locally using familiar, friction-free UPI QR codes and payment handles.
- Offshore Laundering Insulation: The criminal operators pulling the strings sit thousands of miles away in Southeast Asian jurisdictions, safely out of reach of domestic police inquiries.
- Dead-End Paper Trails: When domestic victims realize their balances cannot be withdrawn, local authorities encounter a jurisdictional wall, unable to reach the offshore servers hosting the actual software.
Technical Hazards: Where the Trap Snaps Shut
Mathematical Impossibility: The 98.9% Win-Rate Mirage
The user interface prominently advertises a 98,9% WIN RATE alongside an astronomical x1000 MAX MULTI.
In authentic gaming mathematics, Return-to-Player (RTP) figures are theoretical calculations modeled over hundreds of millions of automated spins—they never represent a static, single-user win rate. Dewian.lol carries no auditing credentials from verified third-party laboratories such as eCOGRA, iTech Labs, or BMM Testlabs. Instead, the backend API allows site administrators to manipulate payout outcomes dynamically: early spins are artificially rigged to produce minor gains, enticing victims into larger deposits before algorithms enforce guaranteed, unrecoverable losses.
The Trojan in Plain Sight: The PROMO DOWNLOAD APK Hook
Unlike secure platforms that operate exclusively inside hardened browser environments, Dewian.lol features an elongated orange banner explicitly urging users: PROMO DOWNLOAD APK.
Enticing visitors with bonus play money to install an untrusted package file bypasses the security perimeter of the Google Play Store. Once sideloaded, these malicious applications typically demand invasive device privileges:
android.permission.RECEIVE_SMSandREAD_SMSandroid.permission.BIND_ACCESSIBILITY_SERVICE
With accessibility services granted, the application operates with full visibility over the screen. It can silently intercept incoming bank SMS alerts, harvest one-time passwords (OTPs) in the background, and relay authentication credentials to remote command servers—clearing the path for unauthorized fund transfers without alerting the phone’s owner.
The Asymmetric Cashout Wall
Depositing capital into Dewian.lol is immediate, but attempting a withdrawal triggers an extortion loop. Victims requesting their money are told their payouts are held pending an “unfreeze tariff,” a “TDS compliance deposit,” or an “anti-fraud clearance fee.” Every supplementary payment sent to unlock the balance is stolen, and users who press support for answers are locked out permanently.
Financial Contagion: The Mechanics of a Mule Account Freeze
The most damaging consequence of transacting on Dewian.lol is not just losing deposited capital—it is the legal fallout that frequently hits the victim’s personal bank account.
[Victim Deposits Funds on Dewian.lol via UPI]
                    │
                    ▼
      [Layer 1 / Layer 2 Mule Account]
                    │
                    ▼
[Syndicate Moves Funds Across Banking Rail]
                    │
                    ▼
[Cybercrime Police Registers FIR from Another Victim]
                    │
                    ▼
[Statutory Debit Freeze Imposed on ALL Interacting Accounts]
       (Section 106 BNSS / Section 102 CrPC)
Because the platform does not possess legitimate merchant acquiring facilities, deposits flow directly into unregulated mule accounts—bank accounts rented from third parties or acquired via synthetic identities.
When another victim defrauded by the same syndicate files a complaint, cybercrime units map every transaction linked to that central mule node. Under Section 106 of the Bharatiya Nagarik Suraksha Sanhita (BNSS) (formerly Section 102 of the CrPC), investigating authorities have the statutory power to issue blanket debit freeze orders across the entire financial chain. As a result, users who deposited money into Dewian.lol find their primary savings accounts hit with sudden liens, locking personal funds indefinitely while police trace the money-laundering web.
Digital First Aid: Remediation & Quarantine Protocols
If you have already interacted with Dewian.lol, swift action is essential to contain financial and digital damage:
Halting the Financial Bleed
- Trigger the Golden-Hour Alert (1930): If you recently transferred money via UPI, immediately call the National Cybercrime Helpline at 1930 or log on to cybercrime.gov.in. Rapid intervention within the initial 2 to 4 hours allows authorities to flag the recipient handle and place holds before funds are cascaded down the mule pipeline.
- Tackling Bank Debit Liens: If your account has been frozen due to syndicate activity, request the formal police requisition order and FIR number from your bank branch. Prepare a factual representation demonstrating that you were an unwitting target rather than a willing participant in money laundering, supporting your case with unedited payment records and your official 1930 complaint slip.
- Flagging Social Vectors via Chakshu: Forward all suspicious SMS links, WhatsApp numbers, or Telegram channels that directed you to Dewian.lol to the Department of Telecommunications (DoT) via the Chakshu portal on Sanchar Saathi.
Eradicating Malicious Mobile Payloads
If you sideloaded an installer from the site’s PROMO DOWNLOAD APK banner:
- Restart in Safe Mode: Boot your device into Safe Mode to suppress third-party services and background scripts.
- Revoke Administrative Authority: Navigate to Settings > Security > Device Admin Apps and disable permissions for any unfamiliar app or package referencing “DEWIAN” or “GACOR”.
- Purge the Package: Locate the recently downloaded application in Settings > Apps, force stop the process, wipe cache and storage, and uninstall it entirely.
- Credential Lockdown: Using a clean secondary device, change all primary banking passwords, regenerate your UPI PINs, and terminate active web sessions across your primary email accounts.
Fraud Defense Resources
🛡️ Threat Protection & Recovery Toolbox
- Mobile Endpoint Protection: Neutralize hidden Android Trojans, accessibility keyloggers, and SMS interceptors using verified mobile security tools like Bitdefender Mobile Security or Malwarebytes Premium.
- Identity & Credit Safeguard: Protect personal records (PAN, Aadhaar, national identity data) against identity theft and unauthorized borrowing via active credit monitoring.
- Secure Anti-Phishing Shield: Keep device traffic isolated from rogue redirect engines, malicious DNS poisoning, and ephemeral scam domains using a verified zero-log VPN.
FAQ: Understanding the Dewian.lol Threat
Is Dewian.lol a scam?
Yes, Dewian.lol is an unlicensed fraudulent portal. It uses fabricated performance statistics (including a false 98.9% win rate) to pull deposits into an unregulable offshore funnel that blocks payouts.
Is Dewian.lol legit?
No, Dewian.lol is not legit. It operates without statutory incorporation, lacks recognized gaming commission credentials, and hides its domain infrastructure behind disposable privacy shields.
What is the connection between Dewian.lol and Gacor180?
The landing page prominently features the GACOR180 brand badge. Dewian.lol acts merely as an entry mirror routing traffic into the broader GACOR180 syndicate network.
The promotional banner prompts you to sideload an unverified .apk file that bypasses app store safety checks. These files frequently harbor spyware capable of intercepting incoming SMS OTPs and harvesting personal banking credentials.
Why was my bank account frozen after depositing funds on Dewian.lol?
Deposits are sent to private mule accounts rather than official merchant processors. When cybercrime units investigate fraud linked to these mules, all interconnected accounts are frozen under Section 106 BNSS / Section 102 CrPC.
Can I withdraw my winnings from Dewian.lol?
No. Winnings displayed in your dashboard are simulated figures. Payout requests are systematically blocked, and operators demand additional “clearance fees” before terminating communication entirely.
What do the numbers “98,9%” and “x1000” on the website mean?
They are fabricated promotional claims designed to make the platform seem lucrative and lure users into making real-money deposits.
Report the transaction immediately to 1930 and file a complaint on cybercrime.gov.in. Provide the exact UTR reference number so authorities can place an inter-bank freeze on the recipient account.
Every safe click counts. If this post helped, a coffee gesture fuels more scam‑busting investigations.

Related Forensic Teardown • Master Guide
How Domain Churn Scams Keep Illegal Betting Rings Alive →Help Us Spread Awareness
Please share this article to spread awareness. Follow us on social media for more scam alerts.