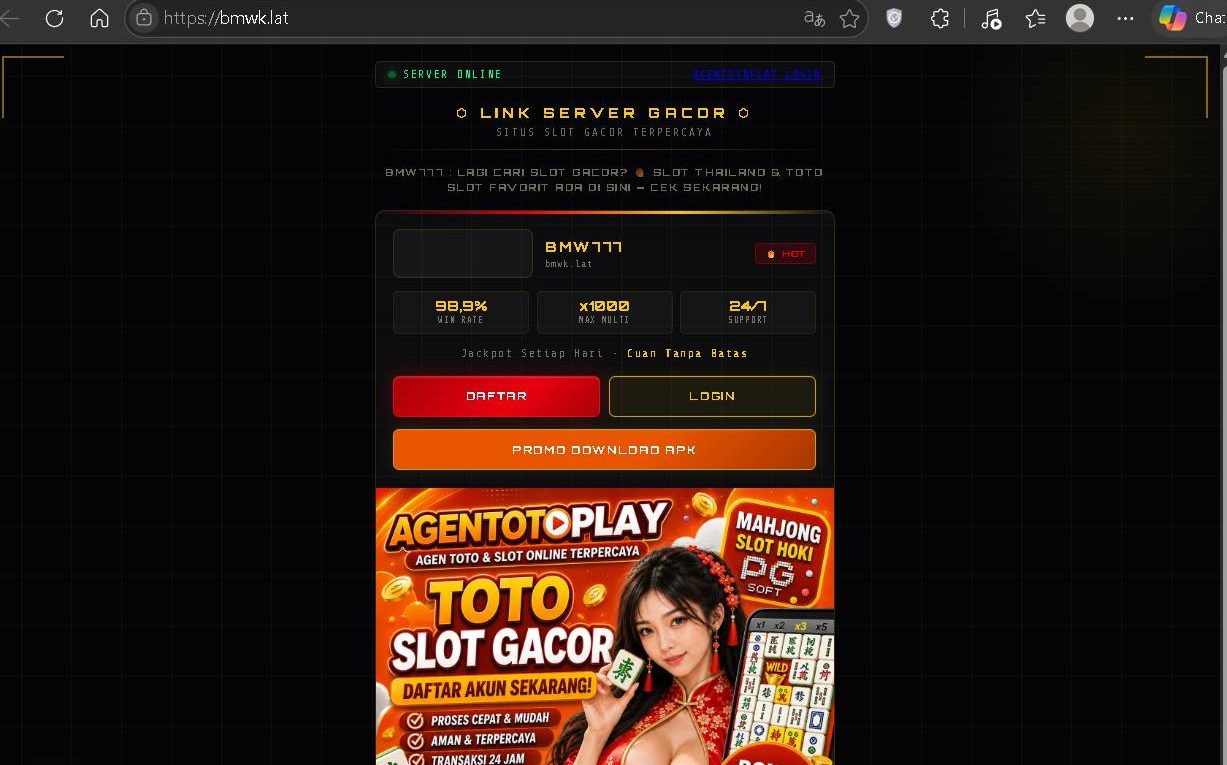
The Phantom Portal: Exposing Bmwk.lat and the Mechanics of Malicious Redirection & Mirror Churn
If you recently landed on Bmwk.lat, chances are you didn’t type that address into your address bar intentionally. Finding yourself pushed toward Bmwk.lat is usually the direct byproduct of malicious redirection & mirror churn, an evasive digital syndication tactic deployed by underground casino and slot operators.
When you navigate the web, especially through video streaming forums, file download platforms, or unsolicited promotional blasts, automated scripts frequently hijack your browser session. In this investigative breakdown, we peel back the hood on how disposable fronts operate, dissect what makes this domain dangerous, and arm you with actionable cyber safety measures to secure your digital footprint and financial accounts.
What Is Malicious Redirection & Mirror Churn? Understanding the Evasion Engine
To understand why platforms like Bmwk.lat crop up on consumer radars, we must examine two intertwined techniques weaponized across high-risk affiliate webs: malicious redirection and mirror churn.
Suspicious Link or Courier SMS?
Verify URLs or APKs before clicking.
1. Malicious Redirection
Malicious redirection occurs when malicious JavaScript, unauthorized DNS shifts, or cloaked ad scripts force your browser to leave your requested destination and load an unvetted third-party website.
Unlike traditional advertising—where clicking a banner takes you to a clearly defined product page—malicious redirects trigger silently. They often activate via hidden click-jack overlays, background pop-unders, or compromised ad exchange networks. The core purpose is simple: bypass deliberate choice and force high volumes of unconsenting user traffic into deceptive sales funnels, high-risk financial schemes, or unverified betting rings.
2. Mirror Churn
Mirror churn is the continuous cycle of registering, deploying, abandoning, and burning disposable domain names.
When a gambling portal or high-risk storefront operates outside legal regulatory frameworks, its web address quickly ends up flagged by web security firewalls, Google Safe Browsing, search engine spam filters, and regional telecommunication ISP blocks. To outrun these enforcement mechanisms, operators establish an automated deployment line:
[Master Content Database / Unlicensed Backend]
           │
           ├──► [Domain A: bmwk.lat] ────► Blacklisted / ISP Blocked
           │
           ├──► [Domain B: bmwj.lat] ────► Active Mirror (Temporary)
           │
           └──► [Domain C: bmwx.lat] ────► Warm Standby Node
As soon as domain reputation monitors flag Bmwk.lat, the operators cut DNS traffic to that node and route incoming visitor streams to a fresh, clean clone within minutes. To ordinary search engines and security scanners, each URL looks like a new, independent website; to the operator, it is merely a disposable straw feeding traffic into the same illicit core.
Player Safety Blueprint: Prevention & Solutions
Protect assets before interacting with unverified mirrors, or follow mitigation steps if data was shared.
Never pay secondary “clearance taxes” or “unlock fees” to release trapped funds.
Uninstall suspicious packages, reboot into Safe Mode, and run an updated antivirus scan.
Reset passwords on linked emails/wallets immediately and enable authenticator-app 2FA.
Contact your bank’s fraud desk to dispute transactions under merchant fraud.
Block unsolicited contacts and disregard third-party “fund recovery” hackers requesting fees.
Case Study: Deconstructing Bmwk.lat
Applying these concepts to Bmwk.lat illustrates why understanding these architectural patterns is critical for consumer defense.
How Does Bmwk.lat Work?
The operational life cycle of Bmwk.lat depends on stealthy upstream funnels. Most users encounter the domain via intermediate URL shorteners or aggressive ad-tech syndicates running rogue real-time bidding (RTB) scripts. Once an unsuspecting user taps anywhere on a compromised publisher page, an unseen script opens Bmwk.lat in a new tab.
Under the hood, the site functions as a lightweight front-end proxy. The server hosting Bmwk.lat does not run independent software; instead, it fetches assets and routing parameters from an offshore master server commonly tied to uncertified Southeast Asian white-label gambling networks.
User Click ──► Script Injection ──► Bmwk.lat (Proxy Node) ──► Offshore Unlicensed Funnel
If an internet service provider in a target territory blocks the IP address tied to Bmwk.lat, the affiliate management back-office simply reassigns the DNS pointers, leaving registered users stranded while the syndication engine continues unimpeded under a different alphanumeric string.
What Is Bmwk.lat Claiming and Offering?
When you arrive on the landing pages linked with Bmwk.lat, the presentation is calibrated to induce immediate action through bold promises and fabricated urgency.
- High Return-to-Player (RTP) Guarantees: The landing page routinely displays flashing widgets promising Slot Gacor games, claimed “98.5%+ win probabilities,” and “insider algorithms” supposedly calibrated for guaranteed payouts.
- Instant Deposit Incentives: New visitors are bombarded with banners advertising 100% to 200% first-time deposit matches, zero-fee wire funding, and cryptocurrency reloads designed to extract upfront funds immediately.
- Fictitious Partnerships: The platform frequently clones the graphical assets of legitimate iGaming content providers—such as Pragmatic Play, PG Soft, or Microgaming—to project a false aura of legitimacy and regulatory adherence.
- Frictionless Onboarding: Registration prompts intentionally bypass standard Know Your Customer (KYC) identity compliance, asking merely for an unverified phone number, e-wallet tag, or basic bank account details to minimize registration hesitation.
5 Critical Red Flags on Bmwk.lat
Evaluating the technical indicators of Bmwk.lat reveals classic warnings that distinguish exploitative clone networks from compliant digital platforms.
1. Total Absence of Verifiable Regulatory Licensing
Legitimate financial platforms and regulated gaming portals prominently display searchable license certificates issued by recognized supervisory bodies—such as the Malta Gaming Authority (MGA), the UK Gambling Commission (UKGC), or the Curaçao Gaming Control Board. Bmwk.lat displays no verifiable licensing numbers, corporate entity registration records, or physical office disclosures.
2. Disposable Top-Level Domain Architecture
The choice of the .lat extension paired with a four-letter, randomized alphanumeric prefix (bmwk) matches the footprint of high-velocity domain generation algorithms. Legitimate companies commit to identifiable, trademarked domain names with long-term infrastructure investments; disposable churn networks prefer cheap, high-churn registries that carry negligible abandonment costs when blacklisted.
3. Asymmetric Transaction Friction
The interface makes depositing funds instantaneous via local peer-to-peer bank transfers, QR payment links, and unhosted crypto wallets. Conversely, withdrawal terms are buried beneath ambiguous wagering requirements, hidden rollover multipliers, and arbitrary administrative holds that ensure your deposited funds cannot easily be retrieved.
4. Zero Data Protection and Identity Safeguards
The registration forms on Bmwk.lat lack independent verification seals and enforceable privacy policies. When you enter personal banking details, phone numbers, or credentials on an unvetted proxy portal, your sensitive data is stored on unencrypted remote databases that are routinely sold among identity fraud syndicates and phishing rings.
5. Deployment of Pirated, Non-Audited Software
Reputable platforms integrate software verified by independent testing laboratories like eCOGRA, BMM Testlabs, or iTech Labs to ensure genuine random number generation (RNG). Clone portals like Bmwk.lat regularly deploy unauthorized copies of game code hosted on unverified private servers, allowing backend administrators to manipulate payout parameters at will.
Consumer Protection Checklist: How to Protect Your System and Accounts
If you have inadvertently encountered or interacted with Bmwk.lat, take proactive countermeasures immediately:
- Flush Browser Cache and Storage: Clear your browser’s complete cookie cache and site data history to eliminate persistent tracking cookies and cached script triggers.
- Inspect Installed Extensions: Examine your browser’s extension panel for unknown add-ons or recently modified scripts that might be executing hidden background redirects.
- Update DNS & Enable Protective Filtering: Switch your local device or network router to a privacy-centric DNS provider equipped with automatic threat blocking (such as Cloudflare
1.1.1.2or Quad99.9.9.9). - Freeze Associated Financial Instruments: If you submitted banking details or prepaid wallet numbers, notify your financial institution immediately to place a temporary fraud watch or card freeze on your account.
Frequently Asked Questions (FAQ)
1. Is Bmwk.lat a scam?
Yes. Bmwk.lat exhibits the established hallmarks of an unlicensed, high-risk clone network. It utilizes unauthorized proxy funnels, operates without demonstrable regulatory credentials, and offers no verifiable legal protections or dispute escalation paths for consumer funds.
2. Is Bmwk.lat legit?
No. Bmwk.lat is not a legitimate or legally certified gaming portal. It operates on an unverified, disposable .lat domain designed to cycle rapidly as a mirror node, intentionally evading regulatory oversight and telecommunications security restrictions.
3. How does malicious redirection happen when browsing online?
Malicious redirection typically triggers through exploited third-party advertisement networks, clickjack overlays placed over media players, or compromised website code that invisibly routes your web request through intermediate traffic distribution systems.
4. What should I do if a website automatically redirects me to Bmwk.lat?
Close the browser tab immediately without clicking on any buttons, downloading files, or entering text. Clear your browser’s cached storage data and run a quick security scan on your device using reputable malware removal tools.
5. Why do operators rely on mirror churn rather than maintaining one permanent domain?
Operators rely on mirror churn because rogue or non-compliant portals are regularly blocked by internet service providers, blacklisted by cybersecurity software, and removed from search indexes. Cycling through cloned domains allows them to preserve incoming traffic streams uninterrupted.
6. Can I safely recover money deposited into Bmwk.lat?
Recovering funds deposited into unvetted mirror portals is exceptionally difficult. Because transactions are typically funneled through private e-wallets, peer-to-peer transfers, or non-reversible cryptocurrency addresses, traditional chargeback mechanisms rarely function without direct intervention from your bank’s fraud unit.
7. How can I identify if a web platform is participating in mirror churn tactics?
Warning signs include sudden changes to the domain name while the underlying layout remains identical, randomized domain names consisting of disjointed letters and numbers, rapid shifting across unusual TLDs, and the absence of verifiable corporate contact information.
8. Does visiting Bmwk.lat automatically install malware on my device?
Simply landing on the page and closing it immediately carries a lower risk on fully patched, modern browsers. However, remaining on the site increases exposure to drive-by download attempts, misleading browser notification requests, and malicious payload distribution disguised as software updates.
Every safe click counts. If this post helped, a coffee gesture fuels more scam‑busting investigations.

Help Us Spread Awareness
Please share this article to spread awareness. Follow us on social media for more scam alerts.