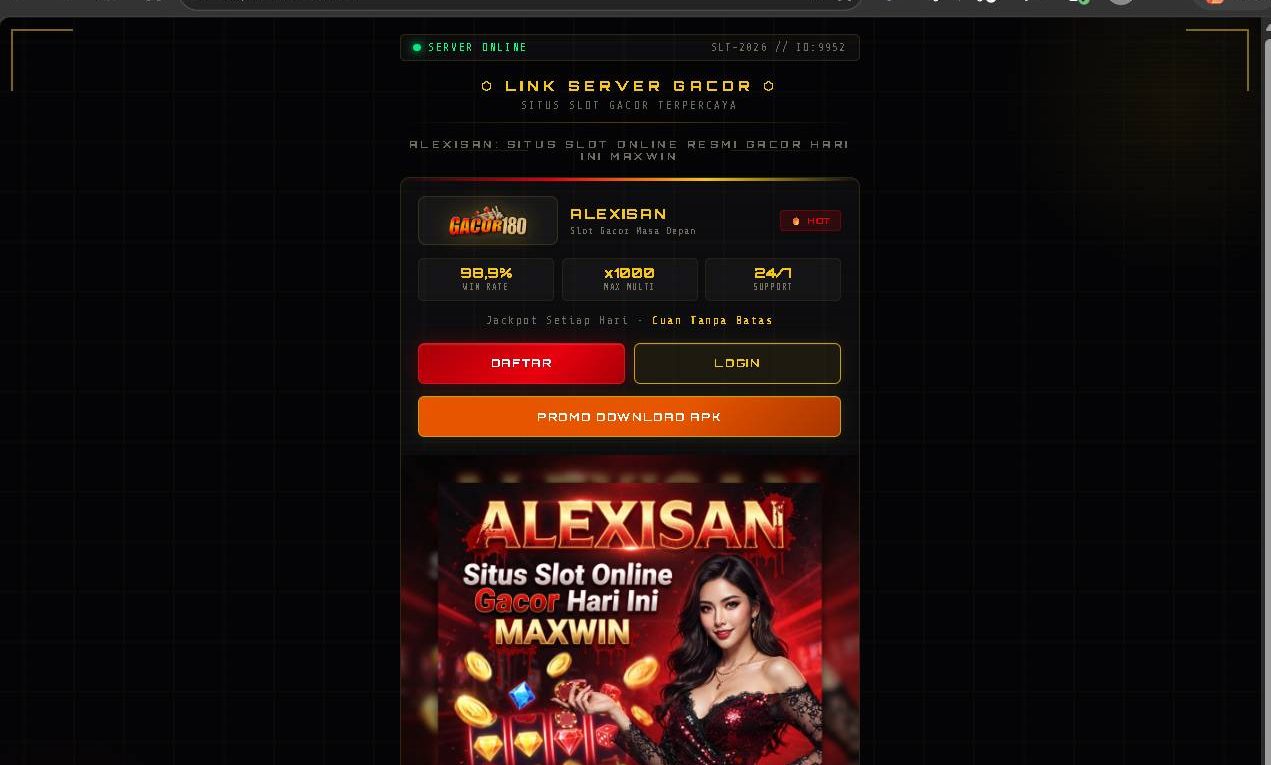
Alexisan.lat Investigation: Unmasking the Risks of This Cloned Judi Online Mirror
Landing on Alexisan.lat redirects users straight into an unregulated, black-market “Judi Online” (Judol) scam masked beneath the veneer of an advanced iGaming command deck. Operating under the syndicate framework GACOR180 and sporting the label ALEXISAN, the website pairs high-contrast sci-fi graphics with promises of effortless jackpots to draw in casual bettors.
The domain name itself relies on familiar branding association, invoking the name of well-known nightlife and leisure brands in Southeast Asia to establish instant psychological familiarity. In reality, Alexisan.lat is not an authorized, fair-play casino operating under legitimate legal oversight.
It functions as a disposable collection node within a syndicated cybercrime operation designed to siphon player deposits, capture sensitive banking details, and deploy unverified mobile software. This investigative report uncovers how Alexisan.lat works, breaks down its mobile malware risks, and details how you can safeguard your identity and finances.
What Does Alexisan.lat Claim and Offer?
The landing portal mimics a digital terminal packed with high-converting marketing hooks:
- Fabricated Win Statistics: The interface prominently advertises a fixed “98,9% Win Rate” alongside a “x1000 Max Multi”, falsely suggesting that negative variance does not exist.
- Guarantees of Endless Income: Front-page copy promotes slogans like “Cuan Tanpa Batas” (boundless profits) and “Situs Slot Online Resmi Gacor Hari Ini Maxwin”, presenting high-volatility games of chance as dependable revenue streams.
- Aggregated Betting Products: The platform markets a broad selection of unverified digital slot titles, live-streamed casino dealer rooms, sportsbooks, and regional lotteries (togel).
- Aggressive Mobile Sideloading: A glowing “PROMO DOWNLOAD APK” button urges visitors to bypass verified application marketplaces and install proprietary mobile packages directly onto their smartphones.
Technical Flow: How the Syndicate Funnel Operates
Alexisan.lat does not run an independent casino backed by audited gaming infrastructure. The embedded server tag SLT-2026 // ID:9952 confirms that it is simply a cloned front-end mirror (link server gacor or link alternatif) sharing identical backend hosting with numerous disposable portals.
[User Visits Alexisan.lat]
           │
           ▼
[Urged to Sideload Rogue APK / Register Personal & Bank Details]
           │
           ▼
[Transfers Real Capital via P2P Mule Account Rails]
           │
           ▼
[Plays Scripted, Unaudited Slot Software]
           │
           ▼
[Attempts Cash-Out] ──► [System Lockout / Advance-Fee Demands]
When visitors tap the DAFTAR (Register) button, the platform captures their active mobile phone number, legal name, and primary checking account or digital wallet identifiers. Deposits bypass accredited commercial clearinghouses; instead, players are instructed to transfer funds peer-to-peer into retail bank accounts held by third-party “money mules.”
The underlying games run on uncertified software scripts calibrated to trigger small, early payouts to hook the player. However, the moment a user attempts to cash out a significant balance, the system clamps shut—enforcing impossible rollover requirements, citing fabricated account verification errors, or terminating user access without explanation.
Deep Dive: The “Slot Gacor” Trap and Mobile Malware (APK) Risks
The greatest hazard associated with Alexisan.lat stems from its two-pronged attack model: pairing psychological gaming deception with raw mobile security compromise.
The “Slot Gacor” Psychological Trap
The platform leans heavily on the term “Slot Gacor”, regional gambling slang describing a slot machine that is supposedly “hot” or running loose. Operators exploit cognitive biases by claiming that their specific servers are calibrated to yield easy jackpots (mudah maxwin). In truth, genuine casino mathematics rely on audited pseudo-random number generation. Because Alexisan.lat runs uncertified code, operators have complete backend control to alter payout frequencies and throttle winning lines down to zero whenever larger bets are placed.
Direct APK Sideloading and Mobile Malware Hazards
The prominent “PROMO DOWNLOAD APK” button introduces severe endpoint vulnerabilities to mobile devices:
- Circumventing App Store Sandboxing: Official app marketplaces run rigorous security screenings to catch malicious payloads before release. Sideloading an untrusted
.apkfrom a web browser removes your operating system’s built-in sandbox defenses. - Interception of Two-Factor Authentication (2FA): Illicit casino APKs frequently request invasive permissions, such as
RECEIVE_SMSandREAD_SMS. This allows hidden background services to silently intercept one-time passwords (OTPs) sent by commercial banks, digital payment apps, and personal email accounts. - Accessibility Services Exploitation: Sophisticated Android banking trojans abuse Accessibility Services to capture screen keystrokes, record login credentials, and execute unauthorized money transfers inside legitimate banking apps without the user’s consent.
- Contact Scraping for Extortion Networks: Sideloaded applications regularly vacuum device contact books, call histories, and location data. This harvested data is frequently sold to illegal lending networks (pinjol ilegal) and high-pressure telemarketing scam rings.
5 Critical Red Flags on Alexisan.lat
+------------------------------------------------------------------------------------------+
|                                ALEXISAN.LAT RED FLAG AUDIT                               |
+------------------------------------+-----------------------------------------------------+
| Risk Vector                        | Diagnostic Evidence                                 |
+------------------------------------+-----------------------------------------------------+
| 1. Sideloaded APK Vector           | Pushes unverified Android packages bypassing stores |
| 2. Statistically Impossible Math   | Promotes fixed 98.9% win rates to deceive users     |
| 3. Ephemeral .lat Architecture     | Disposable TLD cycled to evade regulatory bans      |
| 4. Peer-to-Peer Mule Payments      | Directs funds to personal accounts, barring disputes|
| 5. Complete Lack of Licensing      | Operates without statutory gaming oversight         |
+------------------------------------+-----------------------------------------------------+
1. High-Pressure Prompts to Sideload Unknown Applications
Legitimate, licensed iGaming providers deploy applications through official app stores that enforce strict developer policies and anti-malware standards. Urging users to install an unsigned .apk directly from a mobile browser is a critical warning sign often associated with spyware and banking trojans.
2. Statistically Deceptive Payout Figures
Advertising an overarching 98,9% Win Rate is mathematically deceptive. Certified casino software operates using theoretical Return to Player (RTP) figures verified over millions of continuous spins; it never delivers flat, guaranteed win percentages. Presenting these metrics is a deliberate manipulation tactic aimed at mathematically inexperienced players.
3. Disposable Domain Architecture (.lat)
The site’s deployment on a cheap .lat top-level domain indicates temporary, disposable infrastructure. Telecommunications authorities and cybersecurity threat filters routinely blacklist unlawful gambling websites. Operating on low-cost extensions allows syndicates to abandon flagged URLs and redirect traffic to fresh clone sites overnight.
4. Direct Transfers via Money Mule Accounts
Legitimate e-commerce and licensed gaming hubs use authorized payment processors adhering to strict Anti-Money Laundering (AML) standards and consumer dispute protections. Alexisan.lat bypasses commercial clearinghouses, forcing users to send money directly to individual bank accounts or unmonitored digital wallets. These belong to recruited money mules, meaning transfers cannot be reversed once processed.
5. Absence of Statutory Licensing and Auditing
Alexisan.lat carries zero verifiable licensing credentials from recognized supervisory authorities such as the Malta Gaming Authority (MGA), the UK Gambling Commission (UKGC), or Curacao eGaming. Furthermore, the portal displays no audit seals from independent software testing laboratories like eCOGRA or iTech Labs, leaving the operator free to adjust game parameters without accountability.
Actionable Steps to Safeguard Your Assets and Personal Data
If you have visited Alexisan.lat, submitted sensitive credentials, or downloaded files from the portal, take these decisive security measures immediately:
- Uninstall Any Sideloaded Apps Immediately: If you clicked “PROMO DOWNLOAD APK” and installed the software, go to your mobile settings, clear the application’s cache and data, and uninstall it. Run a thorough system scan using a trusted mobile antivirus tool (such as Bitdefender, Malwarebytes, or Sophos).
- Revoke Dangerous Device Permissions: Open your device settings under Special App Access, Accessibility, and Display Over Other Apps. Ensure that no unrecognized background application holds permissions to monitor screen content or capture inputs.
- Alert Your Bank’s Fraud Prevention Division: If you provided your checking account details, debit card numbers, or digital wallet credentials, notify your financial institution immediately. Request a stop-payment on unauthorized debits, cancel compromised cards, and update your online banking passwords.
- Place Fraud Alerts on Your Credit Profile: Registering on unverified slot networks exposes your identity to syndicates that package and sell lead lists. Initiating a security freeze or placing a fraud alert with major credit bureaus (Equifax, Experian, TransUnion) blocks bad actors from opening unauthorized credit lines in your name.
- Harden Digital Account Security: If you reused the password you registered on Alexisan.lat across other personal services (such as your primary email or banking portal), update those credentials immediately and enable authenticator-based two-factor authentication (2FA).
- Report the Malicious Domain: File formal incident reports with your local internet safety agency or national cybercrime clearinghouse (such as the FBI’s IC3, Action Fraud, or regional content filtering portals like Aduan Konten). These reports help security vendors flag and take down rogue domains across global DNS networks.
Frequently Asked Questions (FAQ)
1. Is Alexisan.lat a scam?
Yes. Alexisan.lat displays all the hallmarks of an unregulated, black-market gambling trap. It operates on disposable domain infrastructure, promotes mathematically impossible win rates, lacks statutory licensing, and pushes unverified APK downloads that expose mobile devices to security risks.
2. Is Alexisan.lat legit?
No. Alexisan.lat is not a legitimate online casino or authorized betting service. It carries no valid licenses from recognized gaming authorities, conceals its corporate ownership, and uses uncertified software that fails standard fair-play requirements.
3. What makes the APK download on Alexisan.lat dangerous?
Downloading an application package directly from an unverified website bypasses mobile operating system security protections. Sideloaded casino APKs frequently request invasive permissions that allow malicious actors to monitor device usage, steal one-time authentication codes (OTPs), and intercept online banking credentials.
4. What does “Slot Gacor” mean on Alexisan.lat?
The phrase “Slot Gacor” is a regional marketing buzzword used to suggest that a digital slot machine is running hot or paying out frequently. Unlicensed operators use this phrase to lure users into depositing real money on games that are actually rigged to favor the house.
5. Why does the website operate under a .lat domain extension?
Illicit gambling syndicates purchase cheap, non-traditional extensions like .lat in bulk because telecommunication regulators and cybersecurity firewalls routinely ban their websites. Using disposable domains enables operators to launch new mirror portals as soon as older links are blocked.
6. Can I recover money sent to Alexisan.lat?
Direct fund recovery from unlicensed platforms is extremely difficult because transfers flow through money mule bank accounts and unmonitored digital wallets. While you should report the unauthorized transaction to your bank’s fraud unit immediately, be cautious of fraudulent online “asset recovery” services that demand upfront fees.
7. What identity theft risks are associated with registering on Alexisan.lat?
Submitting your active phone number, full legal name, and banking details exposes your personal information to unverified actors. These databases are frequently traded across black-market messaging networks, leaving you vulnerable to targeted phishing schemes, spam calls, and unauthorized credit applications.
8. How can I verify whether an online casino is safe and licensed?
A legitimate online casino operates under a clear legal framework with verifiable licenses from established regulators (such as the MGA or UKGC). It will clearly display interactive license registers, process payments through established merchant processors, and offer games independently certified for fair play by testing labs like eCOGRA or iTech Labs.
Every safe click counts. If this post helped, a coffee gesture fuels more scam‑busting investigations.

Help Us Spread Awareness
Please share this article to spread awareness. Follow us on social media for more scam alerts.