Inside Linkdl.fit: How the ‘HOKI 108’ Network Deploys Disposable Mirrors, Fake 98.9% RTP, and Sideloaded APKs
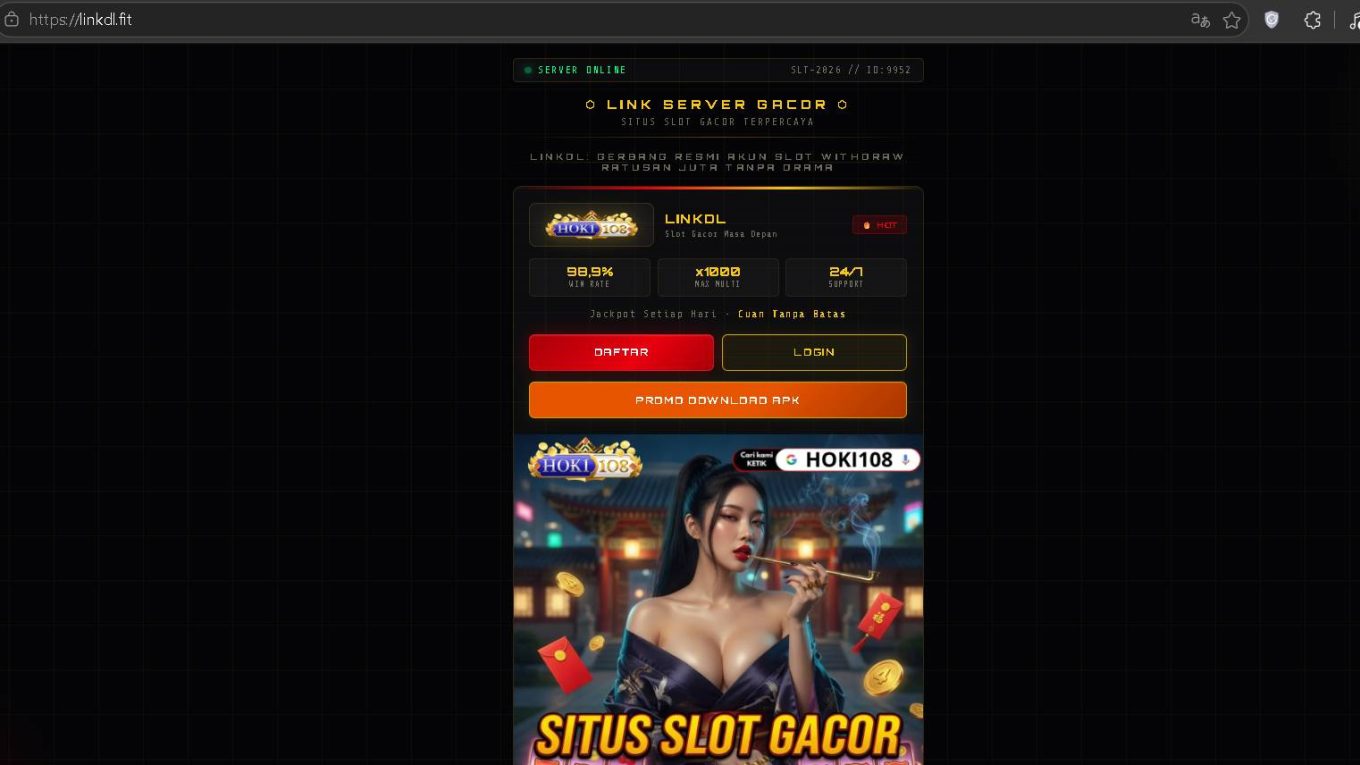
A forensic review of [https://linkdl.fit](https://linkdl.fit) reveals an illicit, unlicensed gambling proxy built to funnel retail users into the offshore “HOKI 108” syndicate. The landing page strips away traditional casino architecture in favor of a disposable, mobile-optimized redirect shell. Rather than hosting verifiable games on-site, the portal acts as a dual-purpose trap: extracting untraceable payments via third-party mule chains and distributing unvetted Android application packages (.apk) directly to users’ phones.
The site operates outside regulated gambling frameworks, using false mathematical guarantees and layered proxy routing to evade detection while putting visitors at risk of immediate financial loss, mobile spyware exposure, and downstream cyber-cell bank account freezes.
The Camouflage Layer: Deconstructing the Interface
[ Visitor Hits linkdl.fit ]
         │
         ├── Psychological Anchor: High-RTP Claim (98.9%) + x1000 Multiplier
         │
         ├── Visual Pacifier: "SERVER ONLINE" Status + Live Server Timestamp
         │
         └── Conversion Funnel:
                 ├── [DAFTAR / LOGIN] ──────► Layered P2P Mule Payment Trap
                 └── [PROMO DOWNLOAD APK] ──► Off-Store Banking Trojan / Spyware
The visual presentation of Linkdl.fit is designed to exploit cognitive vulnerabilities through aggressive visual and cultural anchors:
- The Naming Engine: The domain marries “Link” and “dl” (shorthand for direct download) with the
.fitTLD. This specific naming structure avoids obvious keywords like.casinoor.bet, sliding under the radar of automated workplace network filters, parental blocks, and default telecom blacklist scrapers. - The “Gacor” Psychological Hook: Emblazoned with Indonesian phrases such as “SITUS SLOT GACOR TERPERCAYA” (trusted high-frequency slot site) and “WITHDRAW RATUSAN JUTA TANPA DRAMA” (withdraw hundreds of millions without drama), the UI actively addresses the core anxiety of online gamblers: getting their money back out. By promising zero-friction payouts right beside claims of a “98.9% RTP” and “x1000 Max Multiplier,” the platform manufactures a false sense of high-odds legitimacy.
- Visual Seduction & Feigned Stability: The graphic focal point—an AI-generated illustration of a woman in an unfastened silk robe smoking a traditional pipe amid falling red money envelopes (hongbao) and gold coins—is engineered to capture attention and lower skepticism. Above this, a mock console ticker displaying
"SERVER ONLINE"next to a dynamic clock (JLT-2026 // 13:39:52) mimics institutional uptime metrics to make an unstable mirror look like a vetted trading or gaming portal. - Cross-Border Laundering Dynamic: Despite the entire interface utilizing Indonesian gambling vernacular, the underlying distribution pipes are frequently surfaced on streaming sites and Telegram networks operating across South Asia and India. This deliberate geographic detachment lets offshore operators harvest local payment methods (such as domestic UPI rails) through regional money-mule brokers while maintaining their core infrastructure beyond the legal reach of local police forces.
Suspicious Link or Courier SMS?
Verify URLs, APKs, or parcel alerts against our threat database before clicking.
Technical Audit Matrix
| Security / Forensic Vector | Observed Parameter on Linkdl.fit | Operational Threat Level |
| Active Target | [https://linkdl.fit](https://linkdl.fit) | Critical (High-Risk Mirror) |
| Syndicate Attribution | HOKI 108 / LINK SERVER GACOR | Unlicensed Southeast Asian syndicate |
| Claimed Odds & Return | 98.9% RTP | x1000 Multiplier | Fabricated (Uncertified RNG, manipulated client odds) |
| Distribution Gateway | Direct download button: PROMO DOWNLOAD APK | High (Off-market Android sideloading) |
| Financial Rail Model | P2P Virtual Payment Addresses (VPAs) & Mule Accounts | Severe (Account lien / Section 106 BNSS exposure) |
| Regulatory Status | Zero statutory compliance; Violates IT Act Section 69A | Illegal |
Three Technical Exploitation Vectors Beneath the Shell
1. Rigged Backend RNG & Asymmetric Extraction
Legitimate gaming platforms submit their Random Number Generators (RNG) to statutory testing bodies like eCOGRA or BMM Testlabs. Linkdl.fit features arbitrary values written straight into its markup—most notably the 98.9% win rate. Because the underlying gameplay runs on proprietary, unmonitored backends, operators have granular control over player balances. Early small-stake bets may trigger artificial “wins” to build false confidence, but larger deposits inevitably hit algorithmically forced losing streaks or complete account lockouts.
2. Malicious Android APK Sideloading
The orange PROMO DOWNLOAD APK banner bypasses standard app-store protections. When users sideload this package, it frequently requests dangerous runtime permissions outside the sandbox:
android.permission.RECEIVE_SMS: Allows background interception of critical financial alerts, including one-time passwords (OTPs) and UPI authorization codes, without alerting the user.android.permission.BIND_ACCESSIBILITY_SERVICE: Enables UI inspection and automated screen taps, allowing the app to log keystrokes, extract passwords, and potentially authorize financial transfers autonomously.
3. Mule Payment Layering & The Cyber Cell Trap
Deposits on sites like Linkdl.fit are rarely processed through compliant payment aggregators. Instead, users are routed to peer-to-peer (P2P) transfers, sending money to unrelated individual bank accounts or temporary UPI handles. These receiving accounts belong to layered money-mule syndicates.
When another victim of the syndicate files a complaint with the cyber police, authorities track the entire money trail. Under statutory provisions such as Section 106 of the Bharatiya Nagarik Suraksha Sanhita (BNSS), 2023 (formerly Section 102 CrPC in India), cyber cells issue blanket freeze orders across every bank account that touched that money chain. Users who simply sent or received money through the site often find their primary salary or business accounts hit with automated debit freezes and liens.
Incident Response: Financial & Device Remediation
If you interacted with Linkdl.fit, follow these prioritized mitigation steps immediately:
[Immediate Action] ──► Dial 1930 / cybercrime.gov.in ──► Notify Bank Branch ──► Sanitize Android Device
- Activate the Golden Hour Protocol (India): If you transferred money via UPI or NetBanking, call the 1930 Cyber Fraud Helpline within two hours. File a formal complaint at
cybercrime.gov.in. Note the payment’s 12-digit UPI UTR number and the beneficiary’s VPA; quick reporting allows the National Cybercrime Reporting Portal to freeze the funds before the mule account is cleared out. - Handle Bank Account Freezes & Liens: If your bank account receives an unexpected freeze due to an offshore gaming transfer, ask your branch manager for the Cyber Cell Notice Details (the originating Police Station, FIR/Ack number, and the Investigating Officer’s contact info). Submit a formal letter proving you were a defrauded consumer rather than an operator, providing transaction logs and proof of identity to initiate a lien-clearance application.
- Report Malicious Broadcast Vectors: If you were sent the
Linkdl.fitlink or APK via unsolicited SMS, WhatsApp, or Telegram messages, report the sender’s mobile number on the Department of Telecommunications’ Chakshu portal (sancharsaathi.gov.in) to accelerate network-level blocking. - Purge the Android Payload: If you downloaded and installed the site’s APK:
- Turn on Airplane Mode immediately to cut data transmission.
- Boot the phone into Safe Mode by holding the physical Power button, then long-pressing the on-screen Power Off icon.
- Go to Settings > Security > Device Admin Apps and revoke admin rights from any unfamiliar tools.
- Navigate to Settings > Apps, find the betting utility, clear its storage, and uninstall it.
- Reboot your phone normally and immediately change your NetBanking passwords and UPI MPINs from a separate, clean device.
Frequently Asked Questions
Is Linkdl.fit Scam?
Yes, Linkdl.fit operates as a deceptive gambling funnel. It features unverified win rates, operates without a valid gambling license, and uses advance-fee tactics to block withdrawals once real funds are deposited.
Is Linkdl.fit Legit?
No, Linkdl.fit is completely illegitimate. It is an unverified proxy site running deceptive branding (“HOKI 108”) and serving unauthorized APK downloads to bypass app security screenings.
Why does an Indonesian slot site show up in Indian gaming communities?
Offshore betting syndicates use automated tools to spin up regional interfaces while sourcing domestic payment routes globally. They use localized payment networks (like Indian UPI) via local mule accounts, while hosting the websites overseas to shield operators from local police crackdowns.
What happens if I install the APK file from Linkdl.fit?
Installing the .apk exposes your device to off-market security risks. Such files often request excessive background permissions to intercept incoming SMS messages (capturing banking OTPs) and abuse accessibility services to monitor typed passwords and payment details.
Why was my bank account frozen after using Linkdl.fit?
Because Linkdl.fit uses transient, illegal mule accounts to process deposits, those accounts are routinely flagged by law enforcement for financial fraud. When police cyber cells trace the transactions, they issue debit freezes across all connected accounts under Section 106 BNSS / Section 102 CrPC.
Can Linkdl.fit withhold my withdrawal balance?
Yes. The platform uses arbitrary withdrawal blocks. When users attempt to cash out supposed winnings, the platform typically freezes the balance and demands additional “verification,” “GST clearance,” or “tax” payments—funds that are stolen along with the initial deposit.
Every safe click counts. If this post helped, a coffee gesture fuels more scam‑busting investigations.

Related Forensic Teardown • Master Guide
How Domain Churn Scams Keep Illegal Betting Rings Alive →Help Us Spread Awareness
Please share this article to spread awareness. Follow us on social media for more scam alerts.