Linksk.lat Review: Legit Gaming Hub, UPI Trap, or Syndicate Mirror?
Executive Summary & Verdict Callout
Verdict: High-Risk Scam Gateway / Unlicensed Financial Funnel.
Linksk.lat operates as a dangerous cross-border fraudulent funnel engineered to target vulnerable users through deceptive web interfaces, anonymous shell syndicates, and aggressive APK distribution vectors. Our forensic investigation reveals a structured digital trap that front-loads enticing return metrics while deploying opaque payment rails, asymmetric withdrawal restrictions, and severe mobile security hazards.
Operating entirely outside legal and regulatory oversight, the platform exposes unsuspecting visitors to severe monetary loss, unauthorized device access, and third-party financial liability.
Suspicious Link or Courier SMS?
Verify URLs, APKs, or parcel alerts against our threat database before clicking.
Technical Audit & Forensic Parameters
| Forensic Parameter | Observed Technical Detail / Evidence |
| Active Domain URL | [https://linksk.lat](https://linksk.lat) |
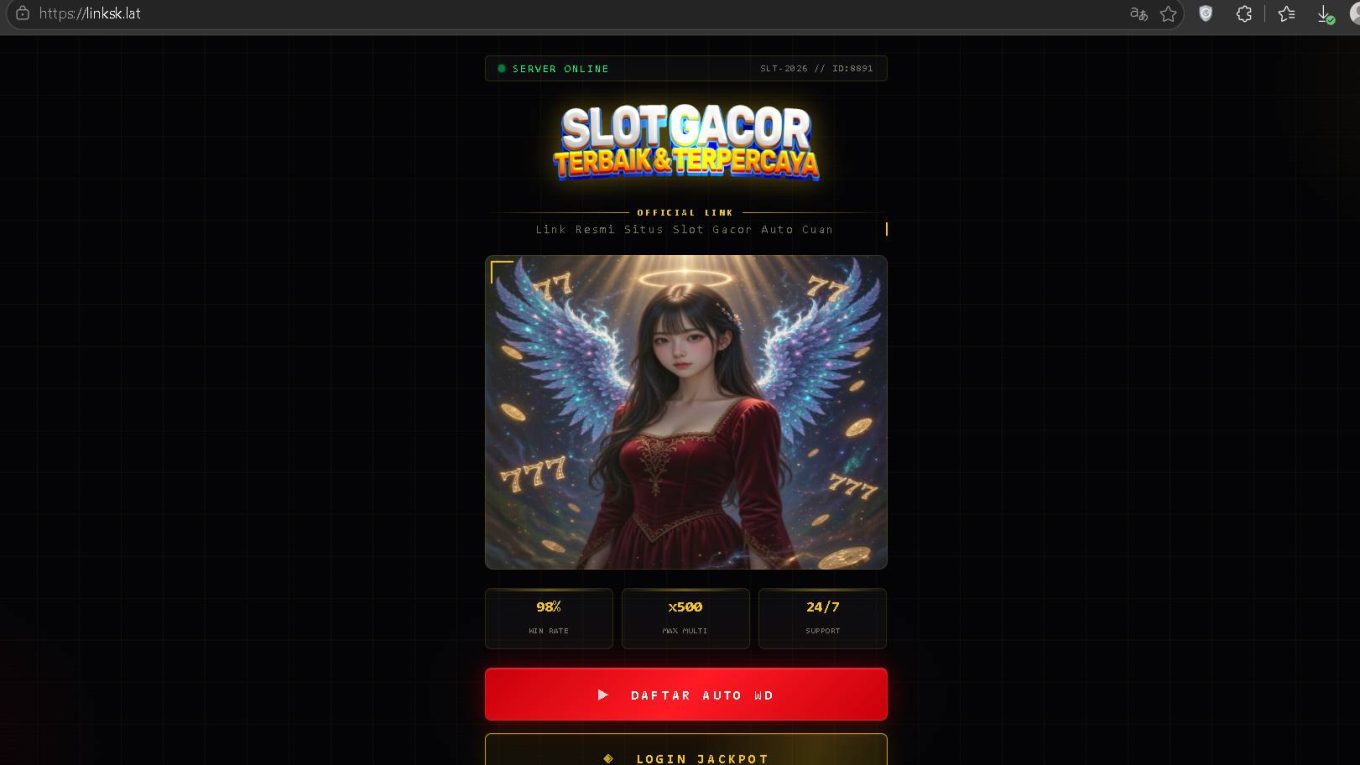
| Observed Brand Names | SLOT GACOR TERBAIK & TERPERCAYA, Official Link “Link Resmi Situs Slot Gacor Auto Cuan” |
| Foreign / Regional Taglines | “SLOT GACOR TERBAIK & TERPERCAYA”, “SERVER ONLINE”, “DAFTAR AUTO WD”, “LOGIN JACKPOT” |
| Claimed RTP / Multipliers | 98% Win Rate, x500 Max Multiplier, 24/7 Support |
| Payment Vectors | Direct UPI gateways, dynamic QR codes, rotating peer-to-peer mule accounts |
| APK Distribution Vectors | Sideloaded package redirection, permission-requesting installer hooks |
| Regulatory Status | Completely unlicensed; zero corporate registry footprints, no recognized gaming commission credentials, protected by anonymous WHOIS privacy shields |
Linguistic & Visual Dissection (Evidence-Based from Screenshot)
Domain Naming Convention & TLD Strategy
The domain name Linksk.lat utilizes a deliberate evasion tactic characteristic of disposable link-aggregators. By combining a truncated keyword prefix (linksk, blending “links” with an abbreviation) with the .lat top-level domain (originally designated for Latin America), syndicate architects bypass standard corporate domain reputation filters and automated social media spam blockers. This volatile infrastructure allows operators to swap mirrors instantly whenever security systems or internet service providers flag their primary distribution channels.
UI Camouflage & Psychological Hooks
A detailed layout analysis of the screenshot exposes a precisely calculated interface designed to lower user guards:
- Thematic Design: Built upon a dark, high-tech grid background with neon-green status indicators (
🟢 SERVER ONLINE,SIT: 2026 // TO: 8894), simulating a secure mainframe or financial server connection. - Mascot & Imagery: Features an AI-generated digital angel or winged guardian figure dressed in a deep red gown, surrounded by floating gold coins and the recurring lucky number sequence
777, creating an immediate aura of divine luck and guaranteed prosperity. - Deceptive Performance Metrics: Prominently displays unverified performance statistics—“98% WIN RATE”, “x500 MAX MULTI”, and “24/7 SUPPORT”—alongside conversion buttons labeled
DAFTAR AUTO WD(Register Auto Withdrawal) andLOGIN JACKPOT. These design cues exploit cognitive biases to induce fast financial deposits.
Cross-Border Mismatch & Target Demographics
A glaring forensic mismatch exists between the domain’s linguistic presentation and its operational targets. While employing Indonesian-origin gaming slang (“Slot Gacor” meaning a loose or high-paying slot machine, and “Auto Cuan” meaning automatic profit), these funnels are aggressively pushed toward Indian digital users via Telegram channels, WhatsApp groups, and surrogate ad networks. This jurisdictional disconnect allows syndicates to launder capital across multi-tier cross-border channels, complicating recovery for local victims.
5 Critical Technical Deceptions
- Backend Syndication & White-Label Shells: Linksk.lat is merely an entry-level shell connected to centralized, illicit white-label gaming backends. These servers allow anonymous operators to alter game outcomes remotely while shielding the principal beneficiaries from local law enforcement.
- Fabricated Mathematical Odds (RNG Violations): Despite bold claims of a 98% win rate and x500 multipliers, the platform lacks any independent Random Number Generator (RNG) verification from accredited laboratories like eCOGRA. Algorithms are programmatically adjusted to encourage initial wins before triggering unrecoverable losses.
- Android APK Permission Abuse: Users registering through the platform are frequently nudged to download standalone
.apkfiles outside official app stores. These packages demand dangerous system permissions, includingRECEIVE_SMS,READ_SMS, andBIND_ACCESSIBILITY_SERVICE, enabling background OTP interception and automated financial malware operations. - Anonymous Infrastructure Masking: The platform leverages enterprise-grade reverse proxies, domain privacy guards, and rotating hosting providers to hide its true origin servers, ensuring that victims have no identifiable entity to serve legal notices or dispute claims against.
- Upfront Clearance & Tax Fee Extortion: When users accumulate fictional winnings and request a payout, withdrawals are locked indefinitely. The platform demands upfront “tax clearance deposits,” “channel activation fees,” or “risk verification charges” to unblock funds, pocketing the extra payments before terminating all communication.
Emergency Remediation & Financial Recovery (India & Global Context)
If you have interacted with Linksk.lat, transferred funds via UPI, or exposed your personal data, execute this containment protocol immediately:
- Golden-Hour Cyber Helpline Reporting: Immediately contact the national cybercrime helpline at 1930 or file a detailed fraud report on the official portal at cybercrime.gov.in. Reporting within the golden hour maximizes the likelihood of freezing illicit transfers in transit.
- Managing Cyber Cell Bank Account Freezes: If your Indian bank account has been hit with a debit freeze, lien, or hold under Section 106 of the Bharatiya Nagarik Suraksha Sanhita (BNSS) or Section 102 of the CrPC due to interactions with mule accounts linked to this syndicate:
- Reach out to your bank’s home branch nodal officer to secure the exact FIR reference number, Cyber Cell station, and Investigating Officer (IO) contact details.
- File a formal legal response establishing your lack of criminal intent, providing complete transaction ledgers, communication logs, and evidence proving you were an unwitting victim of an online financial scam.
- Reporting Communication Vectors: Report all fraudulent Telegram groups, WhatsApp advisory channels, and phishing links promoting Linksk.lat to the Department of Telecommunications (DoT) through the Chakshu portal on the Sanchar Saathi platform.
Android Quarantine & Spyware Neutralization
If you accessed Linksk.lat on an Android device or sideloaded any associated application package, perform these steps immediately to sanitize your device:
- Boot into Safe Mode: Restart your smartphone into Safe Mode to temporarily disable all third-party applications and halt malicious background processes.
- Revoke Device Administrator Access: Open Settings > Security > Device Administrator Apps (or Special App Access). Review the list for any unfamiliar applications holding administrative rights and revoke them immediately.
- Purge Hidden APK Packages: Navigate to Settings > Apps, locate any unverified tools or sideloaded applications installed during your browsing session, and completely uninstall them.
- Reset Default Messaging & Permissions: Verify your default SMS handling and accessibility configurations to ensure no unauthorized application retains reading access to your incoming text messages and one-time passwords (OTPs). Run a comprehensive scan using a trusted mobile security solution.
Security Resource Block
🛡️ Recommended Digital Safety Stack
- Mobile Antivirus & Malware Removal: Safeguard your phone against background APK spyware, keyloggers, and malicious permission hooks using enterprise-grade mobile security tools (e.g., Bitdefender Mobile Security or Malwarebytes).
- Identity Theft & Credit Monitoring: Protect your sensitive PII, PAN, and Aadhaar information from unauthorized financial loan applications with active credit monitoring services.
- Anti-Phishing VPN: Shield your network traffic from DNS spoofing, rogue redirect scripts, and malicious IP logging with a verified zero-log Virtual Private Network.
Frequently Asked Questions (FAQ)
Is Linksk.lat a scam?
Yes, absolutely. Linksk.lat is an unlicensed fraudulent portal engineered to deceive users through false winning promises, fake promotional metrics, and manipulated gaming mechanics designed solely to misappropriate deposited funds.
Is Linksk.lat legit?
No. The platform possesses no legal corporate registration, holds zero valid gaming licenses, and operates completely outside regulatory oversight, making every transaction on the site unsafe.
Why is my withdrawal blocked on Linksk.lat?
Withdrawals are intentionally blocked by design. The platform uses artificial friction—such as demanding upfront taxes, channel activation fees, or verification deposits—to extract additional money from victims before cutting off all communication.
Why has my bank account been frozen after interacting with this site?
When you transfer funds to or receive funds from platforms like Linksk.lat, you are interacting with layered mule accounts. Law enforcement cyber cells tracking illicit money flows routinely place debit freezes and liens on all linked bank accounts under Section 106 BNSS / 102 CrPC.
What should I do if I downloaded an APK file from Linksk.lat?
Immediately disconnect your device from the internet, boot into Safe Mode, revoke any Device Administrator permissions granted to unfamiliar apps, uninstall the rogue APK package, and change your netbanking and UPI PINs from a secure, uncompromised device.
How does Linksk.lat bypass internet service provider blocks?
The operators use frequent domain rotation and dynamic gTLD switching (such as .lat) combined with cloud-based reverse proxies to circumvent national domain blacklists and spam filters.
While direct reversals are difficult once funds settle in a beneficiary account, reporting the transaction within the golden hour via the 1930 helpline and registering a formal complaint on cybercrime.gov.in can trigger a legal hold on the recipient mule account.
Are the 98% win rate and x500 multipliers real?
No. These metrics are entirely fabricated UI elements designed to create an illusion of statistical probability and entice users into depositing real money into an unregulable funnel.
Every safe click counts. If this post helped, a coffee gesture fuels more scam‑busting investigations.

Related Forensic Teardown • Master Guide
How Domain Churn Scams Keep Illegal Betting Rings Alive →Help Us Spread Awareness
Please share this article to spread awareness. Follow us on social media for more scam alerts.