Judis.fit Review: Legit Gaming Hub, UPI Trap, or Syndicate Mirror?
Executive Summary & Verdict Callout
Judis.fit is a dangerous, unlicensed offshore gambling gateway and surrogate phishing mirror operating as an illicit funnel for the transnational “HOKI108” syndicate. Disguised behind a wellness-oriented top-level domain (.fit) to bypass corporate threat intelligence filters, the portal acts as a financial conduit designed to steer consumer traffic toward unmonitored money laundering corridors.
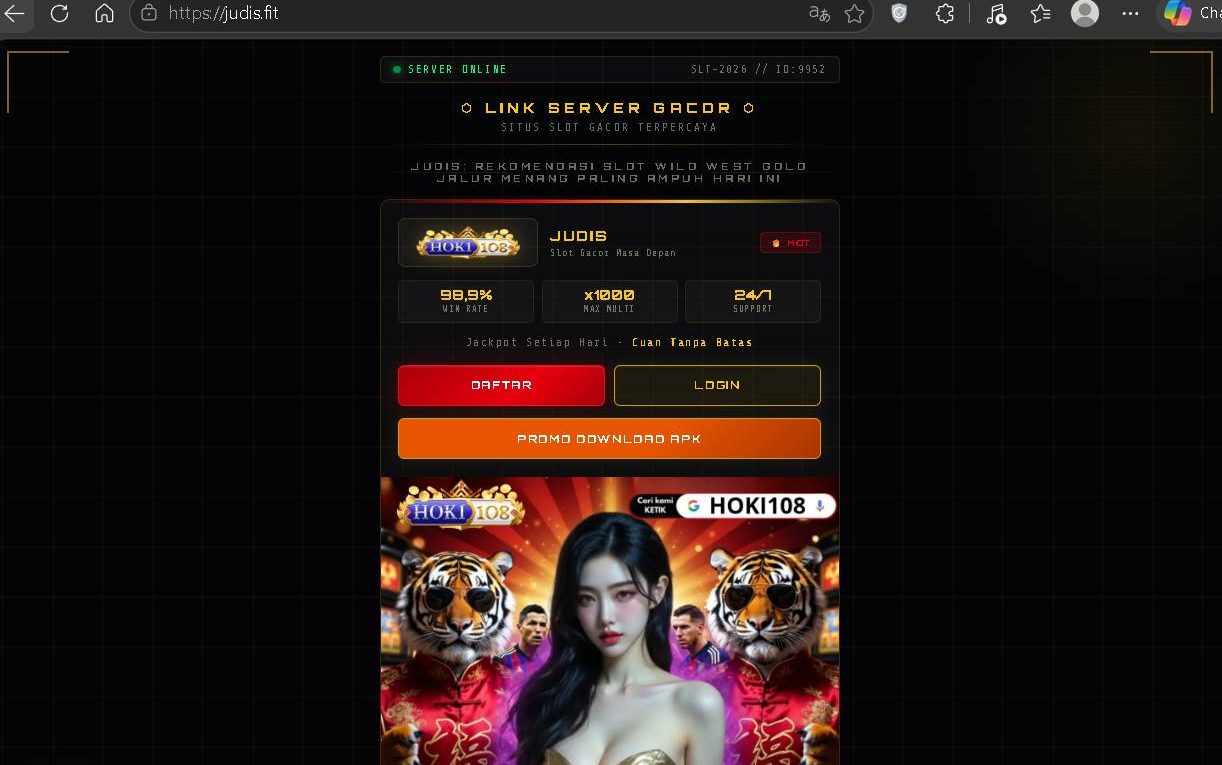
The site relies on deceptive technical artifacts—including an arbitrary console terminal status (SLT-2026 // ID: 9952), impossible statistical odds (a 98.9% win rate), and game-specific win promises targeting titles like Wild West Gold—to drive conversions.
Sideloading the promoted off-market Android package (PROMO DOWNLOAD APK) introduces device-level spyware vectors, while processing deposits through rotating mule virtual payment addresses (VPAs) puts victims at immediate risk of a bank account cyber cell debit freeze under Section 106 of the Bharatiya Nagarik Suraksha Sanhita (BNSS) / Section 102 CrPC.
Technical Audit & Forensic Parameters
| Forensic Parameter | Technical Finding & Visual Evidence |
| Active Domain URL | [https://judis.fit](https://judis.fit) (Observed Diagnostic Header: SLT-2026 // ID: 9952) |
| Observed Syndicated Brands | JUDIS (“Slot Gacor Masa Depan”) / HOKI108 (“Situs Slot Gacor Terpercaya”) |
| On-Screen Linguistic Artifacts | “JUDIS: REKOMENDASI SLOT WILD WEST GOLD JALUR MENANG PALING AMPUH HARI INI”, “Cari kami KETIK G HOKI108”, “Cuan Tanpa Batas” |
| Promoted Multipliers & Odds | 98.9% Win Rate (Statistically fraudulent PRNG claim), x1000 Max Multi, 24/7 Support badge |
| Direct Distribution Endpoints | High-contrast orange callout: PROMO DOWNLOAD APK |
| Gateway Action Elements | High-contrast registration: DAFTAR and portal login: LOGIN |
| Observed Settlement Vectors | Dynamic peer-to-peer mule VPAs, unlisted UPI merchant intent links, shadow crypto aggregators |
| Regulatory & Licensing Status | Completely Unlicensed. No verifiable registration with Curacao eGaming, MGA, UKGC, or any national financial or gaming authority. |
📧 Need Legal Assistance?
Contact the author for legal consultations, case evaluations, and professional inquiries.
Linguistic & Visual Dissection (Evidence-Based from Screenshot)
1. Semantic Masquerading & The .fit TLD Cloaking
The URL judis.fit represents a deliberate evasion tactic. The root label “Judi” is the direct Indonesian word for gambling, making the brand name an open declaration to regional punters. However, pairing this black-market term with the .fit gTLD is an evasion strategy.
Enterprise network filters, school web blocks, and social media spam detection algorithms typically categorize .fit domains under health, athletics, or lifestyle categories. By hiding gambling-related operations behind a lifestyle suffix, the syndicate maintains operational deliverability, slipping past corporate firewalls and basic parental controls before security scanners can update their blacklists.
2. UI Camouflage: Exploiting Niche Game Themes
The visual layout uses calculated sensory manipulation to simulate an unfair player advantage:
- The Wild West Gold Exploit Hook: Unlike generic casino portals, the header text explicitly states: “JUDIS: REKOMENDASI SLOT WILD WEST GOLD JALUR MENANG PALING AMPUH HARI INI” (Today’s most effective winning track for Wild West Gold). By referencing a real, highly volatile Pragmatic Play slot title, the site creates a false sense of insider information, convincing players that the link holds a private, pre-configured exploit track.
- Simulated Network Terminal: A terminal bar at the top displays
🟢 SERVER ONLINEnext toSLT-2026 // ID: 9952. This design mimics a privileged, low-latency connection to a real-time host server, convincing the user that the portal is actively communicating with gaming hardware rather than running a web proxy. - Visual Opulence & Cultural Priming: Flanked by twin white Bengal tigers wearing mirrored sunglasses and draped in gold chains beside red “Fu” (fortune) medallions, the page visualizes effortless wealth. This is combined with the Indonesian promise “Cuan Tanpa Batas” (Endless Profits) and a glowing red
HOTbadge to encourage impulsive sign-ups via the bright redDAFTARbutton. - Algorithmic Search Manipulation: The UI displays an explicit Google search instruction: “Cari kami KETIK G HOKI108” (Find us by typing HOKI108 into Google). This crowdsources search volume to push syndicate keywords up search engine rankings, creating organic search credibility despite ongoing domain seizures.
3. Cross-Border Traffic Funnels
While the visual identity and phrasing are grounded in Indonesian dialect, the hosting architecture is deployed to handle international traffic. Syndicates run surrogate ads on pirated streaming sites, short-video platforms, and rogue Telegram tipster groups targeting Indian and South Asian users. When non-Indonesian IP addresses land on the page, backend routing scripts redirect deposit checkouts away from local Indonesian e-wallets toward domestic Indian Unified Payments Interface (UPI) gateways.
Suspicious Link or Courier SMS?
Verify URLs, APKs, or parcel alerts against our threat database before clicking.
5 Critical Technical Deceptions
[ Visitor Lands on Judis.fit ]
               │
       ┌───────┴──────────────────────────────┐
       ▼                                      ▼
[ "DAFTAR" (Account Creation) ]        [ "PROMO DOWNLOAD APK" ]
       │                                      │
  Mule VPA Routing (UPI Layers)          Sideloaded Malicious APK
       │                                      │
  P2P Cryptocurrency Conversion          High-Privilege Android Hooks
       │                                 (`RECEIVE_SMS`, `ACCESSIBILITY`)
       ▼                                      ▼
Interstate Cyber Cell Bank Lien / Freeze   Silent OTP Theft & Account Drain
(Section 106 BNSS / 102 CrPC)
1. Mule Account Money Laundering Architecture
Deposits on judis.fit bypass regulated commercial merchant gateways. Instead, payments are routed through disposable peer-to-peer (P2P) accounts and mule VPAs. These intermediary accounts—often rented or stolen from unsuspecting students or migrant workers—immediately split incoming deposits. The laundered fiat currency is then funneled into P2P cryptocurrency purchases on unmonitored platforms, leaving the original depositor’s bank account directly linked to an illicit financial chain.
2. Algorithmic Rigging & Fictitious Odds
The platform’s 98.9% Win Rate and x1000 Max Multi badges are purely decorative. Genuine iGaming operators are mandated to use certified Pseudo-Random Number Generators (PRNGs) audited by independent agencies such as eCOGRA or BMM Testlabs, with real returns typically between 92% and 96%. Judis.fit uses cracked, unverified scripts where administrators manually adjust the house edge, luring players with artificial initial wins before shutting down payouts entirely.
3. Sideloaded APK Surveillance & OTP Interception
The PROMO DOWNLOAD APK button directly distributes an unverified Android application package (.apk) from non-standard servers, bypassing Google Play Protect. Once installed, these files frequently request excessive background permissions:
android.permission.RECEIVE_SMS/READ_SMS: Grants silent access to incoming SMS streams, allowing threat actors to intercept bank-issued one-time passwords (OTPs).android.permission.BIND_ACCESSIBILITY_SERVICE: Enables the malicious payload to record keystrokes, interact with screen elements, and authorize background fund transfers without the user’s manual input.
4. Anonymized Shell Infrastructure
Judis.fit features zero verifiable corporate information. There are no registered company names, no real office locations, no identifiable Data Protection Officers (DPOs), and no dispute-handling procedures. The site uses bulletproof offshore hosting and reverse proxies explicitly chosen to evade digital forensics, subpoenas, and international law enforcement operations.
5. Advance-Fee Withdrawal Blocks
The site operates on an asymmetric payment model: deposits are confirmed immediately, but withdrawals are intentionally blocked. Users attempting to cash out their balances encounter fabricated system errors or compliance warnings. Support staff then demand “clearance fees,” “withholding tax payments,” or “tier verification fees.” Once these additional payments are sent, the operators ban the account, leaving the victim with total losses.
Emergency Remediation & Financial Recovery
If you have interacted with judis.fit, transferred money, or downloaded files from the page, take these corrective measures immediately:
1. Golden-Hour Fraud Response
- Call the 1930 Helpline Immediately: If you are based in India, contact the National Cybercrime Reporting Helpline (1930) straight away. Reporting the incident within the “golden hour” allows the Citizen Financial Cyber Fraud Reporting and Management System (CFCFRMS) to place an emergency freeze on the recipient mule account before your money is converted into cryptocurrency.
- File an Official Complaint on cybercrime.gov.in: Submit a formal report on the National Cybercrime Reporting Portal. Make sure to upload unedited screenshots of the transaction receipts, the UTR numbers, the recipient VPA, and your interactions on the platform.
- Request a Bank Chargeback: Immediately alert your bank’s fraud division that your transfer was diverted through an unauthorized merchant funnel, and request an emergency recall of the funds.
2. Resolving a Cyber Cell Debit Freeze (Section 106 BNSS / 102 CrPC)
If your bank account is subjected to a debit freeze or forensic lien, your funds were traced to a money-laundering node flagged by law enforcement:
- Contact your bank’s nodal officer to retrieve the full Cyber Cell Freezing Notice, including the Crime Reference Number, the originating Police Station/State Cyber Cell, and the Investigating Officer’s (I.O.) contact email.
- Prepare a detailed formal affidavit along with an evidence dossier showing that you were targeted by a fraudulent platform rather than acting as a deliberate mule or syndicate accomplice.
- Submit this evidence to the Investigating Officer to request an official No Objection Certificate (NOC) and unfreeze the unencumbered balance in your account.
3. Report Communication Channels on Chakshu
If you were directed to judis.fit through unsolicited SMS broadcasts, WhatsApp messages, or cold calls, report the identifiers on the Chakshu portal within the Department of Telecommunications’ Sanchar Saathi platform (sancharsaathi.gov.in) to aid authorities in blocking the underlying SIM cards and hardware.
Android Quarantine & Spyware Neutralization
If you clicked PROMO DOWNLOAD APK and installed the app on an Android device, treat your phone as compromised:
- Disconnect Network Access: Immediately switch on Airplane Mode and disable Wi-Fi to stop unauthorized data transfers and prevent remote access to your device.
- Reboot into Safe Mode:
- Press and hold the physical Power button.
- Long-press the Power Off or Restart icon on the screen until the Safe Mode prompt appears. Confirm the selection. Safe Mode boots the operating system while preventing all third-party downloaded scripts from running.
- Revoke Device Administrator Rights:
- Go to
Settings➔Security➔Device Admin Apps. - Look for unrecognized applications masquerading under names like “System Engine,” “Wild West Tool,” or “Hoki Client” and disable their administrative permissions immediately.
- Go to
- Uninstall Malicious Packages:
- Go to
Settings➔Apps➔See All Apps. - Find the sideloaded APK or any recent, unfamiliar applications and tap Uninstall.
- Go to
- Restore Default Settings & Scan:
- Check
Settings➔Apps➔Default Appsand ensure your phone’s native messaging service is set as the default SMS app. - Open the Google Play Store, select your profile, navigate to Play Protect, and run a complete malware scan.
- Check
High-RPM Cybersecurity Resource Block
🛡️ Personal Threat Defense Suite
- Mobile Antivirus & Spyware Removal: Identify and remove hidden remote-access trojans (RATs) and malicious APK droppers using an industry-recognized mobile security scanner (e.g., Bitdefender Mobile Security or Malwarebytes).
- Identity Theft & Credit Protection: Guard your personal details and prevent unauthorized loans or account creation if your KYC data was shared on unverified portals (e.g., Aura or Experian IdentityWorks).
- Anti-Phishing & Traffic Protection VPN: Automatically block fraudulent mirrors, rogue proxies, and malicious scripts at the DNS layer using advanced web-filtering software (e.g., NordVPN Threat Protection or Surfshark CleanWeb).
Frequently Asked Questions (FAQ)
Is Judis.fit Scam?
Yes, Judis.fit is an active online scam. The domain operates as an unlicensed surrogate funnel that uses fabricated 98.9% win statistics, false game strategy claims, and rotating mule accounts to misappropriate user deposits without offering legitimate withdrawals.
Is Judis.fit Legit?
No, Judis.fit is completely illegitimate. It holds no valid gaming licenses, has no verifiable corporate registrations, and uses a health-related domain extension (.fit) to bypass standard security filters while operating unverified, predatory software.
What happens if I install the “PROMO DOWNLOAD APK” from Judis.fit?
Downloading the unverified APK bypasses Google Play Protect safeguards. These off-market packages frequently request dangerous permissions like RECEIVE_SMS and Accessibility Services, allowing operators to secretly intercept banking OTPs and steal private account information.
Why is my bank account frozen after depositing funds into Judis.fit?
Your bank account likely received a debit freeze under Section 106 BNSS / Section 102 CrPC because your deposit was transferred into a mule account linked to an interstate cybercrime inquiry. Once an account in the transaction chain is flagged, law enforcement freezes all connected accounts for forensic tracing.
Can I withdraw money I have won on Judis.fit?
No. The winnings shown on the platform are simulated by the site’s operators. When you request a withdrawal, the system will block the transfer and often demand extra upfront “clearance” or “tax” payments, which will only lead to further financial loss.
Every safe click counts. If this post helped, a coffee gesture fuels more scam‑busting investigations.

Related Forensic Teardown • Master Guide
How Domain Churn Scams Keep Illegal Betting Rings Alive →Help Us Spread Awareness
Please share this article to spread awareness. Follow us on social media for more scam alerts.