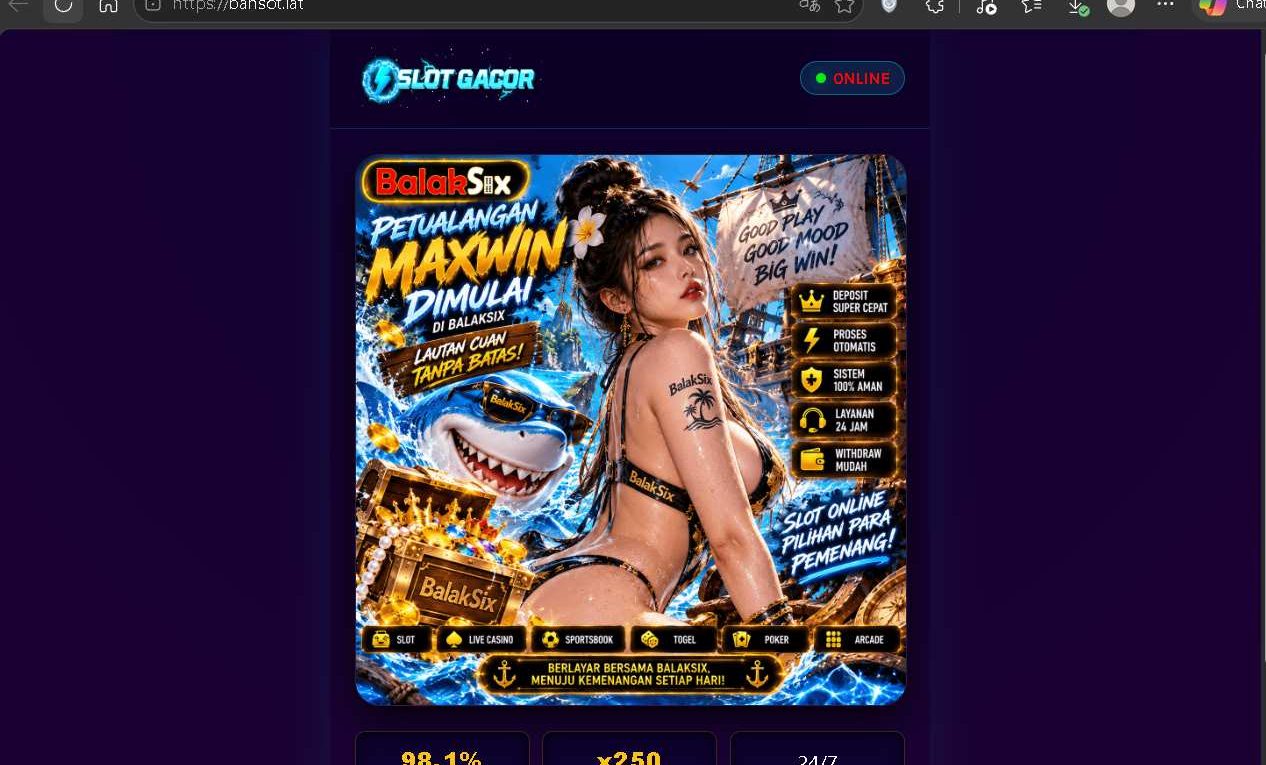
Bansot.lat Review: Inside the BalakSix Ocean Mirror, Fake RTP Metrics, and High-Risk Funnels
Finding yourself suddenly redirected to Bansot.lat usually happens without warning or intentional clicks. Instead, landing on Bansot.lat is the classic outcome of background traffic hijacking and stealth ad-network routing engineered by high-velocity gambling syndicates.
With flashing tropical visuals, pirate treasure chests, and promises of unlimited payouts, the site works hard to turn casual curiosity into instant sign-ups. Beneath that polished veneer, however, lies an unregulated offshore mirror node that presents serious hazards to your personal data and banking balances.
Here is an independent, detailed breakdown of how Bansot.lat operates, what its claims actually mean, the major warning signs to recognize, and the exact steps to protect your digital accounts.
5 Critical Red Flags on Bansot.lat
Before analyzing the site’s layout or features, it is vital to understand the structural warnings that make interacting with this gateway unsafe:
Suspicious Link or Courier SMS?
Verify URLs or APKs before clicking.
1. Fabricated Payout and Win-Rate Claims
Bansot.lat prominently promotes a “98,1% Win Rate” paired with an “x250 Max Multi” directly on its entry portal. In mathematically audited iGaming frameworks, blanket win rates above 98% are unsustainable fictions used purely to entice impulsive deposits. Without authentic verification stamps from recognized independent testing agencies—such as eCOGRA, GLI, or BMM Testlabs—these advertised payout rates are arbitrary numbers controlled entirely by backend operators.
2. Complete Lack of Verifiable Regulatory Licensing
Legitimate wagering platforms and online sportsbooks operate under traceable, publicly searchable regulatory licenses issued by recognized supervisory bodies like the Malta Gaming Authority (MGA) or the UK Gambling Commission (UKGC). Bansot.lat displays no valid corporate registration numbers, no legal company jurisdiction, and no verifiable regulatory certificates. Entering your funds here leaves you without any consumer protection ombudsman or legal dispute process if balances are withheld.
3. Disposable Domain Churn Architecture
The domain pairs a temporary alphanumeric string with a cheap .lat top-level domain (TLD). These short-lived domains are registered in bulk specifically because operators expect telecom firewalls and anti-malware databases to block them within weeks. Regulated businesses build trust on stable, verified web infrastructure; disposable mirror operators simply discard burned URLs and spin up fresh clones when filters catch up.
4. Asymmetric Cash Flow Architecture
The portal advertises instant balance updates and automated funding under promises like “Deposit Super Cepat” (Super Fast Deposit) and “Proses Otomatis” (Automated Process). Conversely, outgoing payments (“Withdraw Mudah”) exist without any verifiable service level agreements. Users dealing with clone networks frequently run into unexpected wagering rollovers, administrative delays, or sudden account lockouts when requesting cash-outs.
5. High Risk of Identity and Financial Data Harvesting
Signing up on unverified proxy mirrors requires submitting sensitive details such as personal mobile numbers, banking identifiers, and digital wallet accounts. Because these platforms ignore international privacy safeguards and consumer data compliance, player credentials are regularly stored in unencrypted environments that are vulnerable to data breaches, phishing campaigns, and unauthorized telemarketing lists.
Player Safety Blueprint: Prevention & Solutions
Protect assets before interacting with unverified mirrors, or follow mitigation steps if data was shared.
Never pay secondary “clearance taxes” or “unlock fees” to release trapped funds.
Uninstall suspicious packages, reboot into Safe Mode, and run an updated antivirus scan.
Reset passwords on linked emails/wallets immediately and enable authenticator-app 2FA.
Contact your bank’s fraud desk to dispute transactions under merchant fraud.
Block unsolicited contacts and disregard third-party “fund recovery” hackers requesting fees.
What Does Bansot.lat Offer and Claim?
Promoting the brand “BalakSix” alongside high-visibility banners like “Slot Gacor,” Bansot.lat presents itself as an exciting, all-in-one entertainment gateway.
[ Bansot.lat Gateway Front ]
             │
             ├──► Online Slots ("Slot Gacor" & "Petualangan Maxwin")
             ├──► Live Casino Table Streams (Roulette, Baccarat, Blackjack)
             ├──► Sportsbook Betting
             ├──► Lottery & Numbers Draws (Togel)
             ├──► Digital Poker & Casual Arcade Rooms
             └──► Automated Local E-Wallet / Instant Banking Channels
The promotional artwork uses slogans such as “Petualangan Maxwin Dimulai di BalakSix – Lautan Cuan Tanpa Batas” (The Maxwin Adventure Begins at BalakSix – An Endless Ocean of Profits). It highlights:
- Broad Gaming Categories: Dedicated hubs for slots, live casino tables, sports betting, poker, lottery (togel), and interactive arcade titles.
- Speed and Security Assurances: Graphic badges claiming a “100% Safe System” (Sistem 100% Aman) and 24/7 client care.
- Quick Onboarding: High-contrast buttons encouraging users to jump straight into player accounts or VIP tiers.
How Does Bansot.lat Function Behind the Scenes?
The technological infrastructure behind Bansot.lat is designed for quick deployment and effortless evasion:
- Forced Redirection Pathways: Most visitors arrive on Bansot.lat not by entering the URL, but through rogue ad networks, clickjack overlays on streaming sites, or background redirect scripts.
- Reverse Proxy Node: The domain does not host an independent casino gaming engine. It serves as a temporary front-end skin connecting directly to an offshore database running the shared BalakSix betting system.
- Bypassing Telecom Blacklists: When public telecom authorities and cyber filtering systems (such as Indonesia’s Internet Positif / Kominfo registries) flag and block
bansot.lat, operators seamlessly point their server traffic to an identical, newly registered clone. The master operational engine remains unchanged, while users on the abandoned domain are left without recourse.
Immediate Steps to Protect Your Device, Identity, and Funds
If you accidentally opened Bansot.lat, tapped promotional prompts, or entered sensitive data, taking quick protective steps can prevent further exposure:
- Close the Tab and Clear Cached Files: Exit the page immediately without accepting browser notifications. Go into your browser settings to wipe cookies, cached images, and site permissions to clear active tracking cookies.
- Inspect Active Browser Extensions: Look over your installed extensions to ensure unauthorized add-ons or suspicious scripts are not triggering background redirects to alternative mirrors.
- Switch to Secure DNS Filtering: Set your device or router to use secure, privacy-centric DNS services like Cloudflare (
1.1.1.2) or Quad9 (9.9.9.9), which proactively block suspicious, newly created mirror domains. - Alert Your Banking Institution: If you submitted payment card numbers, UPI IDs, or digital wallet details, contact your bank’s fraud monitoring unit immediately. Request a card freeze and file a formal inquiry regarding unauthorized merchant transactions.
- Watch Out for Secondary Asset Recovery Scams: Disregard any unprompted messages on Telegram, WhatsApp, or email claiming to “retrieve lost balances” from offshore sites. These represent secondary phishing traps targeting people who interacted with questionable gambling portals.
Frequently Asked Questions (FAQ)
1. Is Bansot.lat a scam?
Yes. Bansot.lat shows the clear hallmarks of an unlicensed, high-risk clone mirror. It operates without verifiable gaming licenses, relies on an expendable domain, and provides no legal protections or formal dispute escalation paths for user balances.
2. Is Bansot.lat legit?
No. Bansot.lat is not an authorized, legally recognized betting platform. It functions as a transient mirror designed to evade internet service provider restrictions, lacking independent game fairness audits and transparent corporate ownership.
3. What does “Petualangan Maxwin Dimulai di BalakSix” mean on the homepage?
This translates roughly to “The Maxwin Adventure Begins at BalakSix”. It is promotional copy crafted to give visitors the impression of effortless, massive slot wins, despite the absence of verified payout calculations.
4. Are the advertised 98.1% win rate and x250 multiplier verified?
No. These figures are unverified promotional claims designed to generate excitement. Legitimate gaming sites must submit their Return to Player (RTP) figures to certified third-party testing labs, whereas uncertified mirrors can display arbitrary figures without accountability.
5. Why do platforms like BalakSix keep changing their web addresses?
Because government bodies, regional internet providers, and security programs continually blacklist unlicensed gambling portals. When an address gets blocked, operators abandon it and deploy a fresh clone so their deposit funnels remain active.
6. Can I get my money back if Bansot.lat blocks my withdrawal request?
Securing refunds from unverified mirror portals is extremely difficult because incoming payments are typically routed through automated peer-to-peer rails, unhosted crypto wallets, or private e-wallets. Your best recourse is to promptly alert your bank or card issuer’s fraud division regarding deceptive merchant practices.
7. What happens to my profile if Bansot.lat is blocked by my internet provider?
If the domain is blacklisted and you do not possess direct links to subsequent mirror nodes, you lose immediate access to your profile and any remaining account funds. These portals rarely provide dedicated recovery portals once a URL goes offline.
8. Does simply opening Bansot.lat infect my device with a virus?
If your browser and device operating system are up to date, simply loading the page carries minimal immediate malware risk. However, leaving the page open increases exposure to clickjack overlays, misleading browser notification prompts, and risky software download prompts. Close the window immediately.
Every safe click counts. If this post helped, a coffee gesture fuels more scam‑busting investigations.

Help Us Spread Awareness
Please share this article to spread awareness. Follow us on social media for more scam alerts.