Unpacking Empirel.fit: The Mechanics of an Offshore Online Gambling Landing Portal/Mirror Scam
Encountering Empirel.fit reveals the inner workings of an offshore online gambling landing portal/mirror scam, a covert gateway set up to siphon digital payments into untraceable betting networks. Rather than operating as an independent gaming platform, this stripped-down portal bypasses regulatory firewalls and regional internet blacklists to funnel unsuspecting visitors into high-risk, unregulated gambling syndicates.
Behind the flashy sci-fi aesthetic and bold promises of overnight profits lies an aggressive conversion trap designed to strip users of their capital while offering zero legal standing or consumer recourse. Whether you discovered this link through social media spam, an automated text message, or a suspicious redirect, exploring what happens after you click illuminates why these temporary storefronts pose a severe threat to your digital identity and finances.
Anatomy of the Threat: Understanding Gambling Mirror Portals
To see why sites like Empirel.fit are inherently hazardous, one must first demystify what an offshore online gambling landing portal/mirror scam actually entails.
Across global markets, cybercrime units and telecom providers routinely detect and ban unauthorized betting domains. When an illegal casino loses its web address, its steady flow of player deposits vanishes overnight. To circumvent this, organized operators run continuous domain-cycling operations:
[Target Visitor via Ads / Spam Redirects]
                   │
                   ▼
       [Disposable Frontend: Empirel.fit]
                   │
    ┌──────────────┴──────────────┐
    ▼                             ▼
[Credential & Account Harvest]  [Malicious APK Sideloading]
    │                             │
    ▼                             ▼
[Shadow Syndicate Pool]         [Compromised Mobile Device]
(No Legal License / Rigged)     (Silent SMS & 2FA Capture)
Instead of hosting their complete software catalog openly—which triggers rapid detection by anti-fraud scanners—syndicates deploy cheap, disposable top-level domains like .fit, .lol, or .top. These mirror addresses fulfill a single purpose: acting as disposable electronic bridges. They shield the backend database from network administrators, evade ISP domain filters, and funnel user deposits into shadow accounts.
Once regulatory agencies blacklist a specific URL, the syndicate drops it without hesitation and spins up an identical template on another fresh address in minutes.
Suspicious Link or Courier SMS?
Verify URLs, APKs, or parcel alerts against our threat database before clicking.
Field Breakdown: How Empirel.fit Traps Visitors
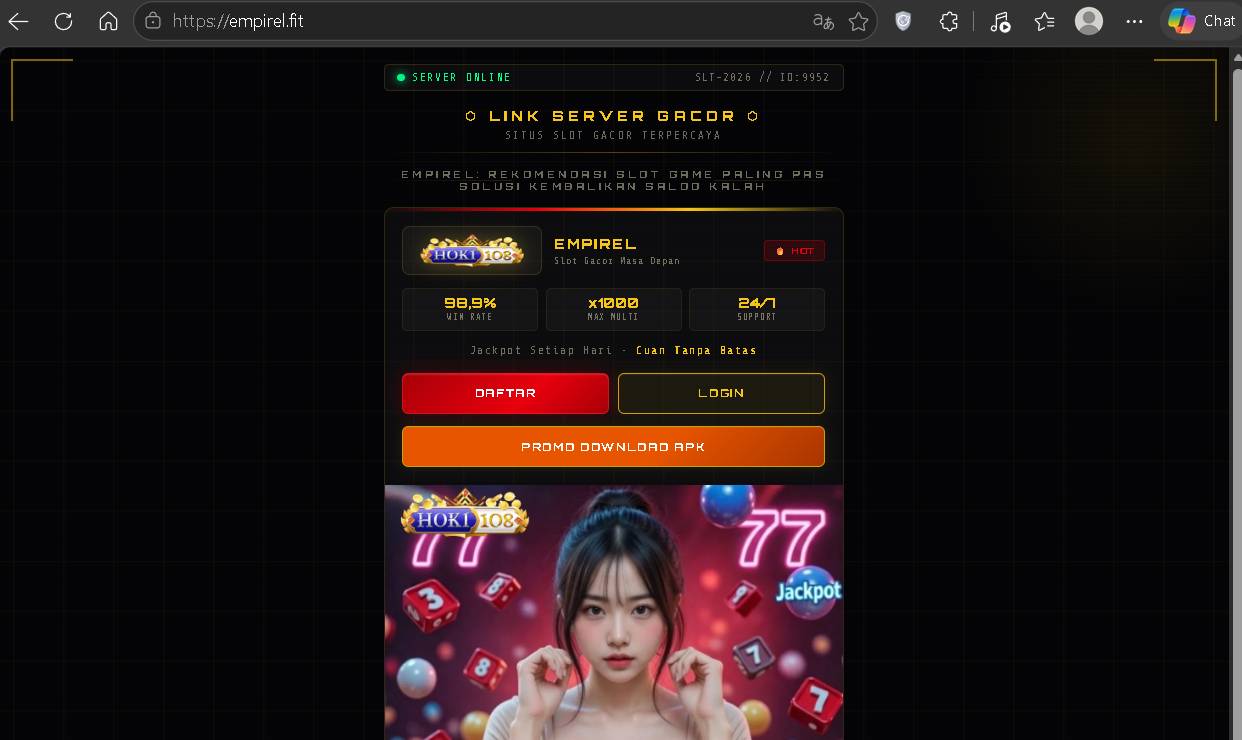
Examining the visual layout and underlying mechanics of Empirel.fit illustrates how modern rogue operations strip out everything non-essential to focus purely on taking money and harvesting credentials.
The Façade: Misleading Claims & Emotional Hooks
The landing page greets visitors with hyper-targeted marketing hooks engineered to manipulate player psychology:
- The “Slot Gacor” Illusion: Emblazoned with tags like HOKI 108 and Link Server Gacor, the page caters to players searching for slots on a supposed winning streak.
- Statistical Impossibilities: It boldly advertises a 98.9% Win Rate alongside a x1000 Max Multi. In certified gaming mathematics, such fixed returns are an outright fiction.
- Loss-Chaser Exploitation: The tagline directly pitches itself as a “solusi kembalikan saldo kalah”—a predatory lure explicitly targeted at gamblers desperate to recoup previous financial losses.
- The Illusion of Legitimate Service: A static “24/7 Support” badge sits prominently in the header to simulate the appearance of a regulated, accountable company.
Under the Hood: The Conversion Pipeline
The interaction sequence on Empirel.fit is built to minimize friction during deposit while completely locking out withdrawals:
- Unmonitored Onboarding (
DAFTAR): Clicking the registration button reveals an open data-intake form. By removing mandatory identity verification (KYC), the platform collects phone numbers, names, and local payment credentials with zero oversight. This data is cataloged and routed straight into telemarketing lists and messaging spam rings. - The Malicious App Vector (
PROMO DOWNLOAD APK): Right below the account controls sits an eye-catching download link prompting visitors to install an Android package (.apk). Because this application bypasses legitimate app repositories, it avoids malware security audits. - One-Way Inbound Transactions: Players fund their profiles through peer-to-peer crypto transfers, unregulated payment gateways, or unmonitored digital wallets. The moment funds clear, they pass beyond the reach of standard dispute systems or banking chargeback protocols.
- The Payout Barrier: If a player attempts to cash out their balance, the platform stonewalls them. The operators impose fabricated turnover rules, demand secondary “administrative deposits,” claim technical glitches, or simply delete the profile without recourse.
5 Major Red Flags Identified on Empirel.fit
1. High-Risk Mobile Software Sideloading
Directing users to install an unofficial Android APK is a severe security red flag. Sideloading software outside official app stores bypasses default operating system protections. These files can covertly package keystroke loggers, spyware, or background services designed to intercept two-factor SMS codes and monitor banking notifications.
2. Fabricated Payout Percentages
Claiming a 98.9% return rate is mathematically deceptive. Authentic, regulated developers—such as Pragmatic Play, Playtech, or NetEnt—certify slot titles within rigid statistical ranges, generally between 94% and 97%. Any portal advertising near-guaranteed wins runs pirated game clones with rigged outcome engines.
3. Total Absence of Verifiable Regulatory Licensing
Regulated platforms must prominently present a verifiable license issued by recognized gaming authorities (like the Malta Gaming Authority, UKGC, or Curacao Gaming Control Board). Empirel.fit provides no license number, no registered corporate entity, and no traceable headquarters address.
4. Disposable Domain-Churn Setup
Legitimate financial and entertainment platforms do not establish their core services on throwaway extensions like .fit. The use of this TLD indicates that the domain is treated as expendable infrastructure, waiting to be dropped the moment it gets flagged by web protection databases.
5. Non-Existent Consumer Protections and Fair Play Audits
The website fails to supply enforceable terms of service, an official privacy policy, or responsible gambling controls (such as self-exclusion or deposit limits). Moreover, it lacks audit seals from recognized testing agencies like eCOGRA, BMM Testlabs, or iTech Labs.
Practical Steps to Secure Your Accounts and Devices
If you have already entered personal details or interacted with Empirel.fit, implement these countermeasures right away:
- Cut Off All Further Transactions: Never yield to demands for secondary “activation fees,” “tax clearances,” or extra deposits to unlock a withdrawal. Any additional money sent to an unregulated portal will be permanently lost.
- Delete Unofficial APK Files: If you installed software via the site’s promotional link, remove it from your device immediately. Reboot your phone into safe mode, run a deep scan using an established mobile anti-malware application, and inspect system permissions to revoke unintended SMS and Accessibility access.
- Reset Reused Passwords: If the password entered during registration matches credentials used elsewhere, update those accounts immediately and transition from SMS verification to an app-based authenticator (such as Google Authenticator or hardware keys).
- Alert Your Bank or Wallet Provider: If you entered debit card numbers or bank account credentials, notify your financial institution’s fraud desk to block unauthorized transactions and monitor for illicit recurring charges.
Frequently Asked Questions (FAQ)
1. Is Empirel.fit scam?
Yes, Empirel.fit operates as an offshore online gambling mirror scam. It lacks regulatory oversight, makes false promises of guaranteed payouts, conceals its actual ownership, and promotes unverified mobile software downloads.
2. Is Empirel.fit legit?
No, Empirel.fit is completely illegitimate. It holds no recognized gaming licenses, publishes no authentic legal policies, and serves solely as a temporary gateway for unregulated offshore gambling rings.
3. What is an offshore online gambling mirror site?
An offshore online gambling mirror site is a throwaway duplicate or proxy web address used by unauthorized casino networks. It allows operators to circumvent regional ISP blocks and search engine restrictions to keep funneling players into shadow betting servers.
4. Why is downloading the APK from Empirel.fit dangerous?
Downloading unsigned APK packages directly from mirror portals circumvents standard mobile app security scans. These files can carry malicious code capable of harvesting keystrokes, recording credentials, and intercepting two-factor authentication SMS messages.
5. Can any slot game truly provide a 98.9% win rate?
No. Regulated slots are mathematically calibrated with an unavoidable house edge, yielding average returns between 94% and 97%. A site advertising a 98.9% win rate is using deceptive figures to lure in deposits.
6. What should you do if Empirel.fit locks your funds?
Do not send more money. Fraudulent portals routinely claim that additional payments are required to “clear” or “unlock” an account. These claims are traps; legitimate casinos never require users to deposit extra cash simply to withdraw their existing balance.
7. Why do operators keep switching between domains like .fit, .lol, and .lat?
Non-traditional domain extensions are cheap and simple to register in bulk. When cybersecurity tools or government agencies block one specific link, operators can immediately route traffic to a replacement mirror without interrupting their revenue stream.
8. How can I confirm that an online casino is actually safe and legal?
Always verify that the website holds an active license from an established regulatory commission, with an authentic link back to that regulator’s official register. Legitimate operators also disclose clear physical company details, undergo independent software audits, and host their mobile applications inside authorized app stores.
Every safe click counts. If this post helped, a coffee gesture fuels more scam‑busting investigations.

Help Us Spread Awareness
Please share this article to spread awareness. Follow us on social media for more scam alerts.