Sojuara.lol Under the Microscope: Anatomy of an Offshore Online Gambling Landing Portal/Mirror Scam
Encountering a suspicious portal like Sojuara.lol highlights the aggressive rise of the offshore online gambling landing portal/mirror scam, designed to funnel unsuspecting players into shadow betting networks. These stripped-down entry domains appear across search redirects, Telegram channels, and social media promotions, bypassing regional cybersecurity barriers to harvest user credentials and deposits.
Rather than delivering a secure, licensed gaming experience, landing on Sojuara.lol puts your personal information and financial assets at immediate risk. Behind its minimalist, cyber-grid interface lies an unregulated operation running without consumer protection, transparency, or legal accountability.
What Is an Offshore Online Gambling Landing Portal/Mirror Scam?
To evaluate the risks of domains like Sojuara.lol, you must understand the underlying framework of an offshore online gambling landing portal/mirror scam.
In heavily supervised regions, regulatory watchdogs, internet service providers (ISPs), and search engines continually flag, penalize, and blacklist unauthorized casino operations. Because illicit syndicates cannot keep a primary web address active for long, they rely on domain churn strategies.
Operators purchase dozens of inexpensive, throwaway domains featuring unconventional top-level domains (TLDs) such as .lol, .lat, or .xyz. These URLs serve as mirror portals—disposable jump stations that accomplish three key objectives:
- Circumventing DNS and ISP Firewalls: When telecom networks block a primary server, the syndicate distributes fresh alternative mirror links so users can still reach the platform.
- Cloaking Shadow Operations: Minimalist landing pages hide intrusive casino scripts from automated anti-phishing crawlers and advertising bots until the visitor interacts with the page.
- Flipping Traffic to Unlicensed Backends: The portal serves as a frontend interface that silently pipes player logins, registration details, and payment commands to an offshore server database.
Once cybersecurity platforms blackmark a domain, the operators burn it and roll out an identical template on another URL within hours.
Suspicious Link or Courier SMS?
Verify URLs, APKs, or parcel alerts against our threat database before clicking.
Case Study: Deconstructing Sojuara.lol
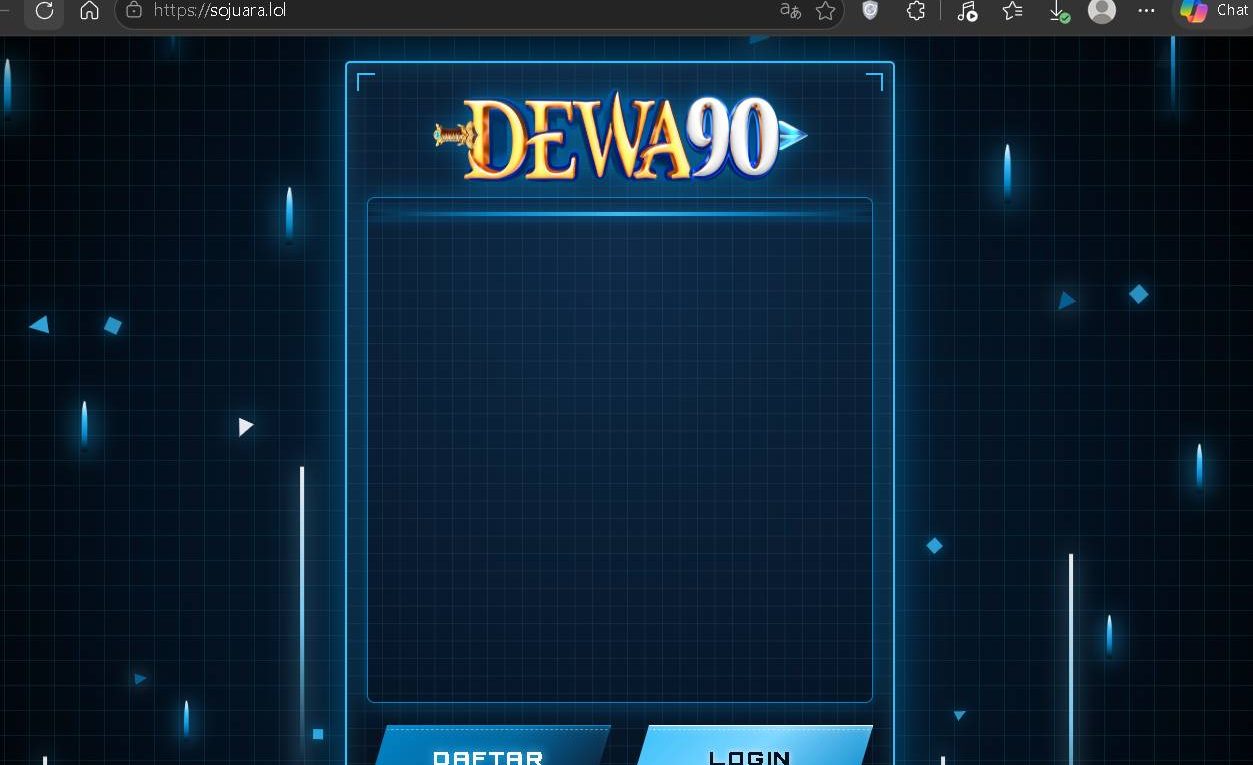
Sojuara.lol provides an unmistakable look at how modern illegal gambling syndicates strip away all unnecessary web assets to optimize for speed, evasion, and credential capture.
[User Arrives at Sojuara.lol]
             │
             ▼
[Branded Header: DEWA90 Syndicate]
             │
             ├──► [DAFTAR Button] ──► Exposes PII to Unregulated Telemarketing Lists
             │
             └──► [LOGIN Button]  ──► Routes Credentials to Shadow Database
Visual Shell and Promoted Identity
When you open Sojuara.lol, you are not presented with game previews, customer support widgets, or standard corporate documentation. Instead, the site displays:
- A sci-fi neon grid frame and a dark blue space-themed background.
- The glowing emblem of DEWA90, an offshore Asian slot and sports-betting network frequently tied to unlicensed gaming syndicates.
- Two isolated call-to-action buttons: DAFTAR (Register) and LOGIN.
Behind the Scenes: How the Site Operates
- Data Ingestion via “DAFTAR”: Clicking the registration button opens an unencrypted or loosely secured data-capture form. Prospective players submit sensitive information—including active telephone numbers, full legal names, WhatsApp handles, and local banking or e-wallet account details. This data is channeled straight into syndicate databases.
- Shadow Routing via “LOGIN”: Existing members entering credentials through the login module are authenticated against offshore databases without independent fraud prevention or encryption standards, leaving passwords vulnerable to credential stuffing attacks.
- One-Way Payment Funnels: Once inside, deposits flow through peer-to-peer crypto transfers, illicit bank transfers, or unmonitored digital wallets. Once money is transferred into these offshore accounts, all standard financial chargeback protections and dispute channels disappear.
- The Payout Deadlock: While adding funds is made effortless, cashing out is routinely thwarted. Unregulated networks commonly lock player accounts, demand bogus “clearance taxes,” claim violations of non-existent wagering rules, or stop responding altogether.
5 Serious Red Flags Uncovered on Sojuara.lol
1. Direct Affiliation with the Unregulated DEWA90 Syndicate
The platform prominently features the DEWA90 logo. This operator lacks accreditation from recognized bodies such as the Malta Gaming Authority (MGA), the UK Gambling Commission (UKGC), or the Curacao Gaming Control Board. Playing on an unlicensed platform strips away all legal recourse in the event of withheld funds.
2. Disposable Domain Infrastructure (.lol Churn)
Legitimate commercial businesses invest in permanent, brand-protected web properties. Operating under a cheap .lol TLD is a prime hallmark of disposable mirror operations designed to be discarded the moment regional telecommunications authorities enforce blacklists.
3. Absolute Void of Legal Disclosures and Terms
The landing page on Sojuara.lol contains no verifiable registered office address, company registration numbers, terms and conditions, privacy policy, or responsible gaming resources. You are handing over financial details to completely anonymous actors.
4. High Exposure to Telemarketing and Identity Harassment
Submitting personal contact information into the “DAFTAR” form exposes your identity to shadow data brokers. Numbers collected on these mirrors are routinely added to aggressive telemarketing funnels, resulting in endless spam texts, automated phone calls, and phishing attempts on messaging apps like WhatsApp and Telegram.
5. Absence of Independent Fair-Play Testing
Legitimate casino games use certified Random Number Generators (RNGs) tested and audited by independent testing houses like eCOGRA, BMM Testlabs, or iTech Labs. Syndicates linked to mirror setups often run copied or altered game code, allowing administrators to rig winning odds and keep player balances perpetually suppressed.
Direct Action Plan: Safeguarding Your Security
If you have already interacted with Sojuara.lol, follow these immediate recovery steps:
- Cease All Deposits: Never transfer additional capital to “unlock” an account, clear pending bonuses, or pay withdrawal verification fees. Any additional deposit will also be lost.
- Change Shared Passwords: If you registered using a password you also use for other online platforms (such as personal email, cryptocurrency exchanges, or banking accounts), update those passwords immediately and enable authenticator-app 2FA.
- Block Suspicious Communications: Expect incoming spam calls and messages offering “exclusive bonuses” or “guaranteed slot patterns.” Block and report these senders without clicking any shared links.
- Notify Your Financial Institution: If you disclosed banking account or debit card details, alert your bank’s fraud prevention department to monitor your account for unauthorized charges.
Frequently Asked Questions (FAQ)
1. Is Sojuara.lol scam?
Yes, Sojuara.lol exhibits the operational characteristics of an online gambling mirror scam. It operates as an unlicensed gateway for the Dewa90 syndicate without regulatory oversight, consumer protections, or verifiable payout mechanisms.
2. Is Sojuara.lol legit?
No, Sojuara.lol is not a legit gaming portal. It does not hold a valid gambling license, provides no ownership transparency, and uses a disposable domain setup to evade regulatory web blocks.
3. What is an offshore online gambling mirror site?
An offshore gambling mirror site is an alternative clone domain used by unlicensed betting operators to bypass regional ISP blocks and search engine restrictions, seamlessly channeling visitors to unregulated backend servers.
The site uses a bare-bones layout to keep page weight minimal, reduce server overhead, and capture user credentials quickly while evading content analysis algorithms run by cybersecurity search crawlers.
5. What happens if I register my phone number on Sojuara.lol?
Your phone number and submitted details are saved to an unregulated syndicate database. This typically results in persistent spam calls, suspicious SMS marketing, and phishing links across messaging platforms like WhatsApp and Telegram.
6. Can you withdraw winnings from Dewa90 mirrors like Sojuara.lol?
Withdrawing funds from unregulated mirrors is exceptionally risky. Players often encounter arbitrary account freezes, demands for upfront verification fees, or fabricated violations of bonus rules designed to block payouts.
7. Why do gambling syndicates use the .lol domain extension?
Syndicates buy .lol domains in bulk because they are inexpensive and easy to acquire. When one domain gets added to government or ISP blocklists, operators can direct traffic to another mirror within minutes.
8. How can I verify if an online casino platform is legally licensed?
A legitimate platform displays verifiable corporate licensing numbers with direct links to the public registry of an established regulator (such as MGA or UKGC), undergoes third-party software audits, and publishes transparent terms and conditions.
Every safe click counts. If this post helped, a coffee gesture fuels more scam‑busting investigations.

Help Us Spread Awareness
Please share this article to spread awareness. Follow us on social media for more scam alerts.