Pradab.lat Review: Legit Gaming Hub or BalakSix Syndicate Trap?
Threat Classification & Urgent Reader Triage
Pradab.lat is an unlicensed, high-risk predatory gambling landing page operating as an ephemeral frontend mirror for the offshore “BalakSix” syndicate. The domain functions not as a compliant casino operator, but as an evasive intake node engineered to siphon retail deposits directly into unverified peer-to-peer payment rails, trapping user capital behind fabricated withdrawal obstacles.
🛑 Emergency Action Protocol
- If you have not deposited: Close this website immediately. The advertised 98,1% win rate is an unverified cosmetic script, and the platform possesses zero statutory licensing or player capital protections.
- If your balance is stuck: Do not send additional capital. Demands for “AML audit clearance,” “TDS tax deposits,” or “VIP withdrawal activation” are advance-fee extortion scams; sending more money will not release your funds.
- If you sent money or your bank account shows a freeze: You may be entangled in a cyber cell debit freeze triggered by illicit transaction pooling. Read Wisdom Ganga’s authoritative guide on online casino domain churn scams and fund recovery immediately to initiate 1930 golden-hour reporting and execute proper legal containment under Section 106 BNSS / 102 CrPC.
Forensic Evidence Matrix
[ TARGET AUDIT RECORD: PRADAB.LAT ]
-----------------------------------------------------------------------------------------
Domain Entity         : https://pradab.lat (Registry: .lat regional gTLD)
Operating Pseudonym   : BalakSix / Slot Gacor
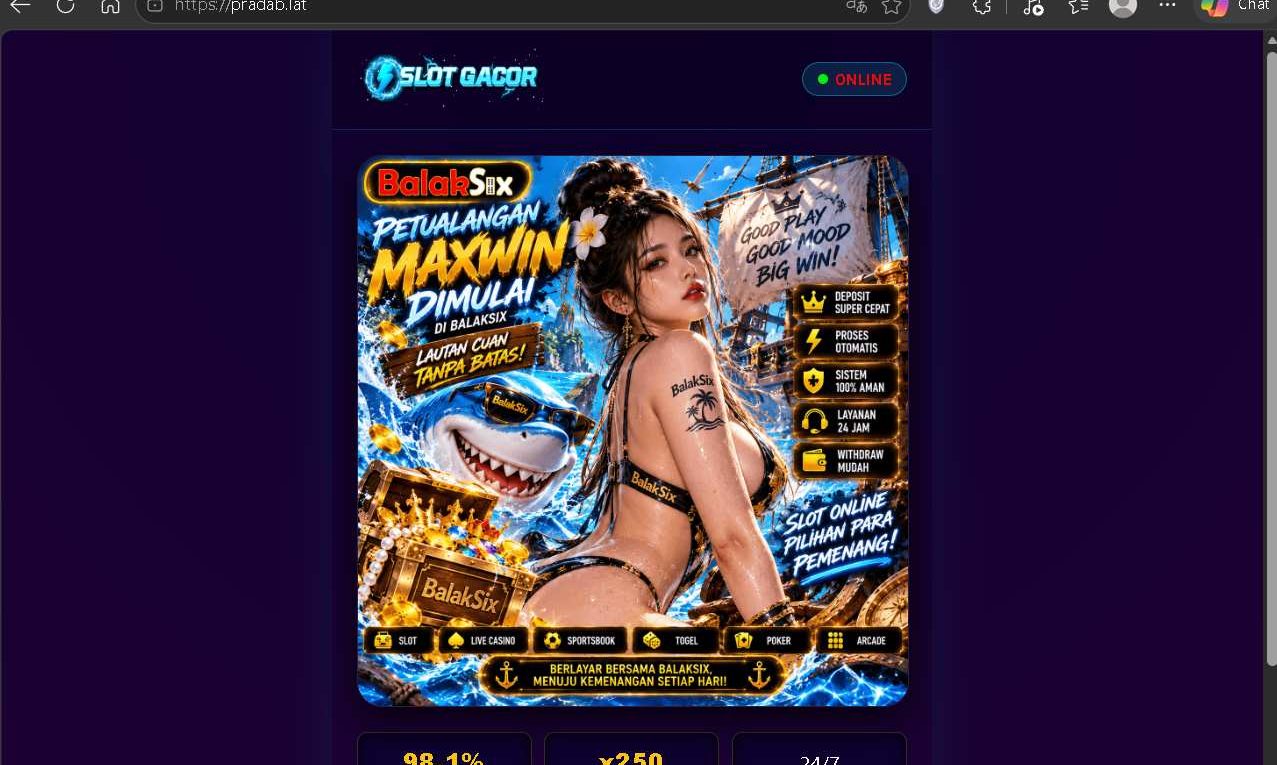
Visual Focal Points   : AI pirate character, branded shark mascot, open doubloon chest
Linguistic Triggers   : "Petualangan Maxwin Dimulai di BalakSix"
                        "Lautan Cuan Tanpa Batas!"
                        "Berlayar Bersama BalakSix, Menuju Kemenangan Setiap Hari!"
Fabricated Metrics    : 98,1% Win Rate | x250 Multiplier | 24/7 Support
Purported Guarantees  : Deposit Super Cepat, Proses Otomatis, Sistem 100% Aman,
                        Layanan 24 Jam, Withdraw Mudah
Faux Category Links   : SLOT, LIVE CASINO, SPORTSBOOK, TOGEL, POKER, ARCADE
Telemetry State       : "● ONLINE" status beacon with live chat injection
Licensing Credentials : NONE (Unregulated across RBI, MeitY, CERT-In, MGA, Curaçao)
Artifact Deconstruction: Visual Lures & Infrastructure Camouflage
Domain Syntax & TLD Exploitation
The use of pradab.lat illustrates how cyber syndicates exploit cheap, automated domain registries. The .lat top-level domain—historically aimed at Latin American digital properties—is frequently leveraged by fast-flux networks due to low retail acquisition costs and automated provisioning APIs that lack strict Know-Your-Customer (KYC) identity validation.
This naming architecture is designed for disposable turnover. Because search engines, antivirus web filters, and telecom regulators quickly blacklist flagged gambling mirrors, the backend reverse-proxy infrastructure is pre-configured to migrate incoming traffic to alternate alphanumeric iterations the moment pradab.lat receives an ISP block. To examine the structural mechanisms of how syndicates rotate identical frontends across rotating hosts, review our technical teardown of fast-flux casino domain churn syndicates.
Behavioral Engineering: The “BalakSix” Pirate Camouflage
The landing page relies on calculated visual framing to lower a player’s natural financial suspicion:
- The Wealth Adventure Narrative: By centering the page around an AI-generated pirate theme—complete with a model displaying a “BalakSix” tattoo, an animated pirate shark, and a chest overflowing with gold coins—the operators reframe high-loss mathematical gambling as an adventurous treasure hunt (“Lautan Cuan Tanpa Batas” / Limitless Sea of Profit).
- The Static Trust Badge Wall: The right rail stacks five reassurance triggers:
DEPOSIT SUPER CEPAT,PROSES OTOMATIS,SISTEM 100% AMAN,LAYANAN 24 JAM, andWITHDRAW MUDAH. These are not interactive or verified security credentials; they are static graphic overlays intended to mimic modern digital banking checkouts without any underlying compliance audits. - The Impossible 98,1% Metric: Prominently displaying a platform-wide 98,1% win rate is an actuarial impossibility. Licensed, certified gaming houses run individual Return-to-Player (RTP) game algorithms independently audited by labs like eCOGRA or BMM Testlabs; presenting an unvarying 98,1% success rate is a fraudulent metric designed to entice inexperienced retail depositors.
Suspicious Link or Courier SMS?
Verify URLs, APKs, or parcel alerts against our threat database before clicking.
Cross-Border Operational Inconsistencies
The user interface is built entirely with Indonesian iGaming phrasing—including colloquial hooks like “Slot Gacor”, “Maxwin”, and “Togel”. However, these turnkey syndicates systematically blast links via rogue Telegram channels, compromised social handles, and surrogate sports-streaming feeds into overseas markets, including India. When foreign players access the gateway, the backend routes their payments through localized peer-to-peer rails (such as Indian UPI VPAs or local e-wallets) while the frontend remains locked to its residual Southeast Asian template assets.
The Technical Trap: How Funds Disappear
Victim Initiates Deposit
           │
           ▼
[ Rotating P2P Mule VPA / Bank Account ] ──> Automated Laundering Layering (Crypto / Off-ramp)
           │
           ▼
[ Rigged In-Browser Script Runs ] ──> Displays Simulated "Big Win" Balance
           │
           ▼
Victim Clicks "Withdraw" ──> Automated Engine Halts Transaction
           │
           ▼
[ Advance-Fee Extortion: Fake TDS Tax / AML Audit Demanded ] ──> Complete Loss
Scripted Visual Engines vs. Audited Gaming Feeds
Legitimate online casinos never host games locally on disposable landing pages; they stream them via secure, authenticated iframes from certified game developer servers. Pradab.lat provides no authenticated connection to real studio backends. The vertical tabs for LIVE CASINO, POKER, and SPORTSBOOK serve as navigational facades. Any game presented is a client-side animation loop where outcome percentages are altered to produce immediate, simulated wins that build artificial confidence before systematically clearing out higher deposits.
P2P Mule Account Money Laundering
When a player transfers funds, the money does not enter a corporate merchant account protected by payment escrow. Instead, the checkout screen surfaces temporary P2P mule accounts or individual UPI Virtual Payment Addresses (VPAs). Once funds settle, syndicate scripts immediately fragment the deposit across a chain of secondary accounts before converting the balance into unhosted cryptocurrency, breaking the transactional audit trail.
The Advance-Fee Withdrawal Lock
The platform’s promise of WITHDRAW MUDAH (Easy Withdrawal) collapses as soon as a user requests an outbound transfer. The automated ledger freezes the request, prompting support agents to assert that the player’s account has encountered a compliance hold. The victim is told that depositing an extra 20% to 30% for “TDS tax clearance” or an “Anti-Money Laundering audit deposit” will unblock the channel. This is an advance-fee fraud loop; the site has no automated payout gateway, and transferring additional funds will only compound the financial loss.
Frequently Asked Questions (FAQ)
Is Pradab.lat scam?
Yes, Pradab.lat is an outright scam. It operates as an unlicensed, disposable frontend that uses fabricated 98,1% win-rate statistics, fake category feeds, and advance-fee withdrawal blocks to steal deposits.
Is Pradab.lat legit?
No, Pradab.lat is not legit. It holds zero valid gaming licenses from regulators like MeitY, MGA, or Curaçao, conceals its operator identity behind offshore proxy registries, and operates in violation of financial compliance frameworks.
Why is customer support demanding a tax or verification fee to release my withdrawal?
Demanding upfront payments to release an existing balance is an advance-fee fraud mechanic. Real financial institutions and legitimate gaming operators automatically deduct applicable taxes at source (TDS) from your running balance; they never demand out-of-pocket deposits as a prerequisite for processing a withdrawal.
Because UPI transactions clear instantly, banks cannot execute immediate manual pullbacks once a transfer is finalized. However, you should immediately file a dispute via the 1930 national cybercrime helpline and register your complaint at cybercrime.gov.in. Reporting during the golden-hour window gives cyber investigators the highest chance of freezing the recipient mule account before the syndicate off-ramps the funds.
Why did my bank account receive a cyber cell lien/freeze after using this platform?
Because deposits on Pradab.lat pass through illicit peer-to-peer mule networks, your account becomes an interconnected node in an active money-laundering investigation. When state Cyber Cells track these syndicates, they issue automated debit freeze and lien orders under Section 106 BNSS / Section 102 CrPC across all associated accounts. For actionable steps on contacting the investigating officer and securing an official Police NOC, consult our guide on resolving cyber cell bank liens and domain churn scams.
Every safe click counts. If this post helped, a coffee gesture fuels more scam‑busting investigations.

Help Us Spread Awareness
Please share this article to spread awareness. Follow us on social media for more scam alerts.