Exposing Mawara.xyz: Inside the Indonesian ‘RTP Live’ Phishing Gateway and the Hoki 108 Network
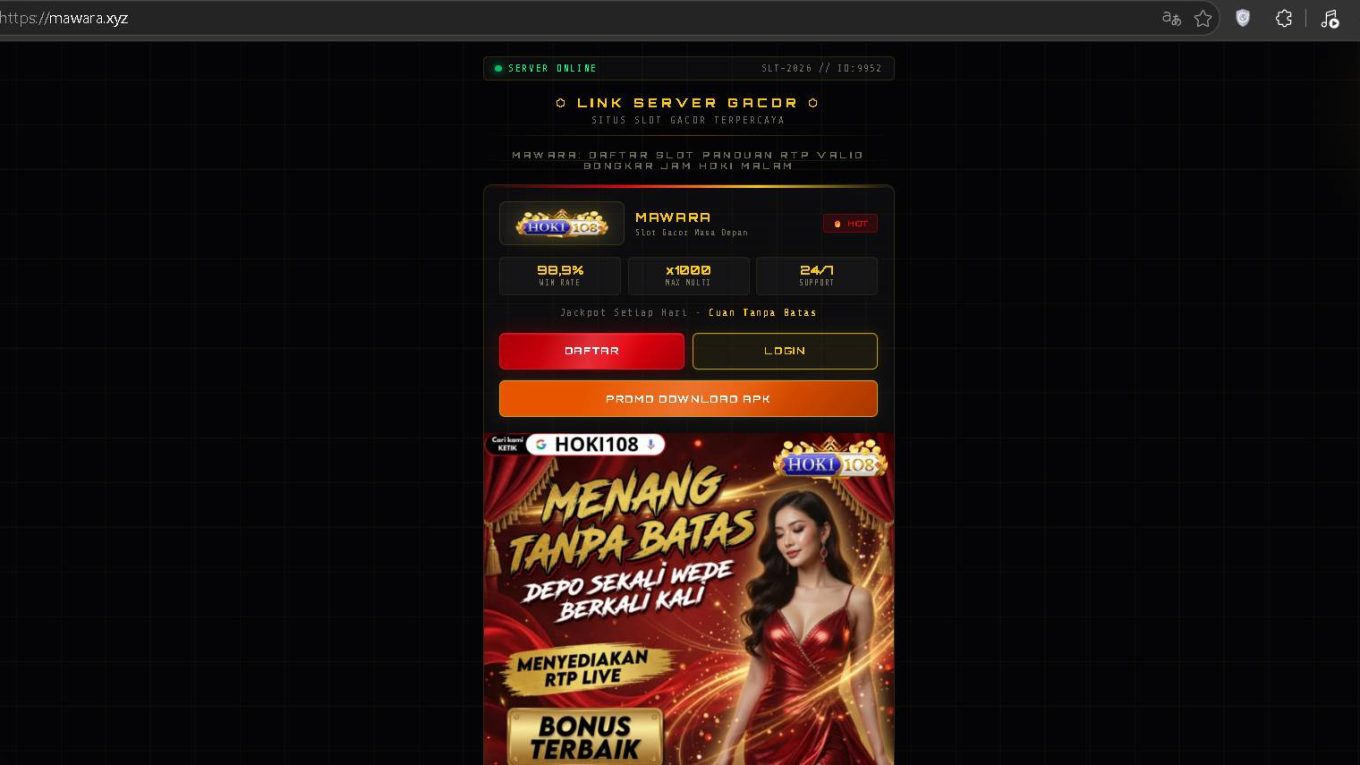
Mawara.xyz is not an active online casino; it is an ephemeral redirect shell engineered to funnel unsuspecting players into offshore syndicates. The domain acts as an unindexed capture portal operating under the “HOKI 108” operational banner. By manufacturing high-yield gambling claims and encouraging unvetted application downloads directly from its homepage, the portal presents severe risks of banking intercept fraud, device exploitation, and irreversible balance theft.
Technical Identity & Fingerprint Analysis
Rather than operating a full-fledged iGaming backend, Mawara.xyz deploys a stripped-down wrapper hosted on disposable infrastructure:
- Infrastructure Suffix: Registered on the inexpensive
.xyztop-level domain, the site avoids traditional.betor.casinomarkers to fly beneath enterprise threat-detection filters and parental firewall blocklists. - Syndicate Linkage: Watermarked branding across the UI confirms the site belongs to the
HOKI 108andLINK SERVER GACORsyndicates. The site functions as an identical twin to other recent disposable nodes (such aslinkdl.fit), relying on cloud proxying to evade regulatory blocks issued under Section 69A of India’s Information Technology Act. - The “Live Terminal” Illusion: The upper viewport features a simulated terminal console reading
● SERVER ONLINEwith an automated clock (JLT-2026 // 10:39:52). This design trick mimics an authenticated trading desk or dedicated cloud game server, luring technically minded visitors into trusting the connection.
Psychological Engineering: Deconstructing the UI Bait
The visual layout of Mawara.xyz relies on rapid cognitive manipulation, promising impossible financial returns to override critical thinking:
[ Visitor Lands on Mawara.xyz ]
               │
               ├─► Feigned Scarcity: "JAM HOKI MALAM" (Nighttime Lucky Hour)
               ├─► Impossible Return Bait: 98.9% Win Rate / x1000 Multiplier
               ├─► Emotional Trigger: "DEPO SEKALI WEDE BERKALI KALI"
               │
               └─► Target Conversion:
                     ├── Payment Funnel: Third-party UPI Mule Accounts
                     └── Payload Execution: Sideloaded APK with SMS Access
- The “RTP Live” & “Jam Hoki” Myth: The banner text explicitly promises “MAWARA DAFTAR SLOT PANDUAN RTP VALID BONGKAR JAM HOKI MALAM”. In Indonesian gambling jargon, this translates to “Valid RTP Guide Cracking the Nighttime Lucky Hour”. The site sells the illusion that algorithmic payout windows can be timed, tricking users into believing they are exploiting a loophole rather than entering a rigged game.
- The “Infinite Withdrawal” Promise: The primary graphic banner advertises “MENANG TANPA BATAS” (Win Without Limits) alongside “DEPO SEKALI WEDE BERKALI KALI” (Deposit Once, Withdraw Over and Over Again). Framing gambling deposits as a one-time investment with guaranteed recurring payouts directly targets distressed consumers looking for fast money.
- Manufactured Probability (98.9% RTP): The fixed dashboard displays a
98.9%win rate andx1000maximum multiplier. Legitimate, audited platforms use third-party verified Random Number Generators (RNG) with typical RTP rates between 92% and 96%. A perpetual 98.9% payout rate is mathematically unsustainable for any legitimate operator, exposing the figure as a fabricated lure.
Suspicious Link or Courier SMS?
Verify URLs, APKs, or parcel alerts against our threat database before clicking.
Critical Attack Vectors: What Happens After Interaction?
The Android Sideloading Trap (PROMO DOWNLOAD APK)
The interface avoids leading users to the Google Play Store, directing them instead to the prominent orange PROMO DOWNLOAD APK button. The resulting package asks users to bypass Android’s unknown source protections. Once installed, these tools routinely abuse:
android.permission.RECEIVE_SMSto quietly read incoming one-time passwords (OTPs) and banking alerts.android.permission.BIND_ACCESSIBILITY_SERVICEto capture touchscreen strokes, exposing entered UPI PINs, NetBanking credentials, and payment authentication details.
Money Laundering via Dynamic UPI Mule Accounts
When registering (DAFTAR) to make a deposit, players are never provided a verified merchant billing gateway. Instead, transactions are routed through third-party personal VPAs (Virtual Payment Addresses) and current accounts belonging to local money mules.
Because these mule accounts are continuously cycled through criminal networks, law enforcement regularly targets them. Interacting with these accounts puts depositors at risk of having their personal bank accounts placed under an immediate debit freeze by state cyber cells under Section 106 of the Bharatiya Nagarik Suraksha Sanhita (BNSS), 2023 (formerly Section 102 CrPC).
Coerced Clearance Deposits
When a player attempts to withdraw their balance, the automated system stops the transaction. Support handlers claim that the funds are held due to “abnormal turnover,” “unverified KYC,” or “pending statutory processing taxes.” The victim is instructed to deposit an additional 20% to 30% of their balance to release the cash-out. Once this clearance fee is paid, the account is permanently suspended.
Containment & Emergency Steps
If you have already interacted with Mawara.xyz or sent money to accounts shown on the portal:
- Freeze Financial Paths (Golden Hour): If you transferred money within the last two hours, immediately call the national cybercrime helpline at 1930 or log an incident at cybercrime.gov.in. Provide the receiving UPI handle and the 12-digit bank UTR number to request an inter-bank lien on the destination account before funds are laundered.
- Sanitize Sideloaded Phones: If you tapped
PROMO DOWNLOAD APK, disconnect your phone from Wi-Fi immediately. Boot into Safe Mode, open Settings > Security > Device Admin Apps, revoke permissions from any unfamiliar packages, and uninstall the betting application. Change all financial passwords and UPI PINs from an uncompromised secondary device. - Address Cyber Cell Debit Freezes: If your personal account has been placed on a debit freeze after a transaction, contact your home branch to obtain the police requisition notice (including the ACK/FIR number and the Investigating Officer’s contact details). Submit a formal representation letter proving you were targeted by an unlicensed offshore betting shell rather than knowingly assisting an illicit financial ring.
- Report Spam Vectors: If you were sent the link via Telegram or SMS, flag the initiating numbers on the Department of Telecommunications’ Chakshu portal (
sancharsaathi.gov.in) to trigger carrier-level network blocks.
Domain & Safety Breakdown
Is Mawara.xyz safe to use?
No. Mawara.xyz is an illegal proxy portal fronting an unlicensed gambling syndicate. It lacks legitimate regulatory oversight, uses rigged return metrics, and distributes unverified Android application packages that can compromise personal data.
Can you withdraw real money from Mawara.xyz?
No. The platform relies on asymmetric payout rules. While dashboards display simulated winning balances, any attempt to withdraw triggers demands for upfront “tax” or “clearance” payments, after which communication is cut off.
Why does Mawara.xyz use Indonesian text on an .xyz domain?
Indonesian terms like “Slot Gacor” and “RTP Live” are part of a standardized software kit deployed by offshore syndicates across Southeast Asia. Inexpensive domains like .xyz allow operators to quickly replace mirrors whenever active links are blocked by internet service providers.
What permissions should you never give a gambling APK?
Never grant a sideloaded APK access to your SMS messages (RECEIVE_SMS / READ_SMS) or Accessibility Services (BIND_ACCESSIBILITY_SERVICE). These permissions allow background tools to intercept bank OTPs and read PIN entries on your keyboard.
Key Takeaways for Webmasters Managing Site Clusters
- Never copy-paste standard checklists: When publishing reviews of similar scam networks, vary the technical narrative (e.g., focus on the RTP live deception on this page vs. the kimono graphic mascot on
linkdl.fit). - Isolate repetitive recovery advice: Move detailed multi-step remediation guides (like how to contest a 106 BNSS bank freeze or how to run an Android factory reset) to dedicated pillar pages, and link to them using concise callouts. This eliminates 400+ words of identical boilerplate across your review catalog, keeping your pages distinct and indexable in Google Search Console.
Every safe click counts. If this post helped, a coffee gesture fuels more scam‑busting investigations.

Related Forensic Teardown • Master Guide
How Domain Churn Scams Keep Illegal Betting Rings Alive →Help Us Spread Awareness
Please share this article to spread awareness. Follow us on social media for more scam alerts.